• About Us
  • Privacy Policy
  • Disclaimer
  • Contact Us
AimactGrow
  • Home
  • Technology
  • AI
  • SEO
  • Coding
  • Gaming
  • Cybersecurity
  • Digital marketing
No Result
View All Result
  • Home
  • Technology
  • AI
  • SEO
  • Coding
  • Gaming
  • Cybersecurity
  • Digital marketing
No Result
View All Result
AimactGrow
No Result
View All Result

Home windows RDP permits you to log in utilizing revoked passwords. Microsoft is OK with that.

Admin by Admin
May 1, 2025
Home Technology
Share on FacebookShare on Twitter


The flexibility to make use of a revoked password to log in via RDP happens when a Home windows machine that’s signed in with a Microsoft or Azure account is configured to allow distant desktop entry. In that case, customers can log in over RDP with a devoted password that’s validated in opposition to a regionally saved credential. Alternatively, customers can log in utilizing the credentials for the web account that was used to register to the machine.
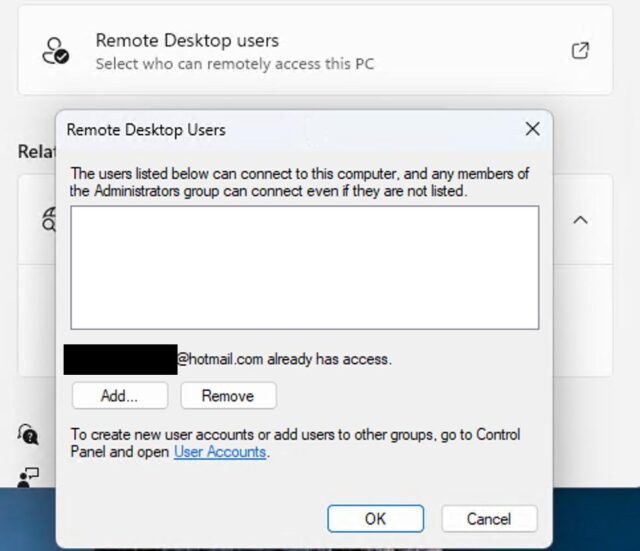
A screenshot of an RDP configuration window exhibiting a Microsoft account (for Hotmail) has distant entry.

Even after customers change their account password, nevertheless, it stays legitimate for RDP logins indefinitely. In some circumstances, Wade reported, a number of older passwords will work whereas newer ones gained’t. The outcome: persistent RDP entry that bypasses cloud verification, multifactor authentication, and Conditional Entry insurance policies.

Wade and one other knowledgeable in Home windows safety mentioned that the little-known habits may show pricey in situations the place a Microsoft or Azure account has been compromised, as an example when the passwords for them have been publicly leaked. In such an occasion, the primary plan of action is to alter the password to stop an adversary from utilizing it to entry delicate assets. Whereas the password change prevents the adversary from logging in to the Microsoft or Azure account, the previous password will give an adversary entry to the consumer’s machine via RDP indefinitely.

“This creates a silent, distant backdoor into any system the place the password was ever cached,” Wade wrote in his report. “Even when the attacker by no means had entry to that system, Home windows will nonetheless belief the password.”

Will Dormann, a senior vulnerability analyst at safety agency Analygence, agreed.

“It would not make sense from a safety perspective,” he wrote in an internet interview. “If I am a sysadmin, I might anticipate that the second I alter the password of an account, then that account’s previous credentials can’t be used wherever. However this isn’t the case.”

Credential caching is an issue

The mechanism that makes all of this doable is credential caching on the arduous drive of the native machine. The primary time a consumer logs in utilizing Microsoft or Azure account credentials, RDP will affirm the password’s validity on-line. Home windows then shops the credential in a cryptographically secured format on the native machine. From then on, Home windows will validate any password entered throughout an RDP login by evaluating it in opposition to the regionally saved credential, with no on-line lookup. With that, the revoked password will nonetheless give distant entry via RDP.

Tags: LetslogMicrosoftPasswordsRDPrevokedWindows
Admin

Admin

Next Post
What’s The Greatest Technique For Your Enterprise?

What's The Greatest Technique For Your Enterprise?

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Recommended.

Know-how often creates jobs for younger, expert staff. Will AI do the identical? | MIT Information

Know-how often creates jobs for younger, expert staff. Will AI do the identical? | MIT Information

May 21, 2026
CISA Flags OT Dangers After Polish Grid Hack

CISA Flags OT Dangers After Polish Grid Hack

February 13, 2026

Trending.

AI & data-driven Starbucks – Deep Brew

AI & data-driven Starbucks – Deep Brew

May 18, 2026
High LLM Observability and Analysis Platforms in 2026: Langfuse, LangSmith, Braintrust, Arize, and Extra In contrast

High LLM Observability and Analysis Platforms in 2026: Langfuse, LangSmith, Braintrust, Arize, and Extra In contrast

August 9, 2026
The Full Information to EcoGPT

The Full Information to EcoGPT

June 6, 2026
Hasbro Information Breach Uncovered Worker Private Data

Hasbro Information Breach Uncovered Worker Private Data

August 30, 2026
7 Greatest Digital Desktop Infrastructure (VDI) Software program (2026): My Picks

7 Greatest Digital Desktop Infrastructure (VDI) Software program (2026): My Picks

September 9, 2026

AimactGrow

Welcome to AimactGrow, your ultimate source for all things technology! Our mission is to provide insightful, up-to-date content on the latest advancements in technology, coding, gaming, digital marketing, SEO, cybersecurity, and artificial intelligence (AI).

Categories

  • AI
  • Coding
  • Cybersecurity
  • Digital marketing
  • Gaming
  • SEO
  • Technology

Recent News

The Pentagon desires $30 million to construct an AI-powered lie detector

The Pentagon needs $30 million to construct an AI-powered lie detector

September 28, 2026
The promise and peril of utilizing visible AI to review cities | MIT Information

The promise and peril of utilizing visible AI to review cities | MIT Information

September 28, 2026
  • About Us
  • Privacy Policy
  • Disclaimer
  • Contact Us

© 2025 https://blog.aimactgrow.com/ - All Rights Reserved

No Result
View All Result
  • Home
  • Technology
  • AI
  • SEO
  • Coding
  • Gaming
  • Cybersecurity
  • Digital marketing

© 2025 https://blog.aimactgrow.com/ - All Rights Reserved