A current Verizon research discovered that vulnerability exploitation grew to become the commonest preliminary entry vector, showing in 31% of breaches. Credential abuse accounted for 13%, whereas ransomware appeared in 48% of breaches, up from 44% the earlier yr.
The Entry Route Obtained Older, Not Smarter
A lot of the present safety dialogue centres on AI-related threats, however Verizon’s knowledge exhibits that identified and unpatched vulnerabilities stay a typical entry level. These flaws are documented, catalogued and infrequently left unresolved for weeks. Securing AI techniques issues, however organizations are nonetheless being breached by way of weaknesses for which fixes exist already.
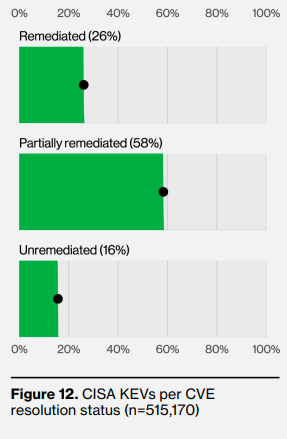
The remediation numbers make the mechanism plain. Verizon discovered that solely 26% of detected vulnerabilities listed in CISA’s Identified Exploited Vulnerabilities catalogue had been totally remediated, down from 38% the earlier yr. The median time to full decision additionally elevated from 32 to 43 days.
The median group was carrying 50% extra crucial vulnerabilities than it had been twelve months earlier.
TrendAI discovered that 70.14% of requested exploits focused vulnerabilities disclosed greater than two years earlier, whereas almost 8% concerned flaws between 10 and 15 years outdated. It additionally discovered that 31% of requested exploits involved vulnerabilities already listed in CISA’s KEV catalogue. Individually, greater than 270,000 techniques remained uncovered to CVE-2020-0796 as of February 2026, six years after its disclosure.
What sits between these two details is an interval. A vulnerability will get printed, catalogued and understood, after which nothing adjustments on the fleet for weeks.
“Handbook work is the brand new assault floor,” says Ryan Braunstein, Safety Supervisor at Automox. “Each handbook activity, whether or not it’s managing tickets, monitoring spreadsheets, or manually patching techniques, gives additional time for an attacker to use one thing.”
A remediation window isn’t a undertaking timeline. It’s a interval throughout which a documented, publicly enumerated weak spot stays out there to anybody studying the identical catalog defenders learn. The asymmetry right here is that attackers can act quicker than defenders.
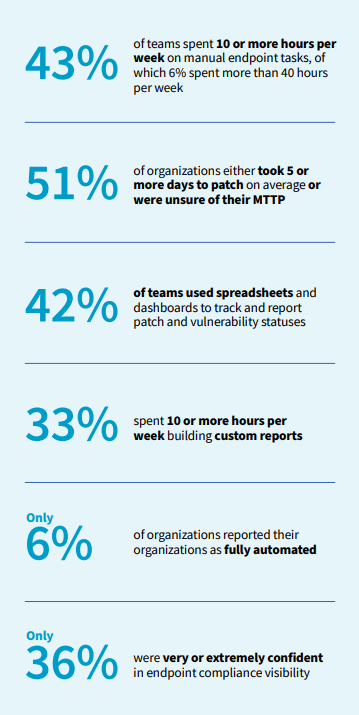
That interval is measurable, and it’s lengthy. Automox’s 2026 survey of IT professionals found that 51% take 5 or extra days to patch on common or don’t know their imply time to patch in any respect. Roughly 1 in 10 reported an MTTP of below a day.
Quantity Is the Cause Triage Stopped Working
The prioritization bottleneck is a quantity drawback earlier than it’s a judgment drawback. Beazley Safety’s Q2 2026 evaluation discovered disclosed vulnerabilities rose 36% quarter over quarter, following an 18.5% rise the quarter earlier than. Vulnerabilities confirmed as actively exploited and added to CISA’s catalog rose 10% over the identical interval.
That hole is the prioritization drawback acknowledged numerically. The identical evaluation notes that NIST now not enriches each new CVE, which quietly removes a triage enter lots of packages had been constructed on.
The queue outgrew the folks working it, no less than that’s what Automox knowledge exhibits. The corporate’s survey discovered that 43% of groups spend 10 or extra hours every week on handbook endpoint duties and 6% spend greater than 40. Solely 6% describe their group as totally automated and 42% nonetheless monitor patch and vulnerability standing in spreadsheets or dashboards. Requested which single activity they’d automate first, 39% selected patch set up.
With disclosed vulnerability quantity up 36% throughout Q2 and plenty of triage processes nonetheless depending on handbook work, the amount of findings can exceed what present groups can course of.
In July 2026, Automox positioned an integration with Tenable Vulnerability Administration into restricted beta. It imports chosen findings, matches affected belongings with Automox-managed endpoints and separates the outcomes into patchable findings, unmatched findings and unmanaged gadgets. Patch and restart actions nonetheless require overview and affirmation, whereas belongings exterior Automox stay seen as protection gaps.
Automox has additionally utilized this mannequin to vulnerabilities with out an out there patch. In September, the corporate launched an AI-drafted Mitigation Worklet pipeline that produces configuration adjustments and non permanent workarounds. Automox says every draft passes greater than a dozen automated checks and human overview earlier than coming into its Worklet Catalog, with clients deciding whether or not to deploy it. The corporate acknowledges that the system can’t tackle each vulnerability.
The system reads new disclosures and drafts configuration adjustments or non permanent workarounds, every of which clears a dozen or so automated checks and a human overview earlier than it lands within the Worklet Catalog, and clients nonetheless select what runs.
Automox says its pipeline applies greater than a dozen automated checks adopted by human overview, with draft mitigations produced in minutes or hours. The corporate additionally acknowledges that the system can’t tackle each vulnerability.
Patching doesn’t shut each route into a corporation. Sophos’s State of Ransomware 2026 reported that compromised identities featured in 79% of ransomware assaults, whereas malicious electronic mail (26%) and phishing (24%) had been the 2 mostly reported root causes. Exploited vulnerabilities had been now not the main reply amongst respondents.
These figures aren’t straight comparable with Verizon’s breach-wide findings. Sophos surveyed 2,158 organizations that had skilled ransomware in the course of the earlier yr, all with 100 to five,000 workers, whereas Verizon analyzed confirmed breaches throughout a wider dataset. Collectively, the findings present that patching reduces one main entry route however doesn’t tackle identification compromise, malicious electronic mail or phishing.
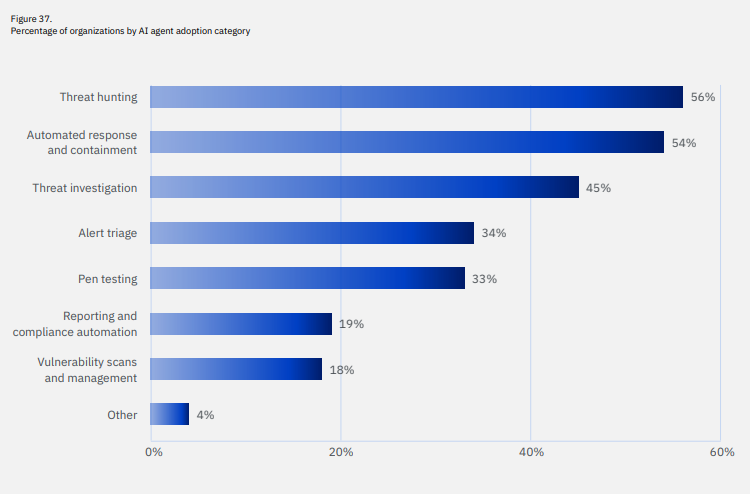
The place machine velocity is being utilized, it’s largely not being utilized right here. IBM’s Value of a Knowledge Breach Report 2026 discovered 50% of organizations now deploy AI brokers someplace within the safety operations heart, however solely 18% apply them to vulnerability scanning and administration. One other 37% say they plan to.
The Boring Funding Is the Defensible One
Probably the most defensible safety spending of the AI period often is the least fascinating. The catalog of what attackers are literally utilizing is printed, free, and up to date repeatedly.
Discovering a vulnerability is just step one. The remaining threat relies on whether or not affected techniques are recognized, prioritised and adjusted earlier than attackers exploit them.