A suspected key member of ShinyHunters identified on-line as “Rey” has been detained in Jordan and is reportedly cooperating with the FBI, days after the hacking group claimed one among its most delicate breaches but: the theft of personnel data belonging to FBI staff.
Jordanian authorities detained Saif al-Din Khader this week, based on three folks conversant in the case who spoke to Reuters. Two sources stated authorities took him into custody Tuesday, and he’s now serving to the FBI and different legislation enforcement companies determine and find different hackers related to the group.
The precise circumstances of Khader’s detention and his present location haven’t been disclosed. The FBI declined to substantiate a particular arrest overseas, however stated it’s persevering with to analyze the current incident allegedly involving ShinyHunters and has already labored with worldwide companions to arrest a number of suspects.
Who Is Rey?
Khader’s alleged identification has been public for nearly a 12 months. In November 2025, cybersecurity journalist Brian Krebs recognized Rey as a young person from Amman, Jordan, allegedly concerned with Scattered LAPSUS$ Hunters, an alliance related to ShinyHunters, Scattered Spider and LAPSUS$. Khader reportedly spoke with Krebs over Sign and claimed on the time that he was leaving information theft and extortion behind.
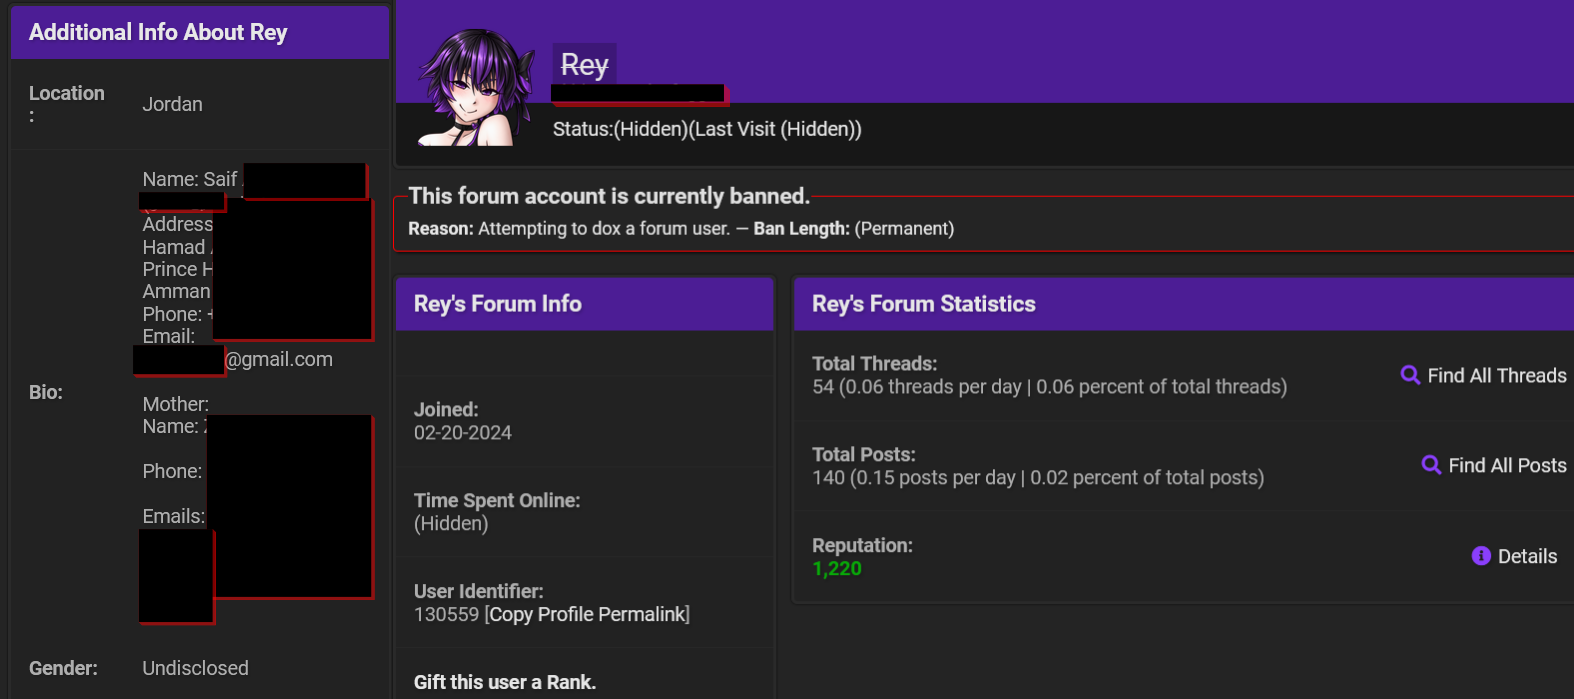
Hackread.com reported on the identification on the time, noting that Rey disputed a number of the claims linking him to the group. More moderen reporting, nevertheless, positioned him a lot nearer to ShinyHunters’ operations. Sources cited by Krebs final month described Rey as having taken management of the ShinyHunters model amid an inside dispute involving Dutch hacker Pepijn van der Stap, also referred to as Umbreon.
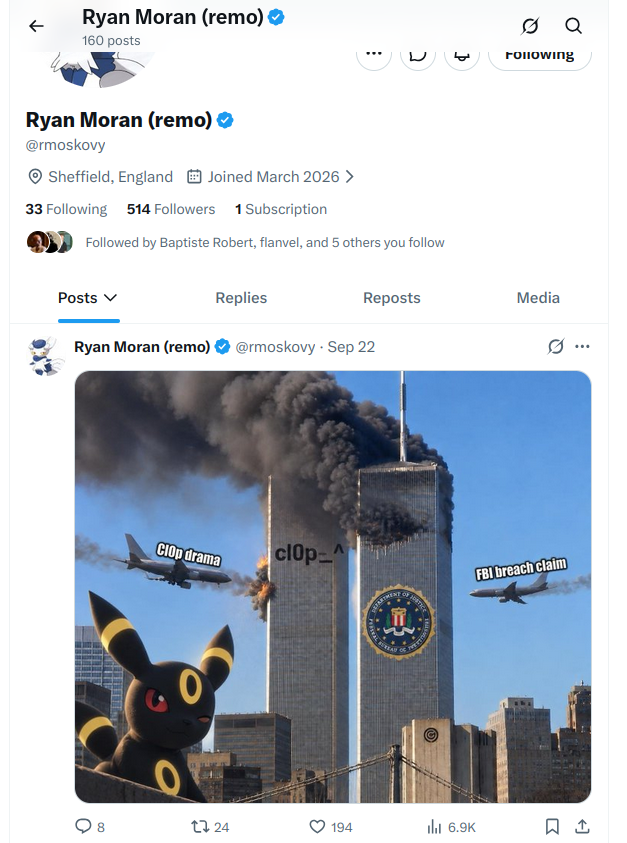
Rey had additionally been publicly taunting the FBI and rival cybercrime teams. Based on Krebs’ report, shortly after the FBI breach turned public, an account linked to him posted materials referencing the assault and the group’s battle with Clop. The account was deleted after Krebs contacted Khader’s father looking for one other interview.
FBI Breach Put ShinyHunters Beneath Intense Stress
The detention follows ShinyHunters’ September assault on the FBI Jobs portal. The group claimed it entered via apply.fbijobs.gov, defaced the positioning and obtained between 2TB and 3TB of knowledge after accessing different programs.
The FBI confirmed that it was investigating unauthorized exercise affecting the roles portal however has not publicly confirmed the complete quantity or contents of the info reportedly obtained.
The contents seem notably delicate. Reuters reviewed samples containing personally identifiable data, job roles and psychiatric and medical data belonging to FBI personnel. An inside FBI memo reportedly instructed employees to imagine each worker might have been uncovered.
ShinyHunters claimed it used an Oracle PeopleSoft vulnerability for the assault. Google Menace Intelligence Group and Mandiant individually documented ShinyHunters, tracked as UNC6240, mass-exploiting CVE-2026-35273 in opposition to PeopleSoft programs.
The flaw was first exploited as a zero-day primarily in opposition to universities earlier than the hackers modified their exploit to bypass WAF guidelines and expanded assaults into authorities, healthcare, expertise, transportation and different sectors.
Hackread.com later obtained an announcement from ShinyHunters saying it had by no means meant to publish or promote the FBI information. The group described its one-week demand for the FBI to right statements about its actions as a “advertising and marketing marketing campaign,” not an extortion deadline.
From Canvas and Rockstar to Massive SaaS Knowledge Theft
The FBI incident adopted an aggressive 12 months for ShinyHunters. In Could, the group focused Instructure’s Canvas studying platform, claiming it stole 3.65TB of knowledge related to almost 9,000 establishments and roughly 275 million customers.
Instructure confirmed uncovered data included names, e-mail addresses, pupil IDs and inside Canvas messages, though the hackers’ bigger figures weren’t independently verified.
The group then defaced Canvas login portals utilized by a whole bunch of colleges and universities, disrupting entry throughout exams and project intervals. Instructure later introduced that it had reached an settlement with the attackers meant to stop publication of the stolen data.
Rockstar Video games was one other goal. ShinyHunters claimed in April that it gained entry to Rockstar’s Snowflake surroundings via credentials or tokens uncovered following a third-party incident involving Anodot.
Rockstar subsequently confirmed {that a} restricted quantity of non-material firm data had been accessed via a third-party breach, whereas saying gamers and its operations have been unaffected.
Google has additionally documented a a lot bigger ShinyHunters-branded marketing campaign involving voice phishing, pretend credential pages and theft from cloud companies together with Salesforce.
The operations focused company SSO credentials and MFA codes earlier than extracting information from SaaS platforms and utilizing it for extortion. Google tracks a number of associated clusters individually as a result of membership and partnerships inside the ShinyHunters infrastructure can change and impersonation can be a priority.
Second Main Detention in Weeks
Khader’s detention follows the September arrest within the Netherlands of Pepijn van der Stap, a beforehand convicted hacker suspected by Dutch investigators of taking part in a job in ShinyHunters. The FBI described Van der Stap as one of many group’s alleged leaders, though ShinyHunters denied to Hackread.com that he had any affiliation with them.
The FBI says ShinyHunters and its alleged co-conspirators have breached greater than 140 organisations since final 12 months and picked up a minimum of $70 million in extortion funds. After the Dutch arrest, FBI Cyber Division Assistant Director Brett Leatherman publicly warned remaining members that arrests and seized infrastructure have been offering investigators with new data.
Occasions this week recommend investigators have been already closing in. Reuters misplaced contact with ShinyHunters via an account beforehand utilized by the group on Tuesday. Its darkish site disappeared Wednesday, shortly after the deadline in its dispute with the FBI expired. The operators later attributed the outage to sabotage by rivals and an unrelated disruption.
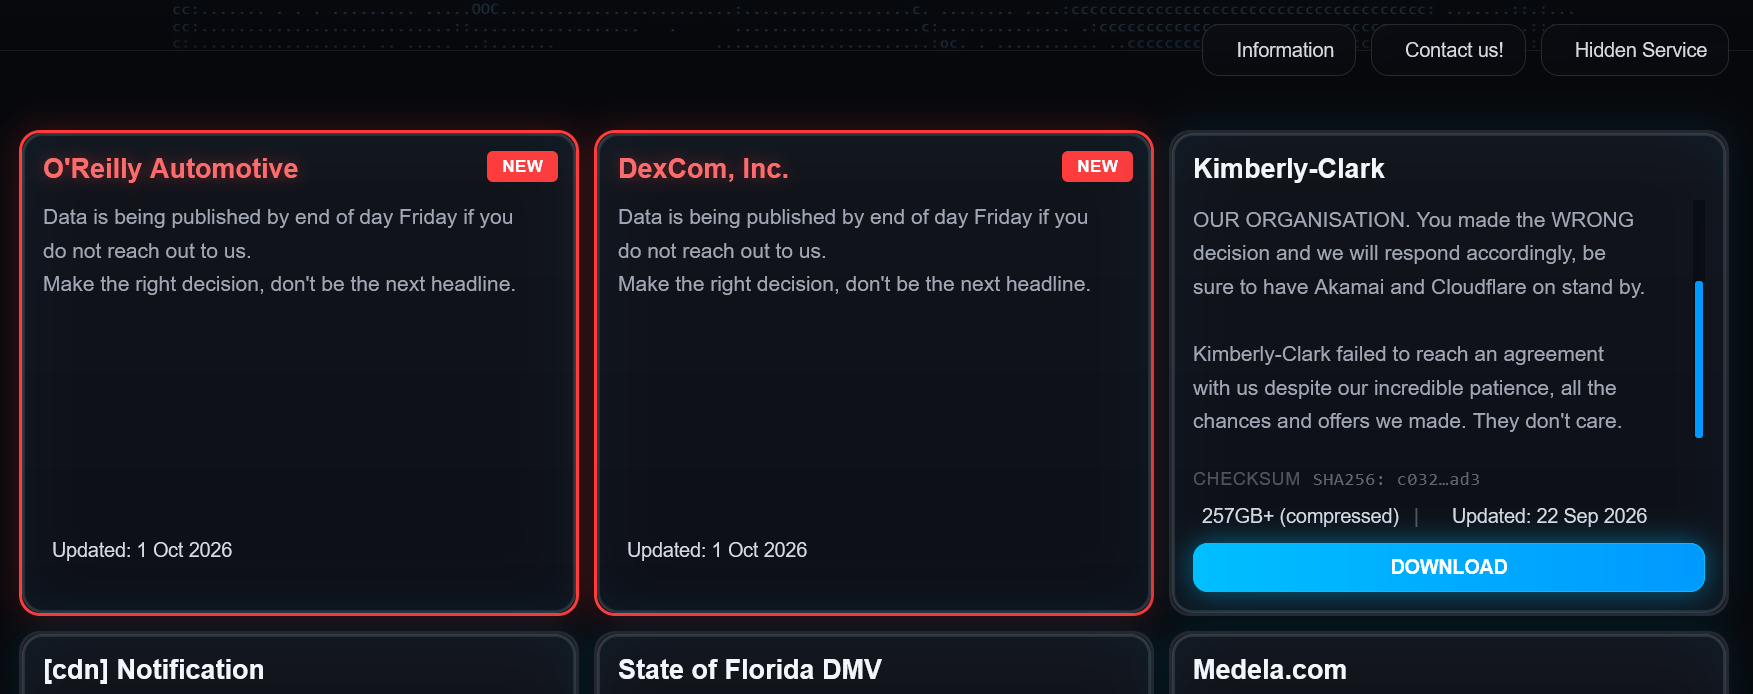
ShinyHunters’ leak website continued exhibiting exercise after Rey was reportedly detained on 29 September. Entries naming O’Reilly Automotive and DexCom have been posted on 1 October and deleted on 3 October.
The modifications recommend that different folks retained entry to the group’s infrastructure, though they don’t reveal who managed the listings or what number of people stay concerned.
The most recent reporting goes additional. Two sources advised Reuters that Khader is strolling investigators via his digital gadgets and communications to assist determine different members. One supply described his cooperation as necessary to persevering with arrest efforts.
For a gaggle whose membership has typically been troublesome to outline, entry to a suspected operator’s gadgets and communications might give investigators data that public aliases and leak websites can not. What Khader has supplied, whether or not he faces expenses, and whether or not Jordan intends to extradite him haven’t been disclosed.