Infostealers have grow to be a longtime enterprise, with builders who produce and preserve the product and paying prospects who run their very own campaigns with them. Amatera – which topped ESET’s infostealer detections in Latin America within the first half of 2026 however targets victims worldwide – reveals what this professionalization appears to be like like in follow.
Like many different infostealers, Amatera goes after a spread of knowledge spanning login credentials, session cookies, tokens, crypto pockets data, messaging information, information, and secrets and techniques from growth environments. The sheer breadth of the loot reveals why infostealers are a mainstay of cybercrime – a single compromise can result in account hijacking, monetary fraud and crypto theft, in addition to open the door into the group the place the sufferer works.
Right here’s extra about the place Amatera got here from, together with its enterprise mannequin, capabilities, and distribution.
What’s Amatera?
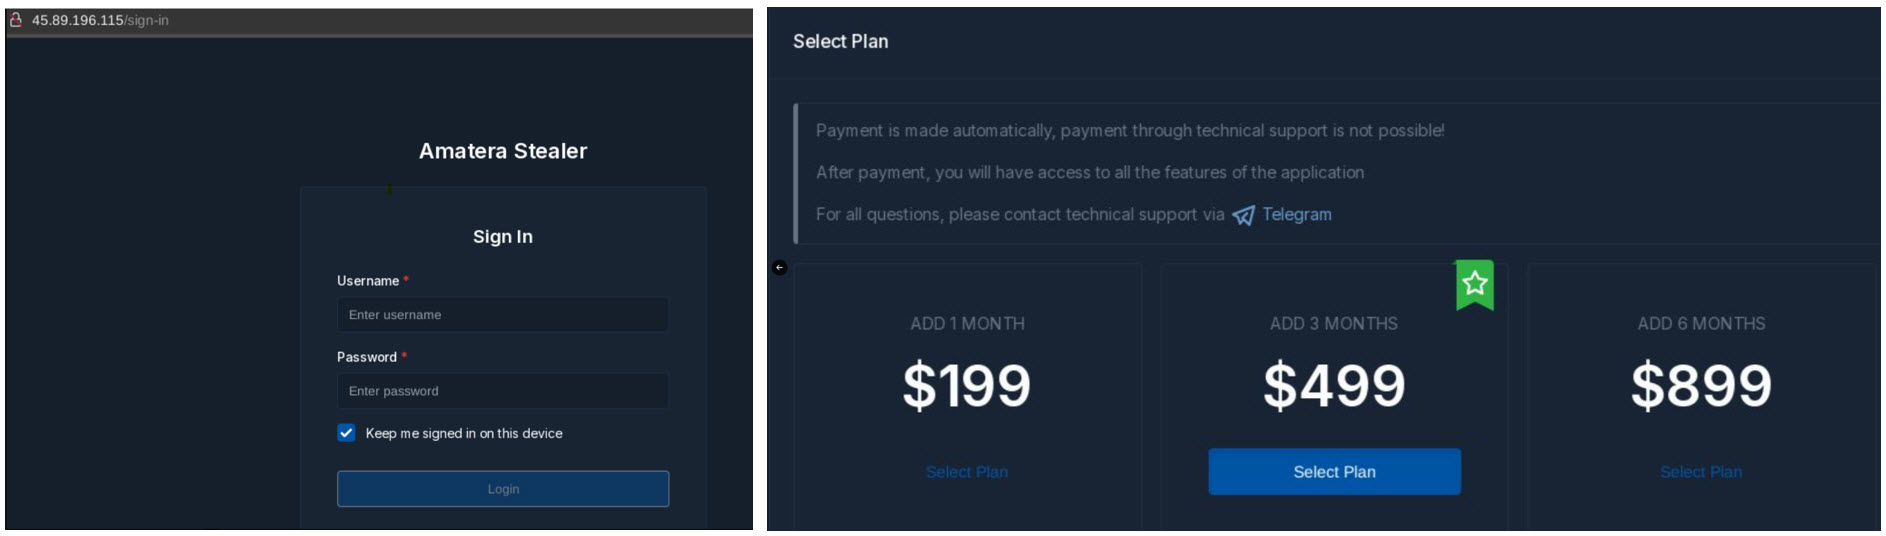
Detected by ESET merchandise as Win/PSW.Amatera, Amatera is a Home windows infostealer written in C++ that was first noticed in 2024. Because it’s marketed underneath the malware-as-a-service (MaaS) mannequin, its builders preserve the code, the management panel, and the assist infrastructure, whereas associates pay a subscription to make use of the malware of their campaigns.
Given the similarities of their respective code, Amatera could be very probably a rebrand of ACR Stealer. Certainly, the latter has a predecessor of its personal: a Sekoia investigation in Could 2024 described it as an up to date model of the GrMsk stealer, supplied as a service on underground boards.
Rebranding – or releasing an up to date model of a chunk of malware underneath a brand new title – is quite common throughout the MaaS ecosystem, significantly amongst ransomware operators. They often promote the supply code after they shut down their operations to keep away from being tracked, or they replace and rename it as a ‘enterprise technique’. In some circumstances, they leak it in order that different malicious actors can reuse it. At any price, by the top of 2024, Amatera Stealer was already on supply for $199 a month, with assist by way of Telegram..
Amatera’s capabilities
Amatera extracts credentials saved in internet browsers, together with cookies, shopping histories, type information, and session tokens. It might probably additionally seek for and seize delicate paperwork and information synced with OneDrive or SharePoint – Microsoft reported a surge in assaults on its enterprise prospects between late April and mid-June 2026. Individually, Straiker discovered that the malware additionally went after cryptocurrency pockets information by manipulating the clipboard.
The malware can also be underneath fixed growth, and it turns up as the ultimate payload in all kinds of assault chains. That selection can also be typical of MaaS: the builders promote the product, and every affiliate chooses their very own method to ship it.
Amatera has unfold by way of compromised web sites, search engine adverts, focused emails, pretend paperwork, SVG information, and ClickFix by way of pretend CAPTCHAs. Certainly, a number of latest analyses of Amatera campaigns worldwide present that one among its key supply vectors is ClickFix, a social engineering method that was first documented in 2024 and was rapidly picked up by adversaries to distribute a variety of malware households.
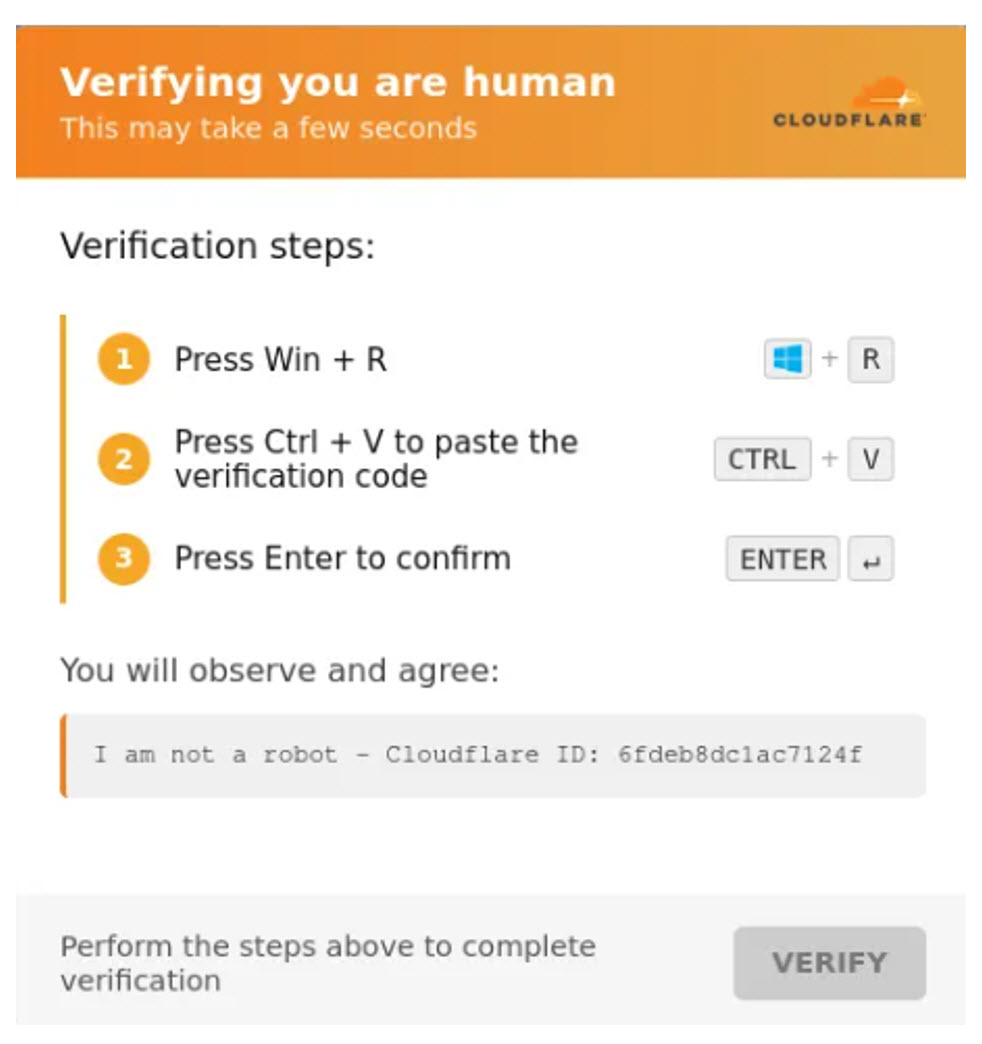
Typically, the sufferer sees a message that mimics a CAPTCHA verify or a browser error and warns them of supposed technical issues that may be fastened by copying a command and working it on their laptop. The sufferer’s personal keystrokes then set the compromise in movement. The method has moved past pretend CAPTCHAs, nonetheless, as adversaries saved the social engineering core of ClickFix with some tweaks:
· AI-fix: Attackers construct pages that impersonate professional AI companies, together with Anthropic’s Artifacts, OpenAI’s Canvas, and Microsoft Copilot Pages. The pages comprise pretend troubleshooting content material for non-existent issues.
· CrashFix: A pretend advert blocker triggers pretend browser crashes and warns of knowledge loss, pushing victims towards a malicious “fast repair.”
· ConsentFix: This variant tips the victims into handing over their OAuth authorization tokens that open their Microsoft accounts to attackers with none password being stolen.
ClickFix-based campaigns have additionally used professional however compromised WordPress websites, amongst different strategies. Attackers gained entry to those websites by means of weak or stolen administrative credentials or by exploiting vulnerabilities in WordPress themes and plugins.
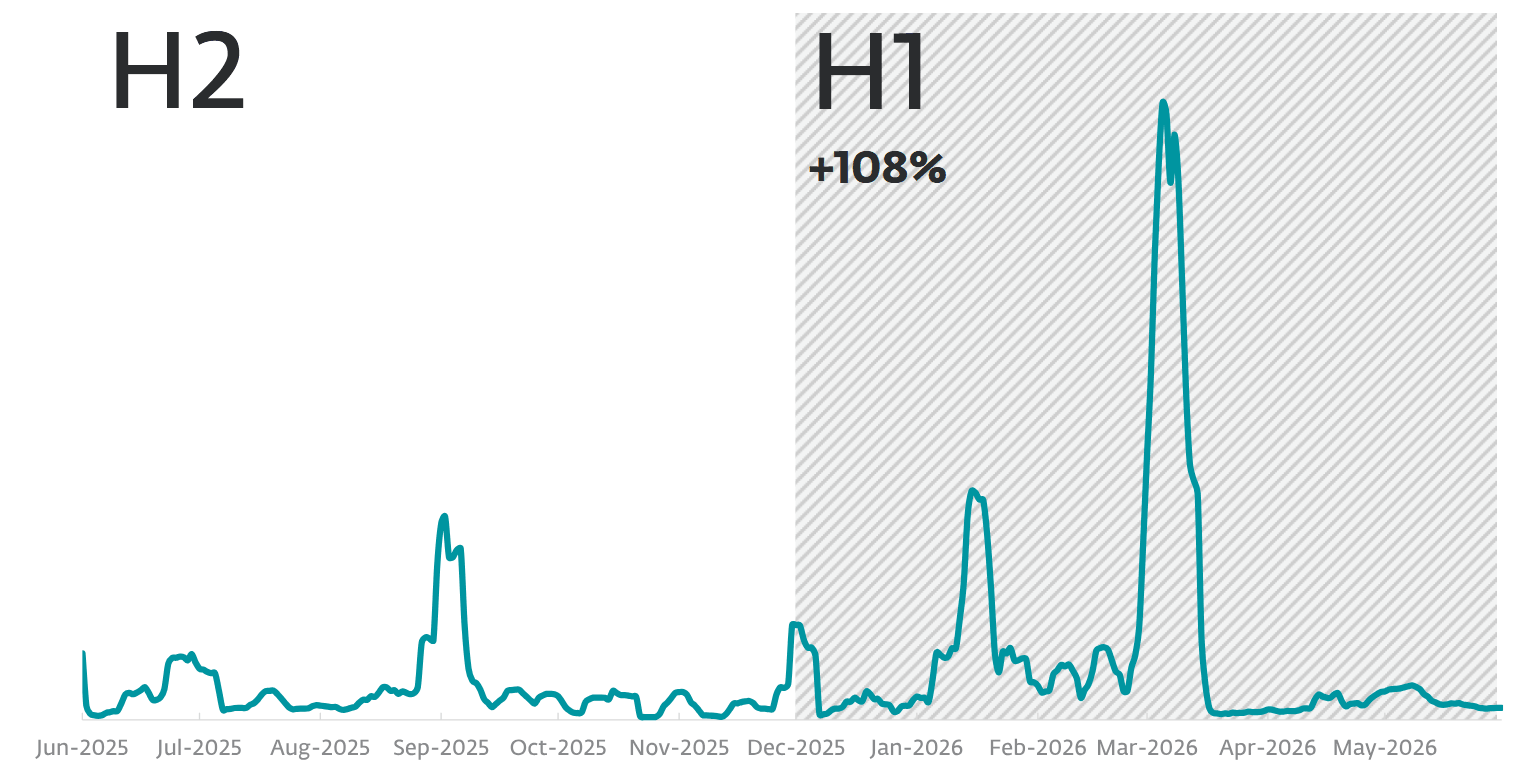
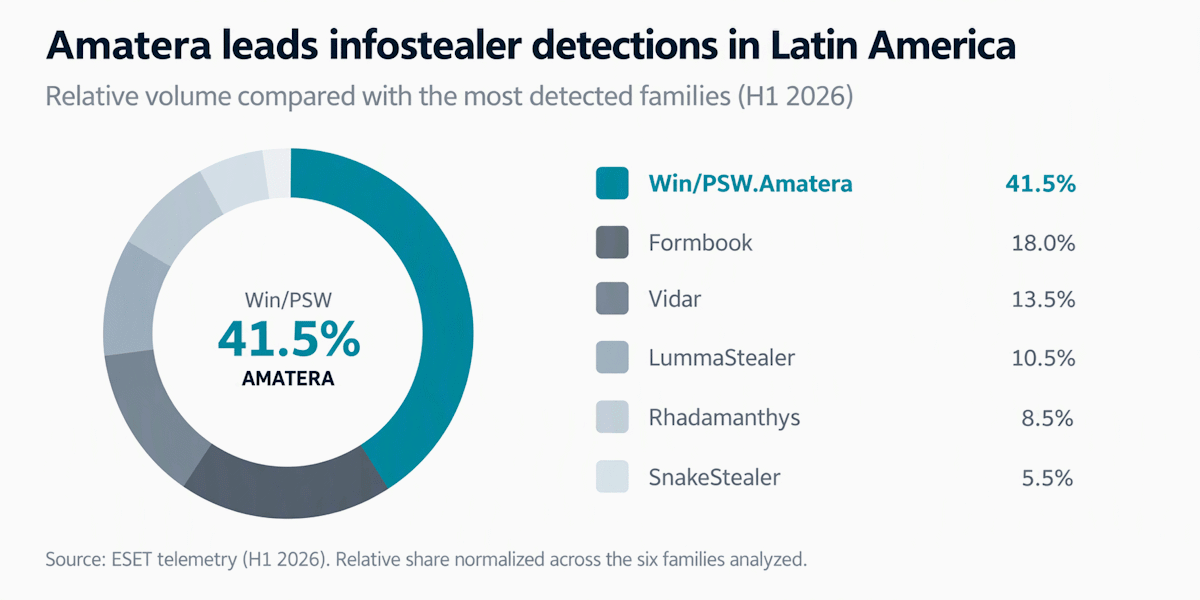
In Latin America, Amatera topped ESET’s infostealer detections within the first half of 2026, forward of Formbook, Vidar, Lumma Stealer, SnakeStealer, and Rhadamanthys. ClickFix’s latest development globally hasn’t been a straight line, nonetheless. ESET detections jumped by greater than 500% within the first half of 2025 in contrast with the earlier six months, making it the second commonest assault vector after phishing. Detections fell steeply within the second half of 2025, earlier than greater than doubling within the first half of 2026 as attackers tailored the method to new environments.
Amatera’s associates additionally purchase Google adverts. The Straiker analysis talked about above uncovered dozens of faux set up pages that have been promoted by means of paid adverts and search engine optimization poisoning and impersonated AI and developer instruments, equivalent to Claude Code, NotebookLM, JetBrains, Comet, and Snowflake, and particularly focused builders who use AI instruments. Like AI-fix, these pages piggyback off the credibility of AI manufacturers and share the execution chain with ClickFix.
Dangers and penalties of an Amatera compromise
Based mostly on its capabilities, these are a number of the potential penalties of falling sufferer to Amatera:
- Compromise of non-public or company accounts by means of stolen passwords, cookies, and tokens
- Unauthorized entry to e mail and cloud storage
- Theft of crypto belongings when wallets or restoration phrases are uncovered
- Infrastructure compromise by means of SSH keys, FTP credentials, or growth secrets and techniques
- Set up of extra malware
- Use of a compromised account for fraud, inner phishing campaigns, or additional intrusions
The danger spills over to employers when the sufferer mixes private and work profiles in the identical internet browser. A house laptop might maintain company e mail periods, cloud consoles, code repositories, or HR methods. The stolen data ultimately turns into a gateway that one other actor can purchase or exploit days later.
How one can stop and reply to an Amatera compromise
Listed below are just a few ideas for staying out of hurt’s manner, particularly in company environments:
- Keep in mind that no professional CAPTCHA, error message, or set up information will ask you to repeat instructions from an online web page into the Run dialog, PowerShell, or Terminal. A search engine advert is not any assure {that a} web site is official. That applies equally to pages that seem like they belong to a well known AI service.
- Implement software management guidelines and scale back the assault floor by limiting using system interpreters and binaries exterior their regular context.
- Monitor PowerShell, Rundll32, WebDAV, uncommon scheduled duties, and the clearing of PowerShell historical past.
- Use phishing-resistant authentication and hold browser periods as quick as enterprise wants permit.
- Separate private and work profiles, and keep away from storing secrets and techniques within the browser when a managed various is offered.
- Filter newly created websites, cloned set up pages, and downloads initiated from adverts when the context doesn’t justify them.
If a compromise is confirmed, isolating the system is just step one. From a trusted system, revoke energetic periods, reset passwords, and rotate API keys, tokens, SSH credentials, and another secrets and techniques current on the system. Additionally, evaluation entry to e mail, cloud companies, repositories, and monetary purposes. The response should observe follow-on exercise, relatively than cease on the preliminary host – documented campaigns executed extra payloads, created scheduled duties, coated their tracks, and used professional system instruments.
Conclusion
Amatera reveals how the infostealer market works in the present day. A developer maintains the product, and different actors distribute it by way of compromised web sites, adverts, pretend AI instruments, emails, or ClickFix directions. The menace can outlive the malicious file itself, nonetheless, as passwords, cookies, session tokens, and confidential paperwork stay beneficial even after the system has been cleaned. Stolen information can gas each fast fraud or later intrusions, and the rise in detections in 2026 reveals attackers adopting and adapting malicious toolsets at a speedy clip.