A Railway engineer admitted testing AI brokers on Primcloud, whose founder says they sought buyer secrets and techniques and scanned its community.
An engineer at cloud platform Railway has acknowledged operating AI brokers towards competing cloud platform Primcloud after its founder reported makes an attempt to acquire buyer secrets and techniques and scan inner methods. Primcloud says its controls blocked the makes an attempt and no buyer knowledge was accessed.
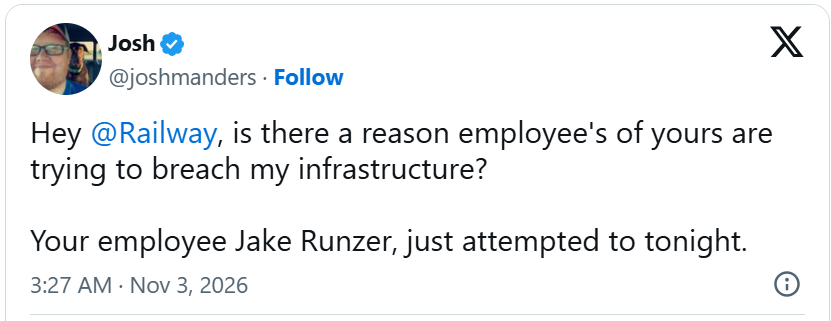
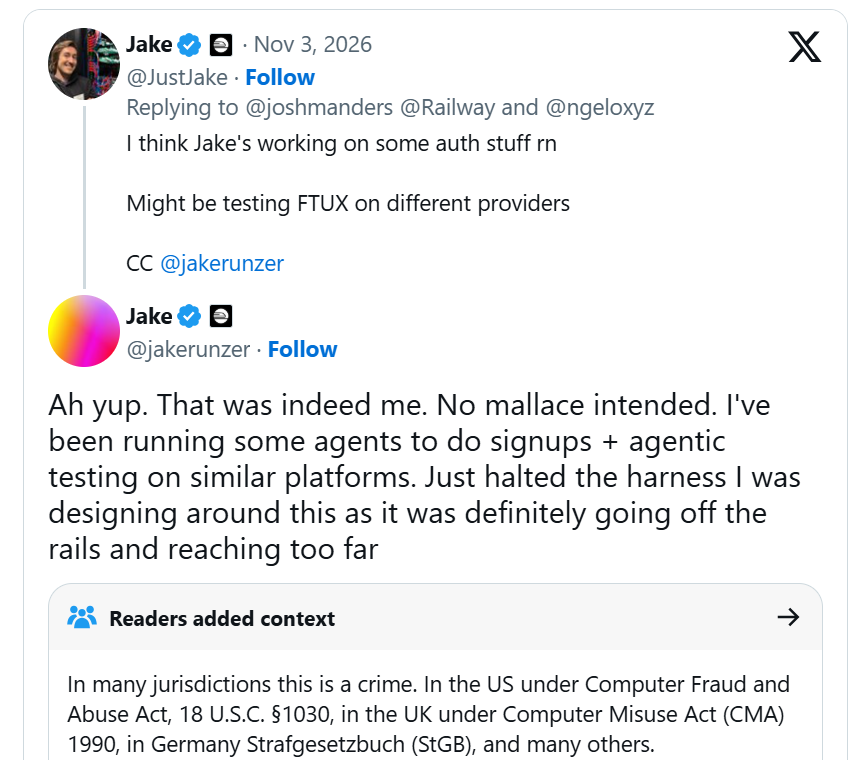
Josh Manders, Primcloud’s founder, publicly challenged Railway on November 3, figuring out senior product engineer Jake Runzer because the individual behind the exercise. Runzer accepted duty for operating the brokers, describing their goal as signups and automatic testing on comparable platforms.
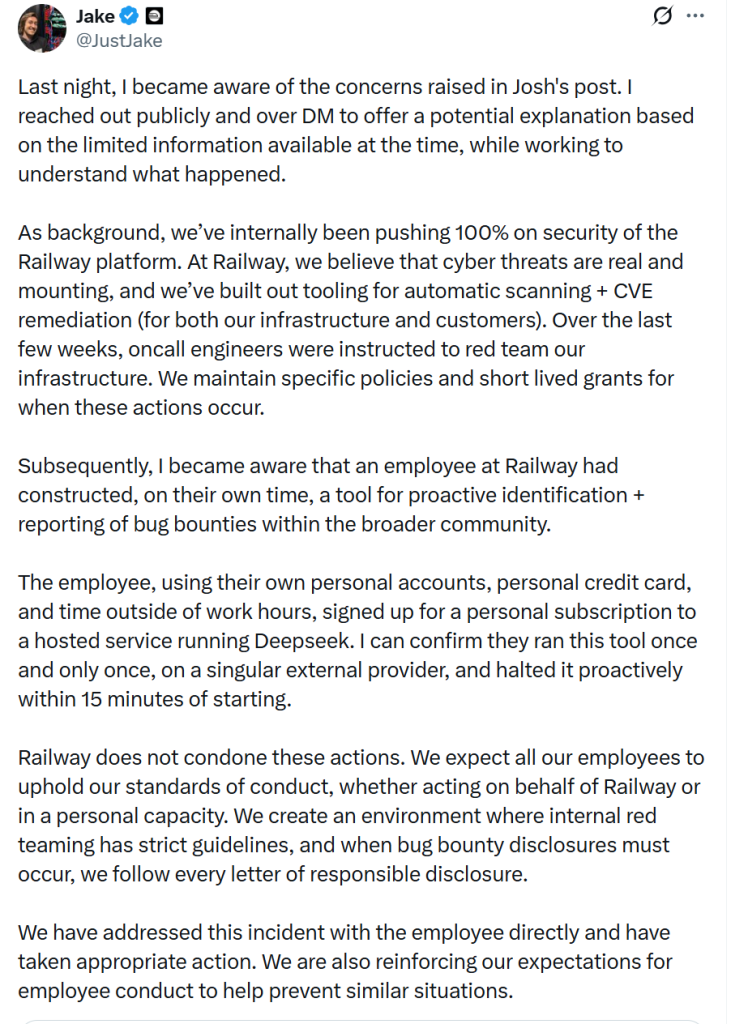
Railway co-founder and CEO Jake Cooper initially apologised. In a later assertion, he mentioned the worker constructed and operated the software personally outdoors work hours and that Railway took inner motion.
His clarification provides an essential distinction to the dispute, which considerations an worker’s acknowledged exercise, not proof of a company-directed operation towards a competitor.
Primcloud Describes Makes an attempt to Attain Different Clients’ Secrets and techniques
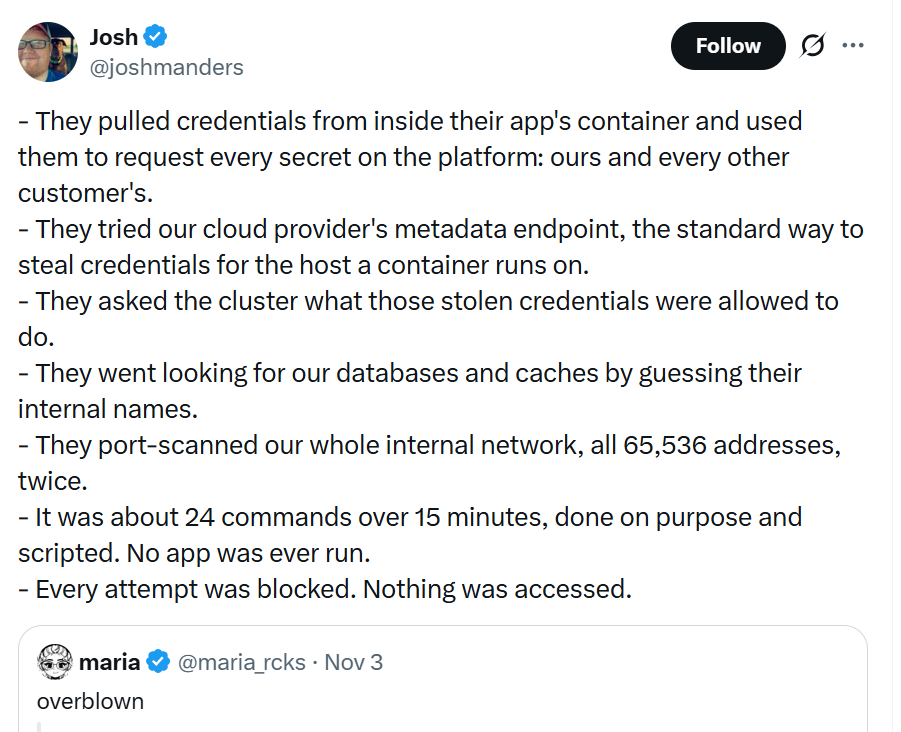
In line with Manders’ account, the exercise went significantly additional than attempting the platform’s signup course of. He mentioned credentials accessible contained in the account’s utility container had been used to request platform secrets and techniques, together with these belonging to different clients.
The brokers additionally tried to succeed in the cloud supplier’s metadata endpoint, checked what the container credentials may entry and looked for databases and caches by guessing inner names, Manders mentioned. Cloud metadata providers can expose non permanent credentials when accessible with out ample restrictions.
Manders described roughly 24 instructions over quarter-hour, together with two scans overlaying 65,536 inner community addresses. That’s his reported tackle rely, not a rely of confirmed dwell hosts or uncovered providers. He mentioned no utility was run and the makes an attempt to succeed in protected sources had been blocked.
These technical particulars stay Primcloud’s account of the exercise. Runzer acknowledged working the brokers, however that acknowledgement doesn’t independently confirm each command, goal or end result Manders described.
Railway Says the Software Was a Private Mission
In his reply to Manders, Runzer mentioned he had been operating brokers for signups and testing on comparable platforms. He denied malicious intent and mentioned he had stopped the system after recognising that it was reaching too far.
Cooper’s later assertion described a private software meant to determine and report bugs via bounty programmes. He mentioned the worker used private accounts, a private bank card and a subscription to a hosted service operating DeepSeek.
In line with Cooper, the software ran as soon as towards one exterior supplier and was stopped inside quarter-hour. He mentioned Railway didn’t condone the conduct and had addressed it with the worker, with out specifying what motion had been taken. He additionally distinguished the exercise from Railway’s authorised inner safety testing.
The outline of the software as a bug-bounty mission doesn’t set up that Primcloud authorised the testing. Nor do the general public statements set up why the brokers chosen every motion or how intently an individual supervised their execution.
Duty Stays With the Operator
For the corporate receiving the requests, the quick concern is what the software program does inside its surroundings. Ram Varadarajan, CEO of Acalvio, mentioned in feedback shared with Hackread.com that distinguishing an agent’s intentions is an unreliable foundation for defense.
“Whether or not you name it a rogue agent or agentic testing, the defender sees the identical habits: one thing contained in the surroundings is harvesting credentials and mapping the community. Sadly, you may’t reliably classify AI intent, particularly with autonomous brokers.”
Varadarajan mentioned decoy credentials and faux inner property might help determine exercise that authentic workflows mustn’t set off, no matter whether or not an individual or an agent initiates it.
Diana Kelley, Chief Data Safety Officer at Noma Safety, mentioned organisations stay liable for addressing actions taken by brokers working underneath their authority. That features investigating incidents, notifying affected organisations and placing controls in place to stop a recurrence.
“An agent can act with no individual directing each step. It doesn’t take away the duty of the folks and organizations that deploy it.”
Railway Disclosed Its Personal Breach in October
The dispute follows a separate safety incident at Railway. In its October 21 disclosure, the corporate mentioned an unauthorised social gathering could have accessed encrypted buyer surroundings variables and obtained some decrypted contents. These variables can include API keys, database passwords and different credentials.
Railway’s preliminary report, revealed the next day, described unauthorised entry to inner methods and confirmed that some encrypted surroundings variables had been decrypted. It suggested clients to rotate delicate credentials saved earlier than October 21.
The report put the higher estimate of workspaces with some surroundings variables uncovered at 1.85%, roughly 100,000 workspaces. Railway mentioned precautionary requests to revoke credentials affected a bigger inhabitants, so receiving a revocation discover didn’t itself set up {that a} buyer’s secrets and techniques had been compromised.