An summary of the actions of chosen APT teams investigated and analyzed by ESET Analysis in Q2 2026 and Q3 2026

28 Oct 2026
•
,
6 min. learn
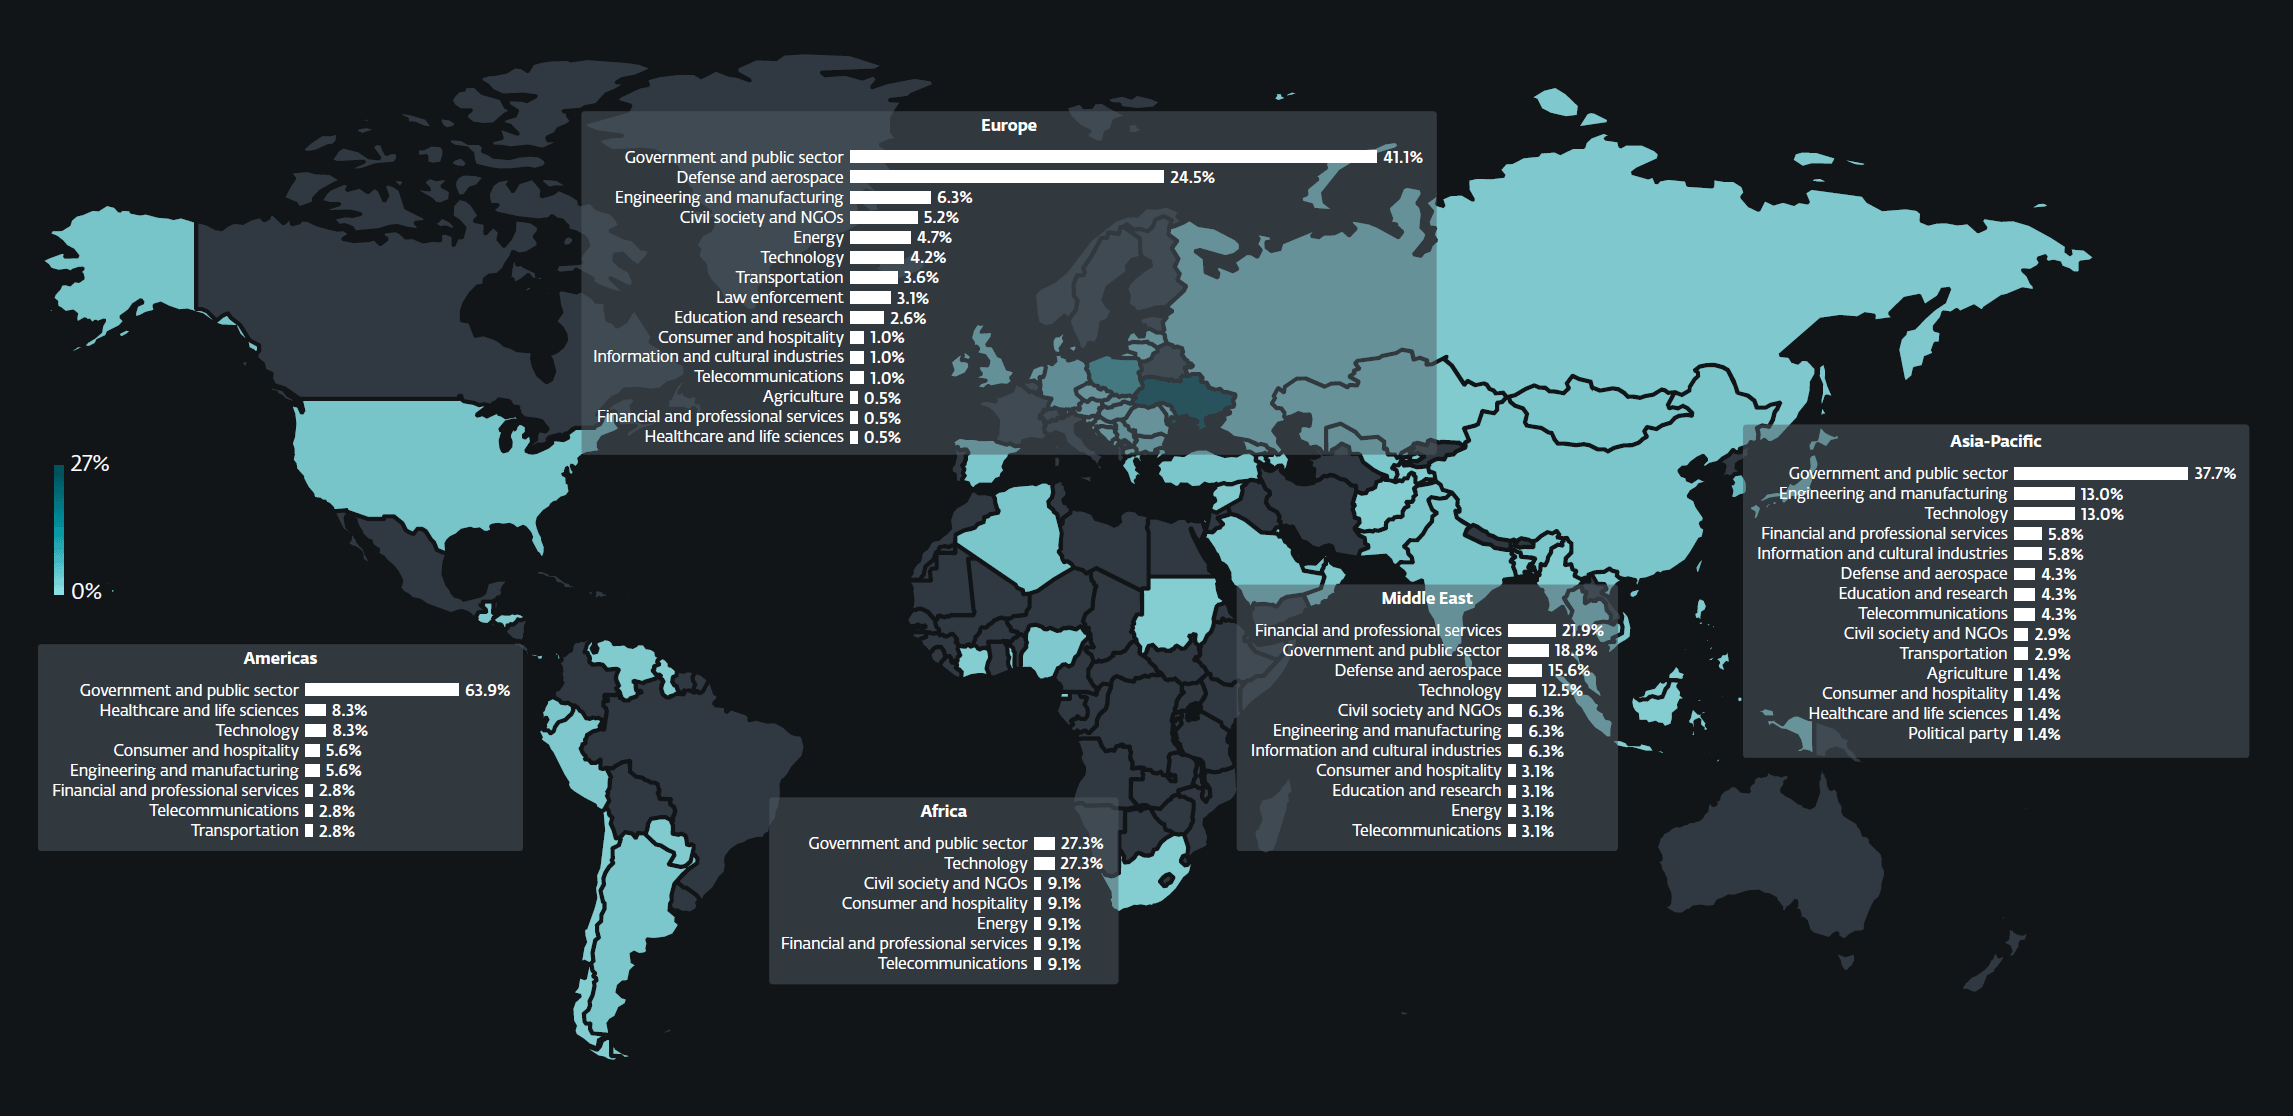
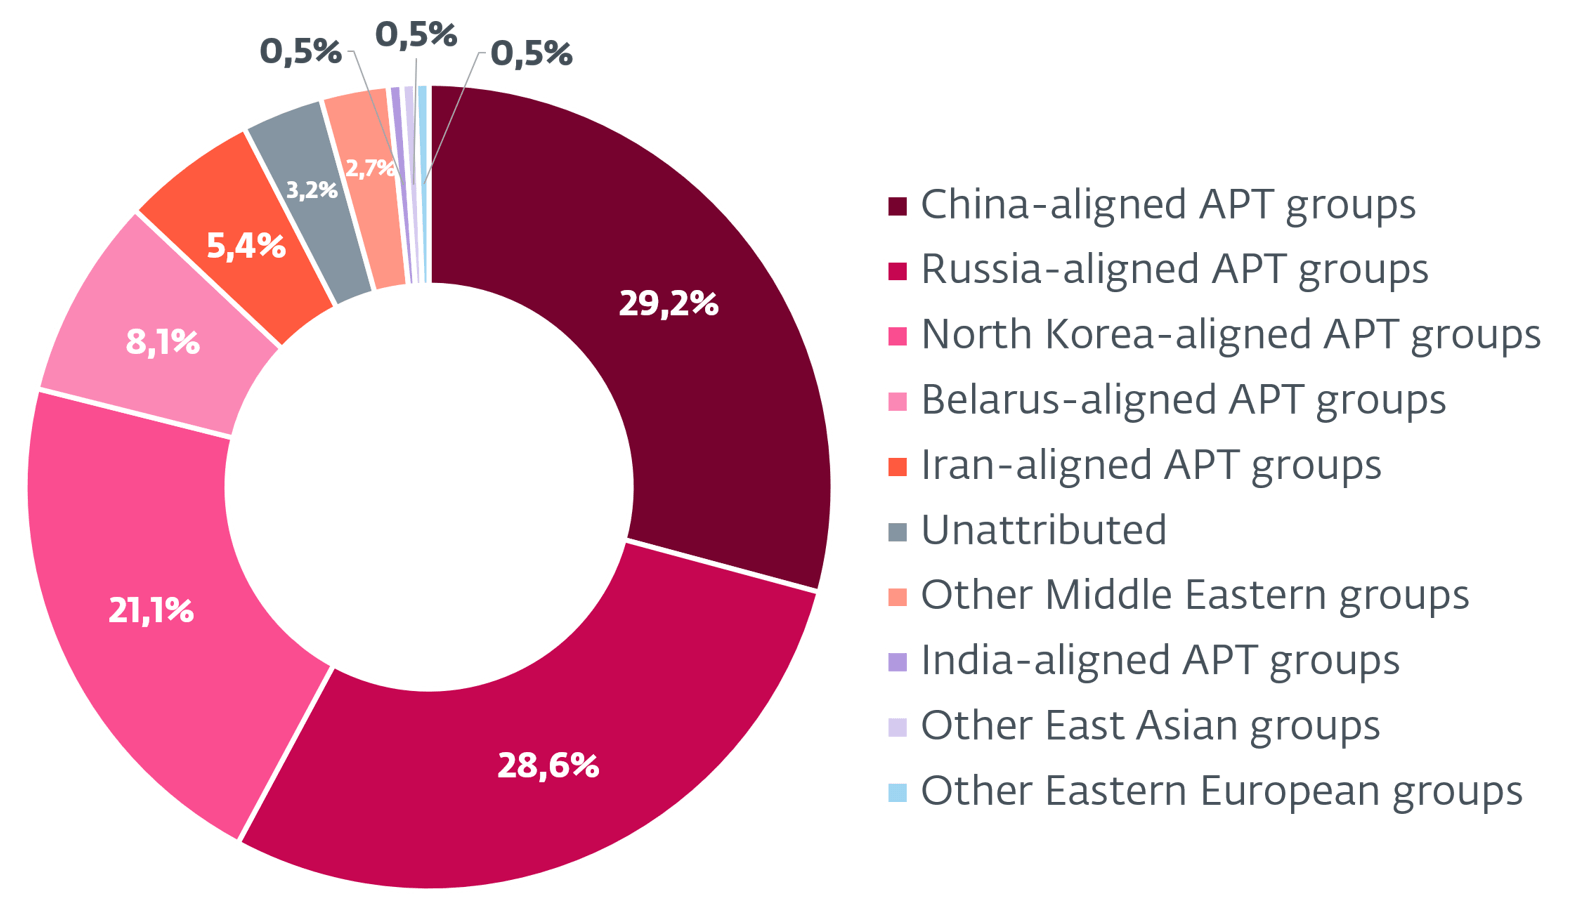
ESET APT Exercise Report Q2 2026–Q3 2026 summarizes notable actions of chosen superior persistent menace (APT) teams documented by ESET researchers between April and September 2026. The operations introduced right here replicate the broader menace panorama noticed throughout this era and spotlight a few of its key developments and developments. They characterize solely a subset of the cybersecurity intelligence made out there to clients of ESET Menace Intelligence APT Reviews.
Through the monitored interval, China-aligned teams performed intelligence-collection operations primarily in opposition to governmental targets. FamousSparrow stored up its monitoring in South America, simply as within the earlier reporting interval. In Southeast Asia and Oceania, China-aligned menace actors ran campaigns that seem to help Chinese language regulation enforcement efforts in opposition to organized crime within the area. One menace actor focused inns in Palau, which appears to be more and more used as a base for fraud-related organized crime. SlippyNunchucks deployed its DarkVigil toolset in Sri Lanka in opposition to Chinese language-speaking people related to fraud schemes, seemingly within the context of broader regional regulation enforcement efforts in opposition to monetary crime. As rip-off compounds have grow to be a difficulty for international locations neighboring China, with direct damaging results on China itself, it’s seemingly that China-aligned APT teams have supported regulation enforcement efforts on this space. One other, broader cluster of exercise focused Taiwanese organizations working within the semiconductor trade. This concentrate on Taiwan’s semiconductor sector is in line with long-running Chinese language industrial espionage priorities, and the strategic significance of semiconductor provide chains to each financial competitors and nationwide safety.
Center East-aligned exercise elevated in contrast with the earlier reporting interval, pushed primarily by the return of a number of established Iran-aligned teams. Within the earlier interval, exercise from these teams had declined, probably as a result of web restrictions imposed by the Iranian regime hindered their very own means to function successfully. FilthyFeline, a subgroup of OilRig, and MuddyWater resumed operations after a quieter interval, with most exercise directed at entities in Israel throughout a number of sectors; a smaller variety of US corporations have been additionally affected. FilthyFeline additionally seems to have taken over exercise in opposition to a mobile knowledge service supplier in Uzbekistan that had beforehand been compromised by BladedFeline, one other OilRig subgroup. In parallel, we analyzed new or up to date malware, suggesting renewed growth exercise inside elements of the Iran-aligned ecosystem. We additionally found exercise by Arid Viper, a Hamas-affiliated menace actor, in opposition to what seems to be the Palestinian Authority’s Ministry of Overseas Affairs and Expatriates or an affiliated governmental entity. Given the continued US-led peace course of, in addition to the long-standing rivalry between Hamas and the Palestinian Authority, this exercise was doubtlessly supposed to gather intelligence on the Palestinian Authority’s diplomatic place and inner pondering concerning negotiations to scale back hostilities within the area.
North Korea-aligned menace actors didn’t deviate considerably from the sorts of targets seen in earlier reporting intervals. These embrace primarily expertise and cryptocurrency corporations, software program builders, and different opportunistic targets. Alongside South Korea, Ukraine has grow to be more and more outstanding amongst North Korea-aligned targets. That is seemingly associated to rising ties between Russia and North Korea, and North Korea’s growing involvement in Russia’s warfare in opposition to Ukraine, not solely by oblique army help (munitions, and many others.) but in addition by the deployment of North Korean troopers. Alongside these broader developments, Lazarus resumed concentrating on of the drone sector, usually utilizing recruitment-themed social engineering to realize preliminary entry. The seemingly motivation is the more and more vital function that drone methods are taking part in within the warfare in Ukraine, the place new ways and capabilities are being examined. Entry to such data and manufacturing processes might present North Korea with helpful know-how for growing its personal drone-production capabilities. We additionally detected ScarCruft concentrating on an African nation, which was most likely supposed both to take care of oversight of a North Korean employee scheme working within the nation or to observe Russian actions there. Individually, DeceptiveDevelopment moved from faux job-interview lures to broader software program supply-chain compromises, harvesting developer credentials and utilizing that entry to inject malicious code into private and non-private supply code repositories.
Russia-aligned exercise continued to help its warfare aims, concentrating on governments, the protection sector, and army entities in Europe, with a considerably greater variety of targets in Ukraine. Trying extra carefully at these actions, similarities between Russia-aligned and Belarus-aligned campaigns stand out, additional supporting our speculation that menace actors aligned with the 2 international locations have gotten operationally nearer. Gamaredon’s operations, that are usually quite a few, noticed a major decline. We suspect that this might be associated to Ukrainian assaults on Crimea, the place the group is suspected to function, a broader restructuring of its operations, or different components that we proceed to evaluate. Regardless of this decline in exercise, Gamaredon up to date its PteroBox file stealer and began utilizing new instruments akin to PteroPSDoor and Turla’s VBScript Rezzuar. PhantomCaptcha tried to deploy spyware and adware, which we named PrincessSpy, on Android gadgets whereas impersonating Ukrainian entities. We additionally recognized an intensive marketing campaign in Ukraine exploiting MDaemon mail servers, throughout which the attackers deployed two backdoor malware households, HELLAGE and HELLTAG.
North Korea’s increasing army cooperation with Russia has prompted expectations that North Korea-aligned cyberactivity may be beginning to align extra carefully with Russian aims in Ukraine. Whereas a few of their concentrating on pursuits overlap, notably across the drone sector, our telemetry extra clearly factors to Belarus-aligned teams appearing as cyberproxies or power multipliers for Russia. We noticed elevated and extra assertive exercise from Belarus-aligned menace actors, with their operations more and more reflecting Russia’s intelligence priorities in Ukraine in some areas. Most notably, we recognized the primary damaging cyberattack by a Belarus-aligned menace actor that we’ve got documented within the European theater, marking a major growth on this menace nexus. In accordance with our telemetry, FrostyNeighbor attacked a producing firm in Ukraine that performs an vital function within the nation’s transportation sector. This marks a notable escalation, as menace actors with a well-established historical past of damaging cyberoperations in Ukraine have, till now, been Russia-aligned.
Lastly, we recognized a number of instances of APT teams utilizing AI and huge language fashions (LLMs) at varied levels of their operations. Menace actors used AI primarily to speed up duties that will in any other case require painstaking effort, together with malware growth and the creation of decoy web sites. In some instances, this resembled vibe coding: speedy, prompt-driven drafting of code, with human operators adapting and integrating the outcomes into their toolchains. We additionally found phishing lures containing pictures that have been clearly AI-generated. In a single notable case, Russia-aligned UAC-0099 inserted a decoy request for directions on constructing a nuclear weapon right into a script remark, apparently trying to set off the protection guardrails of LLM-based safety evaluation and forestall the inspection of the malicious code that adopted.
Regardless of these developments, we’ve got not seen AI considerably reshaping the APT panorama over the previous six months. Whereas we can not decide whether or not some operations might contain a better diploma of AI-driven automation, our telemetry continues to indicate hands-on-keyboard exercise and operations that aren’t absolutely automated. General, our observations counsel that APT teams are at present utilizing AI very similar to mainstream software program builders: to speed up software program growth, automate beforehand handbook duties, and help with the evaluation of enormous volumes of knowledge, relatively than to conduct absolutely autonomous malicious operations.
ESET merchandise shield our clients’ methods from the malicious actions described on this report. Intelligence shared right here is primarily based on proprietary ESET telemetry knowledge and has been verified by ESET researchers.
ESET APT Exercise Reviews include solely a fraction of the cybersecurity intelligence knowledge supplied in ESET Menace Intelligence APT Reviews. For extra data, go to the ESET Menace Intelligence web site.