The FBI is warning a couple of new framework, ARTEX, which automates a number of phases of a cyberattack, from discovering targets to stealing information.
In a November 13 Flash Advisory, the Federal Bureau of Investigation (FBI) stated cybercriminals had been utilizing the open-source framework since not less than August 2026 to focus on organizations worldwide. The focused sectors embrace monetary providers, authorities, expertise, protection, healthcare, semiconductor, power, manufacturing, telecommunications and authorized providers.
One confirmed incident concerned a supply-chain compromise of ConnectWise Cloud Backup that allowed attackers to entry greater than 2,250 downstream tenants.
Written in Go, ARTEX connects to exterior giant language fashions (LLMs) like DeepSeek, Claude and GPT. What makes it completely different is its use of specialised AI brokers that work on separate duties after an operator units an goal. These brokers can establish targets, test programs for weaknesses, exploit them and exfiltrate information, with little human involvement.
The FBI says (PDF) some assaults have moved from preliminary focusing on to privileged entry in lower than three hours and that DeepSeek Flash fashions are significantly widespread amongst attackers due to their comparatively low price and lack of observable security guardrails for penetration testing.
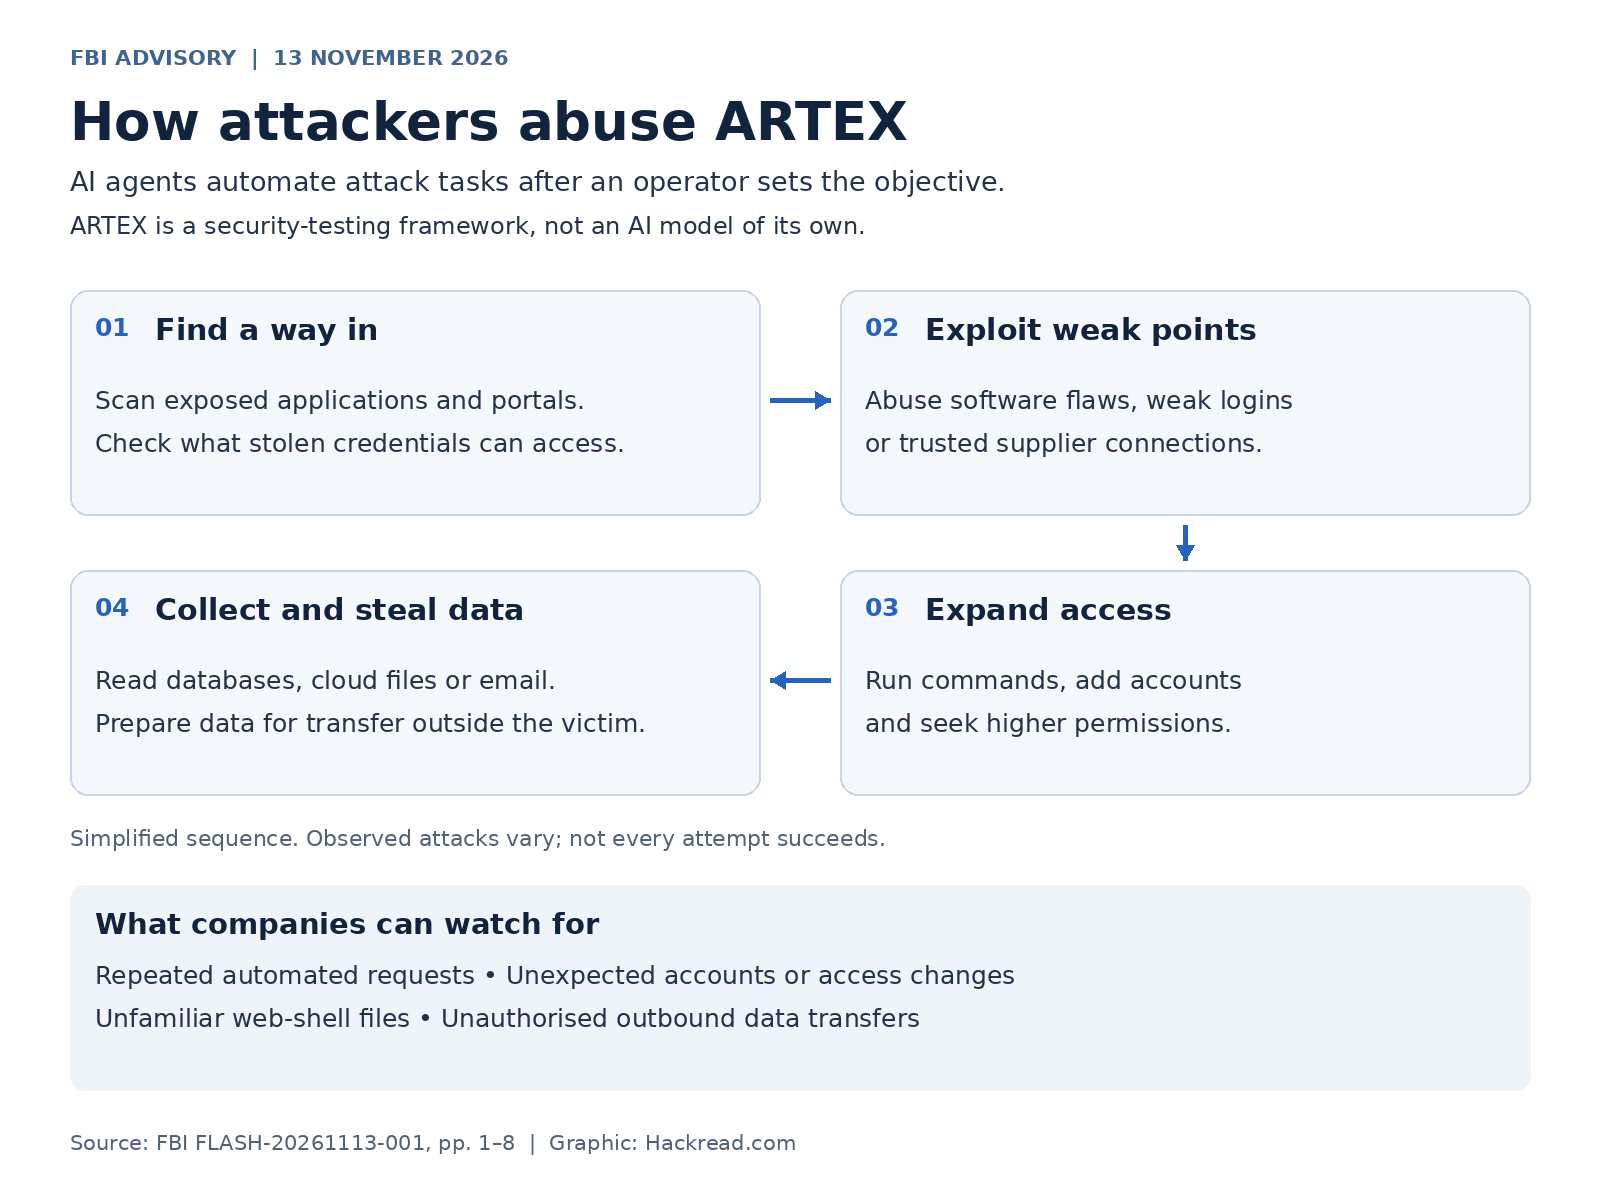
The issue goes past quicker assaults
Some ARTEX-assisted intrusions have reached privileged entry in lower than three hours. That leaves safety groups little time to research an intrusion earlier than attackers transfer additional right into a community. The ConnectWise incident exhibits how this will have an effect on different organizations.
Microsoft’s investigation into Artex linked the exercise to Storm-0940, a China-aligned menace group. After compromising ConnectWise purposes, the attackers used the entry to focus on buyer environments. Microsoft additionally recorded greater than 151,000 failed sign-in makes an attempt throughout a associated marketing campaign, with exercise reaching 2,900 makes an attempt per minute.
The FBI additionally highlighted assaults towards South Korean monetary establishments wherein private data of round 67,000 individuals was stolen. Impacted banks included Shinhan, KB Kookmin, Hana, BNK Busan Banks, Hyundai Capital, Yegaram Financial savings Financial institution, and Welcome Financial savings Financial institution amongst others.
These findings spotlight the gradual change in the way in which attackers are utilizing AI. Hackread.com beforehand reported on a PaperCut marketing campaign wherein a whole lot of AI brokers helped attackers develop, troubleshoot and scale the exploitation of two zero-day vulnerabilities. ARTEX brings a number of assault phases collectively in a single framework. This additional reduces the work wanted to maneuver between them.
Google’s menace intelligence workforce has additionally reported malicious use of different agentic frameworks, together with CAIRN and PentAGI. Its findings recommend that these operations could be noisy and comparatively unsophisticated however nonetheless profitable due to their pace and scale.
Taking down the unique instrument didn’t finish its use
ARTEX’s developer, Autumn-27, eliminated the unique GitHub repository on October 8, 2026, following stories of abuse. However copies, group forks and a business model known as ARTEX PRO stay out there with greater than 1,600 publicly uncovered ARTEX consoles recognized by early November.
The FBI is searching for authentication information, API exercise, cloud logs and different proof of ARTEX-related assaults.
The FBI’s findings have additionally raised considerations about how organizations handle uncovered programs, credentials and entry between suppliers. Morey J. Haber, Chief Safety Advisor at BeyondTrust, shared with Hackread.com that ARTEX modifications the time and experience wanted to show found weaknesses into working assaults.
“The reality, nonetheless, will not be a couple of new exploit or zero-day vulnerability developed by AI. It’s the collapse of the time and the experience barrier between what’s found and when it’s weaponized. Risk actors have lengthy identified that the weakest hyperlink will not be at all times on a flagship utility. A profitable breach can happen in a accomplice portal, a legacy service, a backend cell utility, or a forgotten third-party integration. Till now, discovering and chaining these dependencies took effort, expertise, and time. ARTEX industrializes these ideas.”
Haber additionally warned that organizations ought to pay nearer consideration to identities and credentials utilized by purposes and automatic providers, not simply worker accounts.
“ARTEX will not be breaking in a lot as logging in with keys it finds mendacity round, together with machine identities and repair accounts that no one is monitoring or which were forgotten about. And because it maps belief between organizations, your threat is just as sturdy as your weakest provider. Put merely, the blast radius extends nicely past your personal perimeter.”