Cyberattacks affecting greater than 700 supermarkets in France in October 2026 concerned manipulated refrigeration temperatures and defrost settings, inflicting meals losses. CERT-FR confirmed compromises involving Danfoss AK-SM and AK-SC programs, in addition to Copeland and Dixell XWEB tools. As Hackread.com beforehand reported, the attackers’ identities and exact methodology of gaining entry stay unconfirmed.
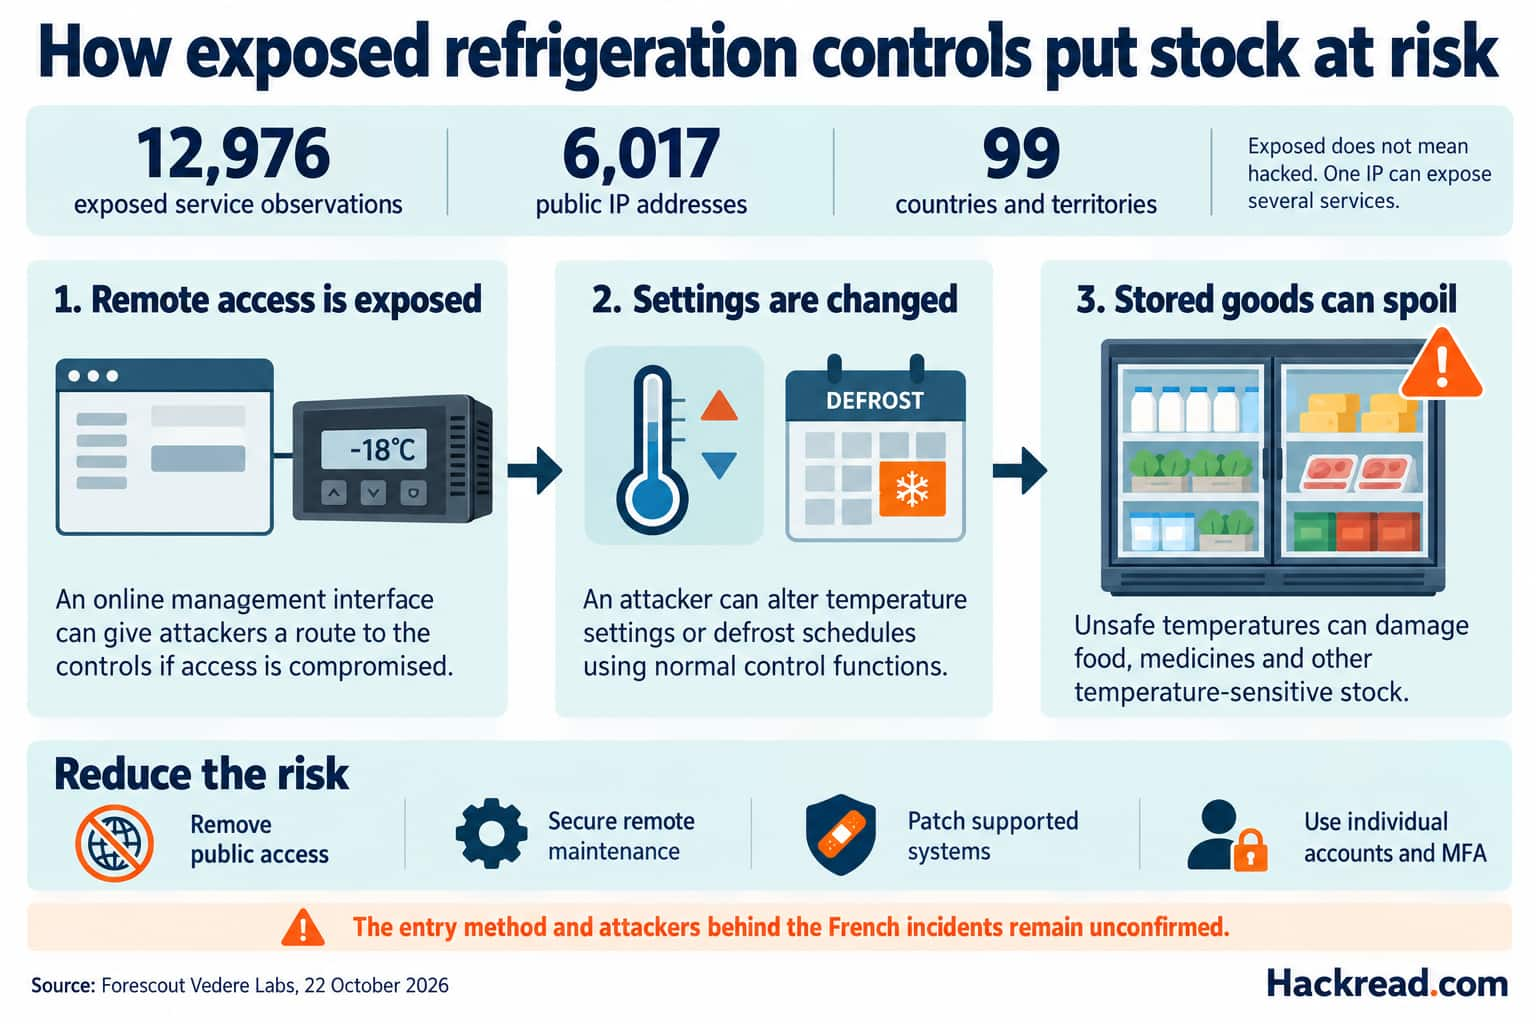
In opposition to this backdrop, cybersecurity researchers at Forescout’s Vedere Labs recognized 12,976 internet-exposed refrigeration service observations throughout 6,017 public IP addresses in 99 international locations and territories.
The researchers used Shodan, a search engine for Web of Issues (IoT) gadgets, to establish uncovered providers throughout 10 product teams. The figures signify service observations moderately than particular person refrigeration programs, as one IP tackle can expose a number of interfaces or signify a number of downstream programs.
The report warns that uncovered administration interfaces and software program vulnerabilities can let cybercriminals manipulate refrigeration programs. This means a critical danger for industries that depend upon temperature-controlled storage similar to supermarkets, hospitals, agricultural amenities and pharmaceutical provide chains.
Grocery store Assaults Spotlight the Dangers
Forescout additionally tracked greater than 20 claimed assaults in opposition to refrigeration programs since January 2026, with pro-Russian hacktivist teams Z-Pentest Alliance and NoName057(16) among the many most lively. Targets included wineries, fruit storage amenities, supermarkets and food-processing websites throughout Europe.
On April 26 alone, Z-Pentest claimed 10 assaults. The risk predates this 12 months’s incidents. In line with a Danfoss technical bulletin printed in October 2025, earlier assaults in 2022 affected 16 Russian supermarkets and 40 Israeli shops.
Hundreds of Refrigeration Companies Uncovered On-line
Forescout recognized the next internet-exposed providers, grouped by product household. The corporate additionally discovered that 80% of noticed Danfoss StoreView providers had been operating older firmware doubtlessly affected by recognized vulnerabilities.
The next uncovered providers had been recognized:
| Product household | Uncovered providers |
| Copeland/Dixell XWEB | 7,075 |
| Danfoss StoreView | 4,697 |
| Copeland Website Supervisor | 551 |
| Carel pCOWeb | 513 |
| Different programs | 140 |
Forescout additionally discovered that 80% of noticed Danfoss StoreView providers had been operating older firmware doubtlessly affected by recognized vulnerabilities.
Danfoss’ August 2025 advisories described two vulnerabilities affecting AK-SM 8xxA programs operating variations earlier than 4.3.1. CVE-2025-41451 might permit distant code execution by way of command injection, whereas CVE-2025-41452 might trigger a denial-of-service situation by way of internet interface configuration adjustments.
Each require authentication earlier than exploitation however spotlight the dangers posed by susceptible refrigeration administration tools.
Hospitals May Face Comparable Refrigeration Dangers
The assaults in France present how altering refrigeration settings may cause real-world losses with out deploying damaging malware. In hospitals, related interference might spoil vaccines, medicines and different temperature-sensitive provides.
Forescout warned that assaults on these programs can have “bodily and monetary penalties” even when attackers use official management features moderately than damaging malware. Its analysis doesn’t report confirmed assaults on hospital refrigeration networks, however the variety of uncovered programs raises questions on how nicely these gadgets are protected.
Many refrigeration programs could be accessed remotely for upkeep, generally by third-party contractors chargeable for a number of websites. Forescout warned that stolen or shared contractor credentials might put these programs in danger, notably when their administration interfaces are uncovered on-line. An attacker with entry might alter temperatures or defrost settings with out deploying malware.
Forescout recommends proscribing direct web entry, securing distant connections, giving contractors particular person accounts with multifactor authentication, patching susceptible programs and monitoring uncommon adjustments to settings or alarms.
Consultants Warn of Dangers to Hospitals and Essential Infrastructure
Damon Small, board member at Xcape Inc., shared with Hackread.com his considerations in regards to the potential impression on healthcare amenities.
“Unprotected refrigeration controllers signify a direct risk to medical operations and affected person security, the place even slight temperature variations can spoil irreplaceable lab specimens, degrade important prescribed drugs, and interrupt acute care,” Small stated.
He warned that attackers might manipulate refrigeration settings with out triggering bodily alarms in time, including that safety groups should deal with environmental controls as important operational property.
“If an industrial chiller is simpler to entry from the Web than your affected person portal, your safety structure has melted,” Small added.
Seemant Sehgal, founder and CEO of BreachLock, additionally shared his perspective with Hackread.com, pointing to current incidents involving refrigeration and cold-chain operations.
“Practically 13,000 refrigeration programs reachable from the general public web throughout 99 international locations is the image beneath incidents the trade has already seen this 12 months,” Sehgal stated.
He warned that hospitals ought to test which refrigeration items are accessible on-line, whether or not their software program is updated, and what occurs if temperature controls cease responding exterior regular working hours.
“A pentest of the refrigeration atmosphere, particularly what an attacker might attain and alter from the controllers themselves, is the appropriate technique to reply these questions earlier than another person solutions them throughout an incident,” Sehgal added.
(Photograph by Jude Ballado by Pexels)