A financial institution doesn’t essentially want an actual department, banking licence, or perhaps a real enterprise to look convincing on-line anymore. A phishing marketing campaign Netskope Risk Labs found reveals that cybercriminals can create fictional however genuine-looking banks, with account-opening pages, buyer assist particulars, and on-line banking portals, utilizing only a ready-made PHP script.
Researchers report that round 29 fake-bank domains appeared over seven weeks- beginning in late September 2026- utilizing names like Sunray Belief, Quartz Financial institution, Western Future Financial institution and Apex Belief Monetary Financial institution. These pages have been designed to gather login credentials and personally identifiable info (PII), together with names and addresses.
Geographically, North America had probably the most affected organizations, adopted by Europe and Asia whereas Finance and banking organizations had practically half of the victims.
Identical Financial institution, Totally different Names
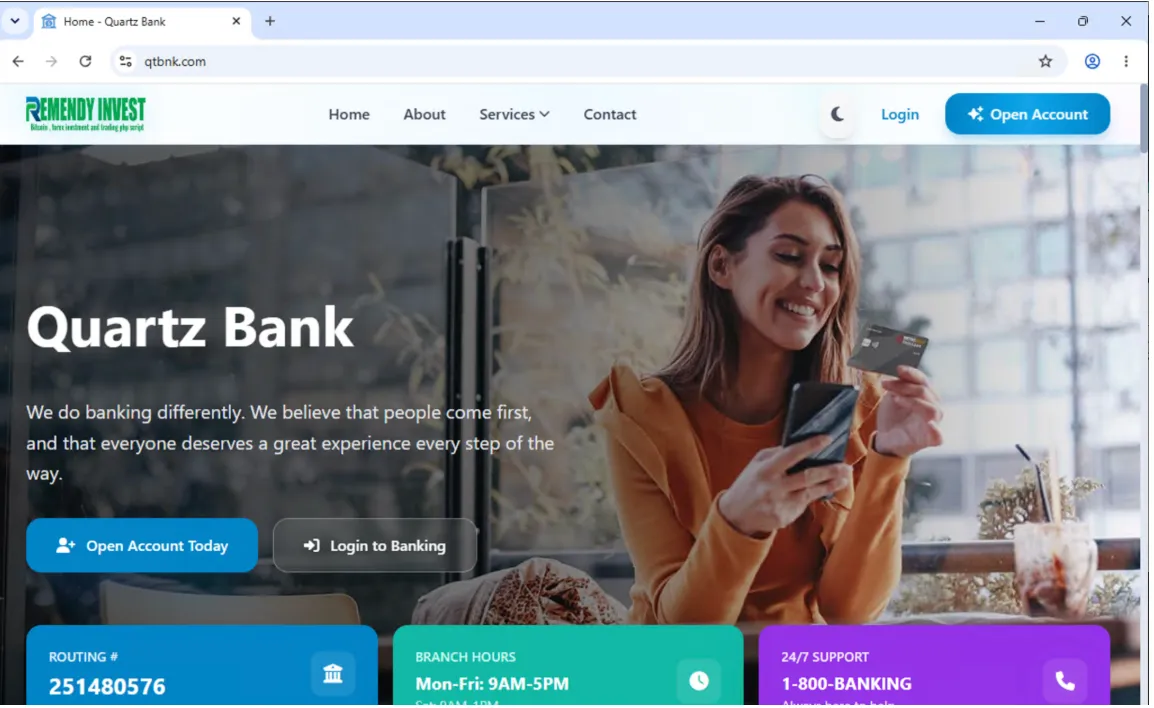
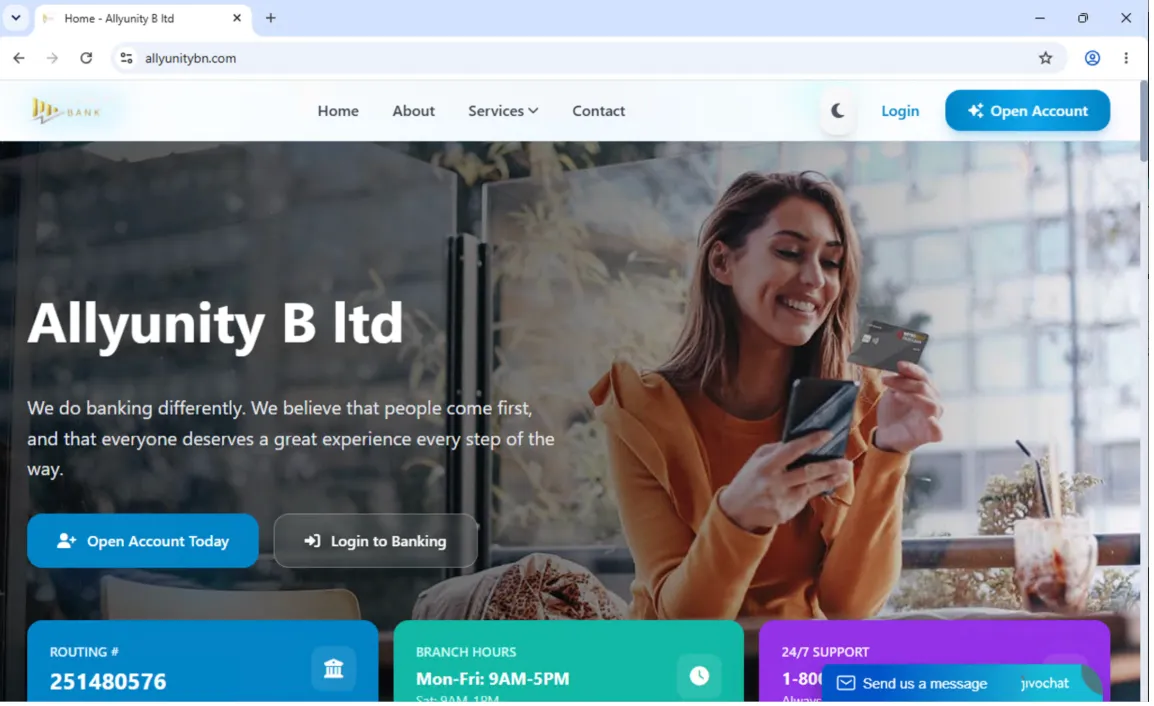
Pretend banking websites might seem like separate monetary establishments to an unsuspecting customer, however Netskope discovered that they share the identical underlying template. Their layouts, advertising and marketing textual content, assist quantity (1-800-BANKING) and even financial institution routing quantity (251480576) are an identical, other than one deployment that modifications a digit to 981480576.
The websites appeared to belong to completely different banks, however Netskope Risk Labs traced them to a single phishing package. The package gave scammers a ready-made banking web site with login and account-opening types designed to gather passwords and private info. They may change the financial institution title and reuse the remaining. On six websites Netskope examined, the identical format, tagline and assist quantity confirmed up once more, together with a routing quantity that differed by one digit on one website.
One element left behind on the now offline Quartz Financial institution’s web site (qtbnk.com) provided a clue about the place the pages got here from. Its brand carried the unique template branding: “EMENDY INVEST, Bitcoin, foreign exchange funding and buying and selling PHP script.”
Researchers imagine that the operators acquired or traded a ready-made PHP banking script and reused it with completely different financial institution names, and in addition used low-cost or abuse-friendly area extensions, together with .sbs, .cc, .professional, .dwell, .on-line and .information. The location Sunray Belief (sunraytrustbn.sbs) was detected only a day after its area was registered.
Scammers have tried their finest to make these fictional banks look established. Netskope discovered Bray Finance listed because the contact on an actual property web site whereas one other faux financial institution appeared on a enterprise info website linking on to its phishing area. Such listings may assist these names seem in engines like google and AI-generated solutions, Netskope notes, which is able to give victims another excuse to belief them.
Why Area Fame Is Not Sufficient
Round one-third of the 29 domains had no VirusTotal detections when Netskope first discovered them, whereas the remaining domains averaged fewer than 5 detections throughout roughly 90 antivirus and URL-scanning engines. Researchers additionally noticed an Allyunity Financial institution model with a CAPTCHA-evasion variant.
“These websites dwell quick and die younger,” Netskope researchers wrote within the weblog submit shared with Hackread.com, explaining that operators can abandon domains earlier than reputation-based safety instruments have time to flag them.
Listing of websites noticed within the rip-off:
qtbnk.com
norexgo.com
1stggbinc.cc
oakmontfb.com
allyunitybn.com
gulfcoastcu.org
premiummaya.com
vaultroyalb.com
ardenovabank.com
glariontrust.com
kinoxcapital.com
northgatebnk.com
financial institution.firstcp.dwell
sunraytrustbn.sbs
brayfinance.on-line
corepayfinance.com
heritageprivate.cc
sterlingtrusts.professional
alliancetrustcu.professional
apextrustfinbank.com
westernfuturebnk.com
westlinedigital.information
clyntelitecapital.com
northfieldreserve.com
swiftpremiumcapital.com
hyperionglobalholdings.com
globalheritagestandards.com
securecapitalcorporationlimited.com
ubnazionale.dwell.loadingloading.com.ng
Hackread.com has beforehand coated ready-made banking phishing instruments, together with the Spiderman package, which cloned authentic European banks and cryptocurrency companies; nonetheless, this marketing campaign takes a unique method altogether. It doesn’t impersonate established banks; it offers criminals fictional monetary establishments they will put on-line utilizing the identical template.
The essential clue for defenders is that the area title might change, however the web site’s underlying particulars don’t. Repeated routing numbers, contact info and web page parts can expose the following faux financial institution even earlier than safety scanners recognise its area.