For thousands and thousands of customers, Prime Large Deal Days on 6 and seven October are about grabbing a discount earlier than the festive rush. For cybercriminals, it’s harvest season, and so they’ve laid the groundwork effectively prematurely.
Two separate research revealed forward of the occasion level in the identical path. KnowBe4‘s Risk Lab says Amazon impersonation assaults surged by 188% between late August and September. Test Level Analysis, in the meantime, discovered that newly registered Amazon- and Prime Day-related domains have risen for 3 months operating, from 905 in July to 1,284 in September, a 42% soar, and 37% increased than the 937 recorded in September 2025.
The tip purpose is acquainted: account takeover, fee card harvesting and malware distribution. What has modified is the polish, scale and regional precision with which the assaults are being delivered.
Constructing the infrastructure
In response to Test Level, round 6.5% of the Amazon-themed domains registered in September had been labeled as malicious or suspicious by its ThreatCloud platform. That’s one in each 16 new domains. KnowBe4’s personal monitoring picked up greater than 700 new Amazon-themed domains in a single three-week window forward of the occasion.
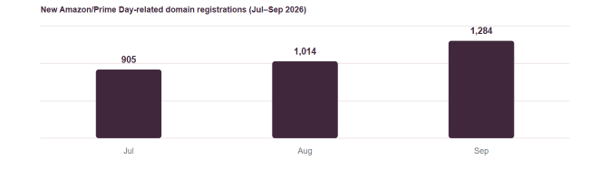
New Amazon/Prime Day-related area registrations, July to September 2026. Supply: Test Level Analysis
Examples flagged as malicious between July and September embrace amazonprime-support[.]com, primevideoamazon[.]com, prime-amazonfr[.]com and amazonprimeusa[.]com. Researchers additionally discovered faux Amazon login pages concentrating on customers in Japan, Vietnam and the UK.
Among the exercise is clearly coordinated. One cluster, which Test Level has dubbed the AmazonShopping/ShoppingOnAmazon Numbered Community, includes eleven associated domains, ten of them malicious, and seems designed to imitate storefronts and checkout flows. A second, the AmazonGlobal Numbered Domains, consists of 5 equally structured domains aimed toward worldwide customers, all malicious. Researchers additionally uncovered full faux Amazon storefronts in Germany and Japan, and even a website concentrating on Amazon’s supply accomplice programme in India.
Engineered to evade
KnowBe4’s information suggests attackers are investing closely in getting previous electronic mail defences. Three-quarters (75%) of the Amazon-themed assaults it analysed had been polymorphic, continually altering show names, topic strains or sending domains to dodge pattern-matching. Nearly two-thirds (64%) used technical obfuscation equivalent to zero-width areas and hidden characters, and greater than 95% relied on hyperlinks resulting in faux fee gateways or credential-harvesting pages, full with cloned logos, buttons and footer disclaimers.
The most important campaigns, themed round account safety alerts or supply updates, averaged 86 phishing assaults every. In a single high-volume operation, attackers despatched faux ‘suspicious login exercise’ warnings from a sprawling mixture of free webmail and burner accounts, rotating senders to dilute detection alerts.
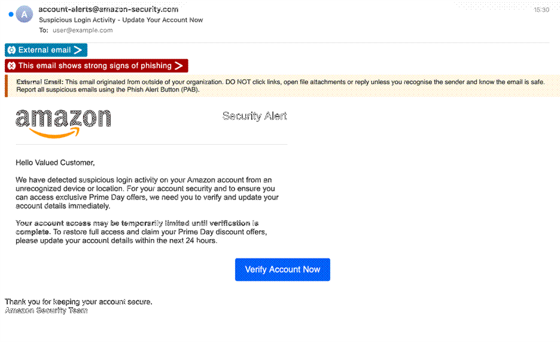
A credential-harvesting electronic mail posing as an Amazon safety alert, urging recipients to ‘confirm’ their account to maintain entry to Prime Day presents. Supply: KnowBe4
One other marketing campaign, aimed toward UK and US mailboxes, used generative AI to churn out personalised offers whereas dynamically rewriting topic strains. Though it claimed to be from Amazon, the true sender traced again to infrastructure linked to a professional multi-cryptocurrency pockets app, probably abused or spoofed to borrow its area fame. The malicious hyperlink was hidden behind a clickable picture slightly than textual content, and victims had been bounced to a faux information website performing as a trusted entrance for credential theft.
In Japan, attackers used white-on-white textual content, embedding invisible random characters within the HTML to confuse scanners whereas remaining unseen by the recipient. The emails got here from freshly registered domains constructed to defeat legacy domain-age checks.
What the lures appear to be
Account and billing scares are the only greatest class, however freebies and supply notices should not far behind:
| Lure theme | Share of world assaults |
| Prime billing, account renewal or ‘login detected’ | 31% |
| Free reward or reward | 29% |
| Supply discover | 25% |
| Restricted-time supply | 15% |
Share of world Amazon-themed phishing assaults by lure theme. Supply: KnowBe4
A localised playbook
Whereas campaigns are broadly sprayed at scale slightly than individually focused, KnowBe4 discovered attackers tailoring their lures to native habits and anxieties:
- United Kingdom: Supply and parcel traps dominate, with pressing ‘verify your supply tackle’ and missed-parcel notices designed to push customers to faux address-verification pages.
- United States: 76% of assaults concentrate on billing issues or membership renewals, taking part in on concern of dropping Prime advantages.
- Germany: 85% of assaults had been delivery-based. Germany was additionally hit by a wave of the Japanese marketing campaign between 27 and 29 September, utilizing ‘Amazon.co.jp’ show names laced with invisible characters.
- France: Though round 75% of Amazon assaults globally had been in English or Japanese, over 90% of these aimed toward French targets had been natively translated, dangling ‘unique entry’ and expiring offers.
- Netherlands: 90% of assaults pushed faux ‘Prime Day presents’. Dutch inboxes additionally obtained the French marketing campaign from 22 September and the Japanese one in the identical week as Germany, suggesting the latter was despatched globally.
- UAE: In contrast to the remainder of EMEA, each assault was a ‘reward alert’ or ‘you have got received’ lure, all in English and unfold evenly throughout September with no peak week.
- Japan: Excessive-urgency account verification and suspicious-login notices despatched from newly created lookalike domains.
AI is erasing the outdated warning indicators
Each companies spotlight the function of generative AI. Test Level warns that AI instruments let risk actors quickly produce well-written, localised phishing messages and convincing duplicate web sites at scale, stripping out the spelling errors and clumsy phrasing that customers have lengthy relied on to identify a faux. The French campaigns’ native-quality translations and the personalised UK and US lures documented by KnowBe4 are circumstances in level.
Stress builds on the companies behind the sale
The chance doesn’t cease with shoppers. Test Level says monetary companies organisations, the banking and funds infrastructure that clears Prime Day purchases, confronted a mean of two,650 assaults per organisation per week in September. That’s up 14% on August and 66% year-on-year, far outpacing the 48% enhance seen throughout all industries.
Shopper items and companies organisations, the retailers, marketplaces and electronics sellers really operating the sale, recorded 2,578 weekly assaults per organisation, up 22% month-on-month and 52% year-on-year. Test Level argues this underlines the necessity for retailers, fee suppliers and banks to establish and block malicious domains and phishing earlier than they attain clients, slightly than cleansing up afterwards.
Pause earlier than you click on
Lucy Gee, Lead Risk Analyst at KnowBe4, stated: “As Prime Large Deal Days method, cybercriminals rely closely on our concern of lacking out. A very powerful factor shoppers can do is pause earlier than clicking. If an electronic mail warns that your account is locked, your fee failed, or that you just’ve received a free prize, don’t use the hyperlinks in that message. Navigate on to the official Amazon app or web site to examine your account standing, hover over hyperlinks to examine the actual net tackle, and bear in mind: if a deal or supply seems to be too good to be true, it nearly actually is.”
Drawing on recommendation from each firms, customers ought to:
- Go direct. Entry Amazon by means of the official app or by typing the tackle, by no means by way of hyperlinks in emails, texts or social media adverts.
- Test senders and URLs. Hover earlier than clicking and look out for hyphenated lookalikes equivalent to amazon-support-login.com.
- Recognise strain techniques. Countdown timers, supply failure warnings and suspension threats are basic crimson flags.
- Don’t depend on unhealthy grammar. AI-generated scams can look polished {and professional}.
- Activate MFA or passkeys. Stolen passwords are far much less helpful and not using a second issue.
- Watch your statements and report something suspicious immediately.
With malicious domains nonetheless showing and phishing campaigns already in full swing, the message from researchers is obvious: the offers might final 48 hours, however the fallout from a single careless click on can final for much longer.
The put up Prime Large Deal Days: scammers top off early as Amazon impersonation assaults almost triple appeared first on IT Safety Guru.