A chronic Partisan Zmiy intrusion right into a medical group, exposing an up to date malware toolkit that mixed Telegram command channels, DNS tunneling, and scheduled payload execution.
Investigators joined the response in December 2025 and traced the earliest proof of compromise to early 2024, indicating roughly two years of entry with out noticed harmful exercise.
The group maintained intensive infrastructure and bidirectional belief relationships with subsidiary medical establishments.
Researchers assess that preserving these connections could have supplied higher worth for espionage and subsequent assaults than quick disruption.
Attribution rested on Vasilek malware, overlapping command infrastructure, and established ways related to Cyber Partisans.
The investigation started after scanning exercise originated from a subsidiary medical group.
Historic antivirus detections recognized Vasilek and GOST, whereas early command execution artifacts matched Impacket’s wmiexec.py: command output redirected by the localhost ADMIN$ share into timestamped recordsdata.
Attackers maintained persistence by Home windows companies and malicious DLLs masquerading as system elements.
Service creation data remained in Home windows System logs beneath Occasion ID 7045. As a result of operators repeatedly changed payloads at similar paths, filenames alone couldn’t reliably determine which instrument had occupied every location.
A beforehand undescribed loader, authd.exe, ran because the “VMware Auth Adapter” service contained in the reliable VMware Instruments listing.
It orchestrated GOST and Vasilek payloads hid as vmtoolsd32.exe, rpctool32.exe, and WsusService.exe.
The Photo voltaic 4RAYS workforce encountered one other assault, by Partisan Zmiy (the Cyber Partisans group is designated as extremist and its actions are banned in Russia), this time concentrating on a medical group.
Partisan Zmiy Malware
The scheduler activated one GOST tunnel each Saturday between 22:00 and 23:00. Two further payloads launched as soon as, eight hours after service startup.
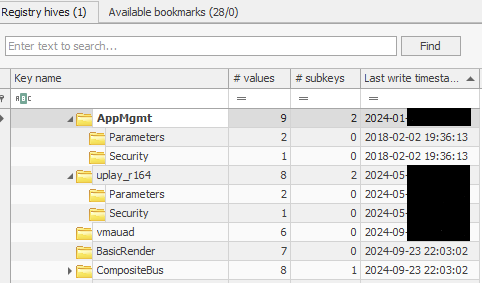
Whereas analyzing the malicious exercise, we found modifications to the registry key tags of the reliable
AppMgmt service.
Researchers interpreted the restricted window as a probable backup channel and the delayed execution as an effort to separate malicious site visitors from startup exercise.
Shortly earlier than discovery, operators changed VMware’s signed vmtools.dll with an unsigned Vasilek library, retaining the unique as vmtoolsd.dll.
The software program listing was reliable however operationally uncared for, offering an efficient concealment location.
Vasilek model 1.5.8 is a 32-bit Home windows backdoor managed by Telegram group messages.
Its command desk incorporates 59 entries, together with aliases, supporting shell execution, file transfers, screenshots, keylogging, clipboard assortment, and course of administration.
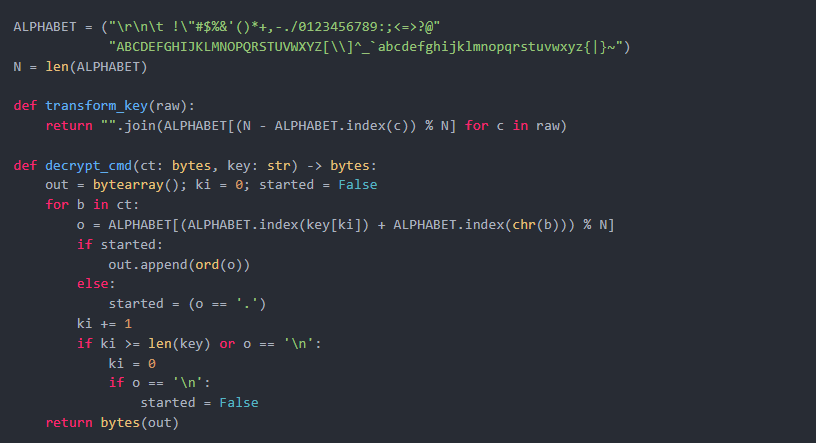
Operators retrieved instructions by getUpdates lengthy polling and returned outcomes utilizing Telegram’s Bot API.
Group-based nameless posting hid the sender’s account, whereas job identifiers helped operators affiliate responses with particular person instructions.
Earlier than execution, Vasilek in contrast a salted SHA-256 hostname hash towards a hardcoded worth, proscribing operation to the supposed machine.
OLLVM-based control-flow flattening, encrypted strings, and dynamically resolved APIs additional difficult evaluation.
Kaspersky ICS CERT’s June 2025 analysis beforehand documented Vasilek’s Telegram management structure and hostname-dependent execution, establishing the technical baseline for this up to date investigation.
Telegram was just one entry route. DNSCat2, PartisanDNS, and a GOST–3proxy chain offered different connectivity, stopping disruption of 1 channel from routinely eradicating entry.
Noticed domains included c0ce[.]org, p7cp[.]org, w3a01[.]internet, f91j[.]org, and the reused gov-by[.]com. These indicators overlapped with, or intently resembled, infrastructure documented in earlier Cyber Partisans analysis.
Investigators additionally discovered proof suggesting momentary modification and restoration of the reliable AppMgmt service.
Public instruments reminiscent of NimExec help comparable service-path manipulation, though their availability doesn’t set up their use on this incident.
The case underscores the significance of investigating recurring detections, auditing service modifications, verifying signatures in trusted software program directories, and correlating suspicious DNS site visitors with sudden messenger API connections throughout interconnected healthcare environments.
IOCs
| Hash sort | Hash worth |
|---|---|
| MD5 | a6af32b1381d8985049e2d5ec1889bd9 |
| MD5 | 338f7eafdfe45e93e57889ebd064d0d5 |
| MD5 | 39e64553b7ddf579240e6642042e6840 |
| MD5 | a6ce67f063fce60954bb6cea4c969aac |
| MD5 | 1199d2f2b1a58435113555b02172bc79 |
| SHA1 | bdeac4b8e9a3c48661adf0c2ee5f05b58cee76eb |
| SHA1 | ed999aaaf1d032c76a51f4aececb99d06c371b33 |
| SHA1 | cd61f92873625dd25a31f414617347d1fa132747 |
| SHA1 | 56df605a33fb77c91bdb92033efe983f336deb23 |
| SHA1 | efe3503bd021de67e884878c6de1e8b110ed2ee7 |
Be aware: IP addresses and domains are deliberately defanged (e.g., [.]) to forestall unintentional decision or hyperlinking. Re-fang solely inside managed risk intelligence platforms reminiscent of MISP, VirusTotal, or your SIEM.
Stops Cyber threats earlier than influence with 21 min quicker MTTR. Combine ANYRUN’s Sandbox in your SOC.