Chinese language state-sponsored hacking group Volt Storm has exploited a number of beforehand unknown vulnerabilities in enterprise administration platforms to penetrate strategically vital organizations.
Its investigation uncovered Silent Prepare, a covert entry framework constructed from quickly rotating chains of compromised gadgets.
Over three years, Black Lotus Labs issued a whole lot of sufferer notifications, serving to investigations uncover 4 confirmed zero-day campaigns and one doubtless marketing campaign.
The central discovering is consequential: fairly than navigating enterprise networks host by host, Volt Storm focused centralized techniques that already possessed administrative entry, credentials and trusted connections to downstream environments.
Silent Prepare routed operations by way of abroad digital non-public servers and compromised non-U.S. gadgets earlier than reaching home relay nodes close to American targets.
These U.S. exit factors helped malicious visitors mix into reputable exercise and evade geographic restrictions.
Researchers noticed greater than 27 gadget lessons, together with SOHO routers, IoT tools and enterprise home equipment.
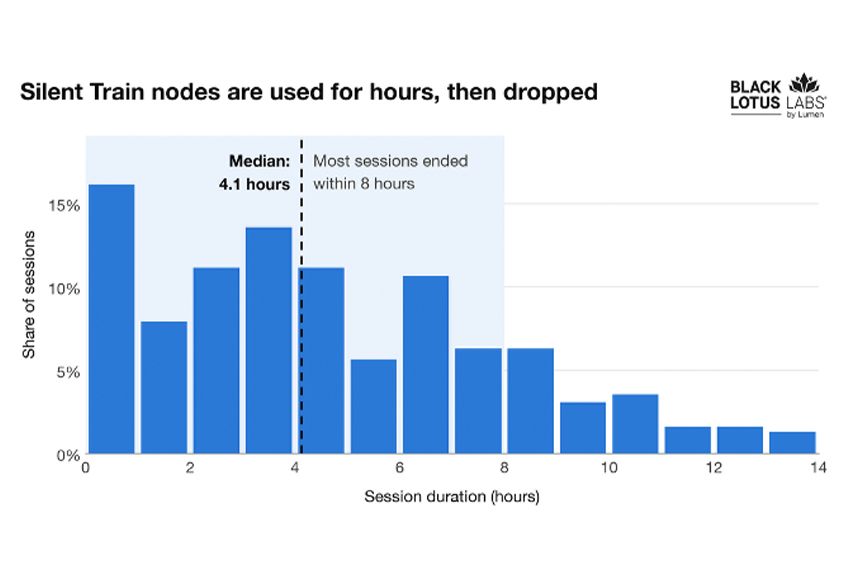
Operators might assemble relay chains in below two minutes, conduct focused exercise and take away non permanent SSH providers, keys and configuration artifacts afterward.
Classes averaged roughly 4 hours, though some lasted solely minutes. Machine roles remained compartmentalized: Intelbras modems appeared as abroad relays, whereas Netgear Orbi gadgets operated as U.S. hops speaking with victims.
By early 2025, the structure included compromised enterprise platforms that remained out there for one to 3 months.
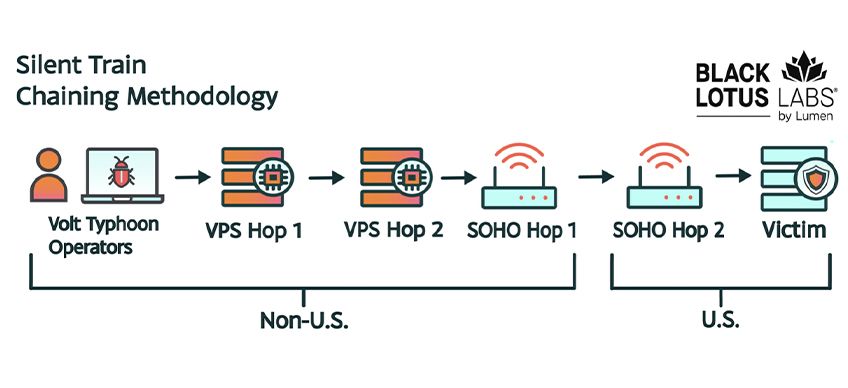
Conventional SSH chains operated alongside reverse tunnels utilizing Chisel and FRP, generally inserting six middleman hops between operators and victims.
Silent Prepare Researchers mentioned that, the framework supported operations in opposition to telecommunications suppliers, authorities companies, protection contractors, universities, and important infrastructure operators.
Zero-Days Exploited
The campaigns targeting endpoint administration, community administration and software-defined extensive space community orchestration.
Compromising these management planes supplied broad visibility and privileged performance whereas lowering lateral motion and related forensic proof.
In Quest KACE environments, greater than 30 victims had been affected. Restricted logging prevented identification of the underlying vulnerability, leaving the zero-day evaluation at reasonable confidence.
Researchers noticed credential theft and exfiltration straight from administration servers.
Different campaigns concerned Versa Director and N-able N-central. N-able’s launch notes verify that CVE-2025-8875 and CVE-2025-8876 require authentication and had been addressed in N-central 2025.3.1, an vital distinction from unauthenticated entry factors.
Volt Storm additionally exploited Cisco Catalyst SD-WAN vulnerability CVE-2026-20127. Cisco charges the authentication bypass at CVSS 10.0; profitable exploitation supplies privileged entry and might allow SD-WAN configuration manipulation by way of NETCONF. Cisco disclosed the problem on February 25, 2026.
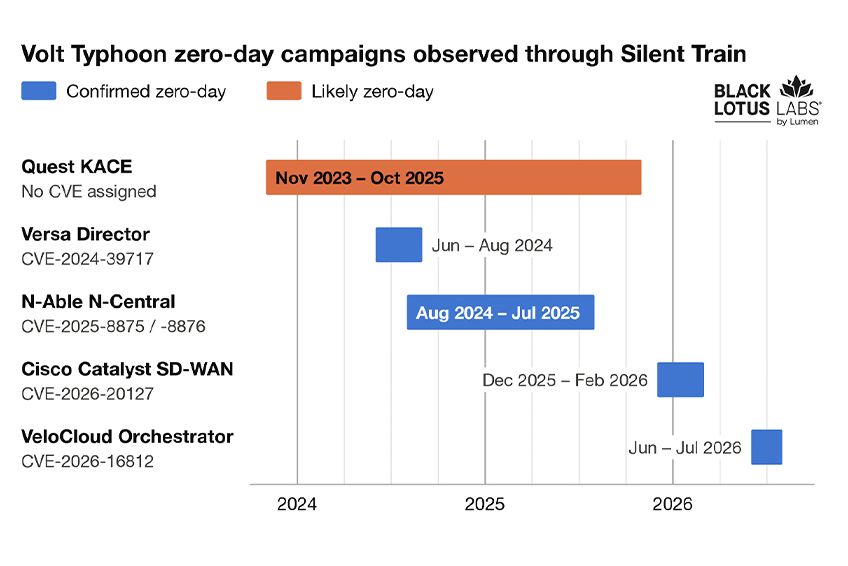
VeloCloud Orchestrator turned one other goal by way of CVE-2026-16812. Arista’s advisory describes a CVSS 10.0 command-injection vulnerability reachable with out tenant or operator credentials and confirms energetic exploitation.
Concentrating on repeatedly concentrated in Hawaii, California and Texas, spanning communications, logistics, protection and important providers.
Black Lotus Labs assesses the sample as in line with pre-positioning entry inside ecosystems vital throughout Indo-Pacific crises, fairly than proof of an noticed disruptive assault.
Defenders ought to prioritize administration infrastructure: take away pointless web publicity, deploy vendor fixes, limit administrative entry and protect telemetry exterior probably compromised home equipment.
Cisco particularly recommends reviewing unauthorized “Accepted publickey for vmanage-admin” occasions and validating control-plane peering connections.
For VeloCloud deployments, Arista advises preserving entry, software, system and database logs earlier than remediation the place possible.
Suspected compromises additionally warrant credential rotation, managed-device validation and restoration from trusted sources not patching alone.
Stops Cyber threats earlier than influence with 21 min quicker MTTR. Combine ANYRUN’s Sandbox in your SOC.