Disclosure: This text was offered by ANY.RUN. The knowledge and evaluation introduced are primarily based on their analysis and findings.
Cybercriminals are utilizing AI to launch extra convincing phishing assaults, scale their campaigns, and discover new methods to slide previous safety defenses. For SOC groups, each missed alert or delayed investigation offers attackers extra time to steal company credentials, entry delicate information, and disrupt enterprise operations.
As investigation queues develop, safety leaders face rising operational prices, overloaded analysts, and higher publicity to pricey breaches. AI-powered malware evaluation helps organizations uncover hidden threats quicker, scale back pointless escalations, and deal with extra incidents with out rising headcount.
Why SOC Groups Are Struggling to Maintain Up with Trendy Cyberattacks
A single suspicious file or URL can set off hours of investigation. Analysts should observe redirects, study suspicious habits, examine associated threats, and doc their findings earlier than deciding what motion to take. As assaults turn out to be extra complicated, these routine duties take up helpful time that could possibly be spent responding to essential incidents.
| SOC problem | Enterprise affect |
| Hidden assault chains behind CAPTCHAs, redirects, and legit web sites | Missed threats and delayed detection |
| Repetitive guide investigations | Larger prices and slower response |
| Disconnected risk intelligence | Incomplete risk visibility and longer investigations |
| Time-consuming report preparation | Delayed escalations and response choices |
| Rising alert queues | Analyst overload and elevated threat of missed threats |
These challenges make it tougher for SOCs to analyze threats completely with out rising prices or headcount.
How AI Is Altering the Manner SOC Groups Examine Threats
AI-powered malware evaluation is taking up among the most time-consuming components of safety investigations, from following hidden assault chains to connecting associated threats and making ready incident reviews.
- AI-Assisted Automation Exposes Hidden Phishing Assaults
A current ANY.RUN sandbox investigation exhibits how AI-assisted automation can uncover hidden assault chains, saving analysts time on repetitive steps whereas giving them the liberty to take management every time wanted.
The investigation began with a PDF hosted on Adobe’s authentic platform. Inside, an embedded hyperlink led by means of further steps, together with a CAPTCHA problem, earlier than revealing a Microsoft OAuth phishing move concentrating on company accounts.
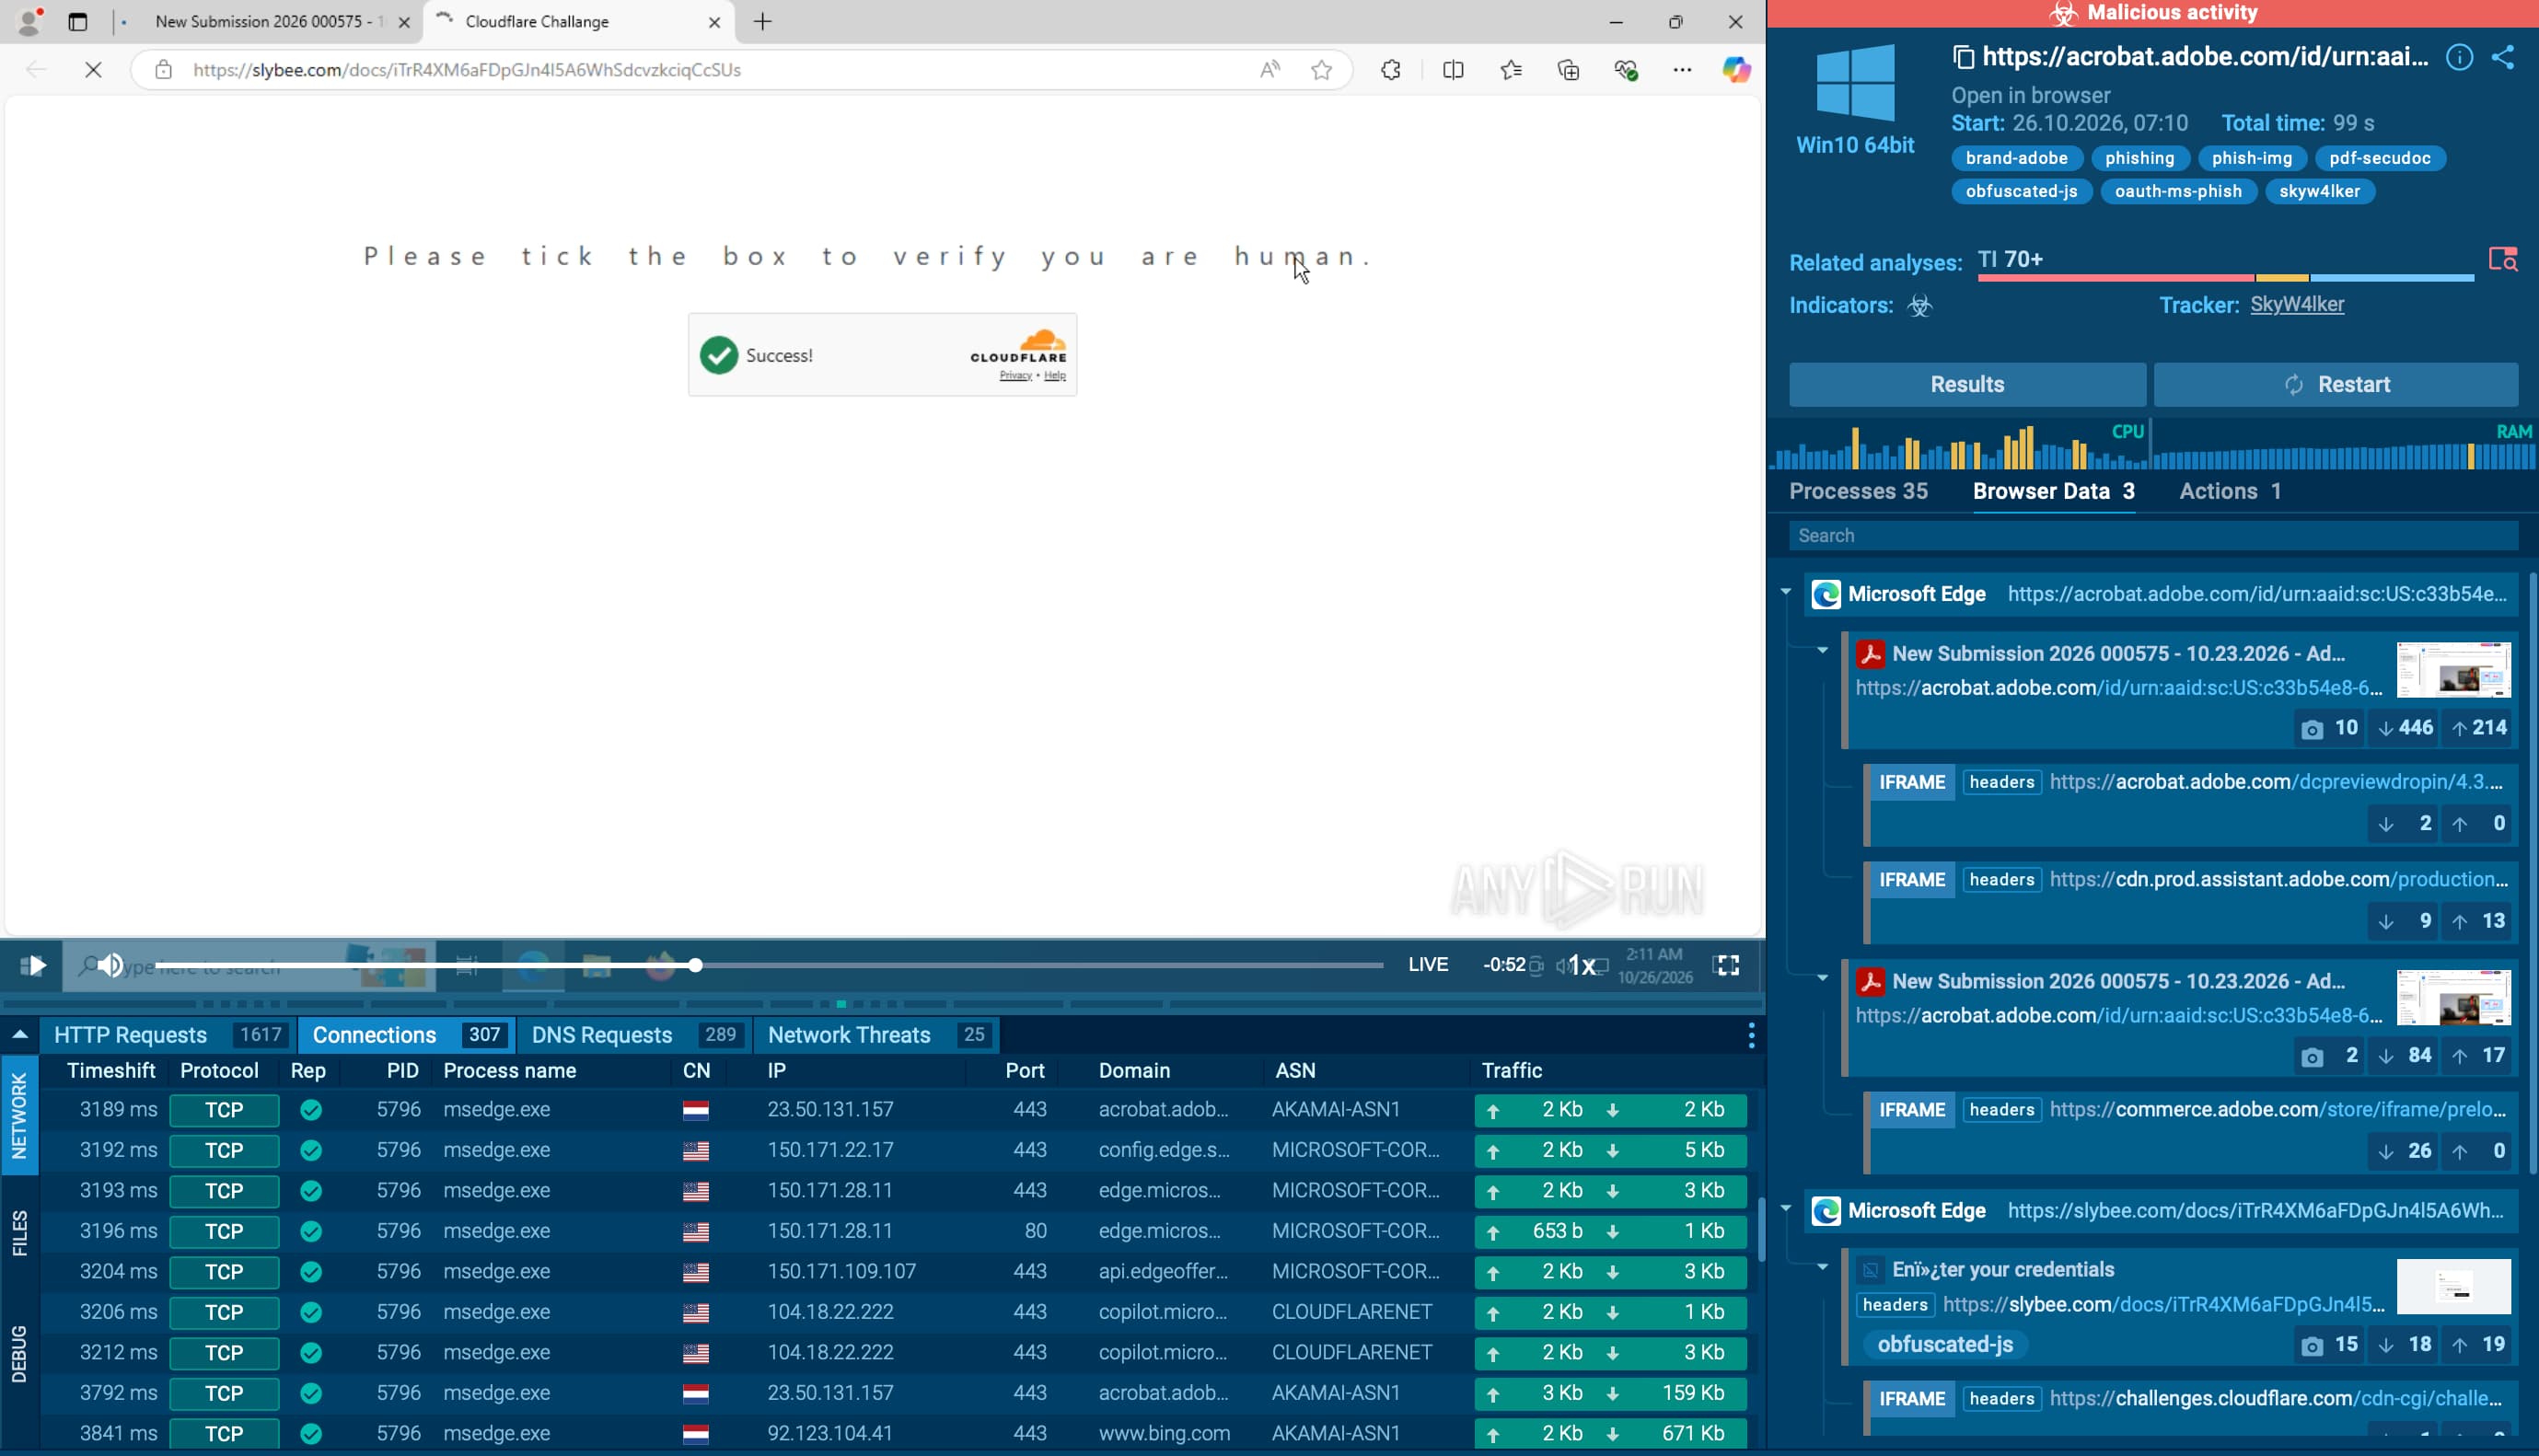
With Automated Interactivity enabled, the sandbox continued navigating the assault with out requiring an analyst to deal with each click on. The mixture of automation and interactivity meant the investigation may proceed routinely, whereas safety professionals may step in at any level to examine suspicious exercise or discover different paths.
The SOC Benefit: Much less Clicking, Extra Investigating
As an alternative of spending time manually reproducing assaults earlier than they will even assess the risk, analysts can concentrate on suspicious habits and choices that require human judgment. This helps safety groups examine extra alerts with out sacrificing visibility or management.
| Give your SOC the facility of AI to uncover hidden threats quicker, scale back guide investigations, and cease pricey incidents with out including extra analysts. |
- Associated Menace Context Speeds Up Marketing campaign Investigations
Discovering one malicious hyperlink could possibly be only the start. Behind it could be a complete phishing marketing campaign involving dozens of associated domains, shared infrastructure, and assaults which have already been investigated elsewhere. With out the appropriate context, safety groups threat treating related threats as remoted incidents.
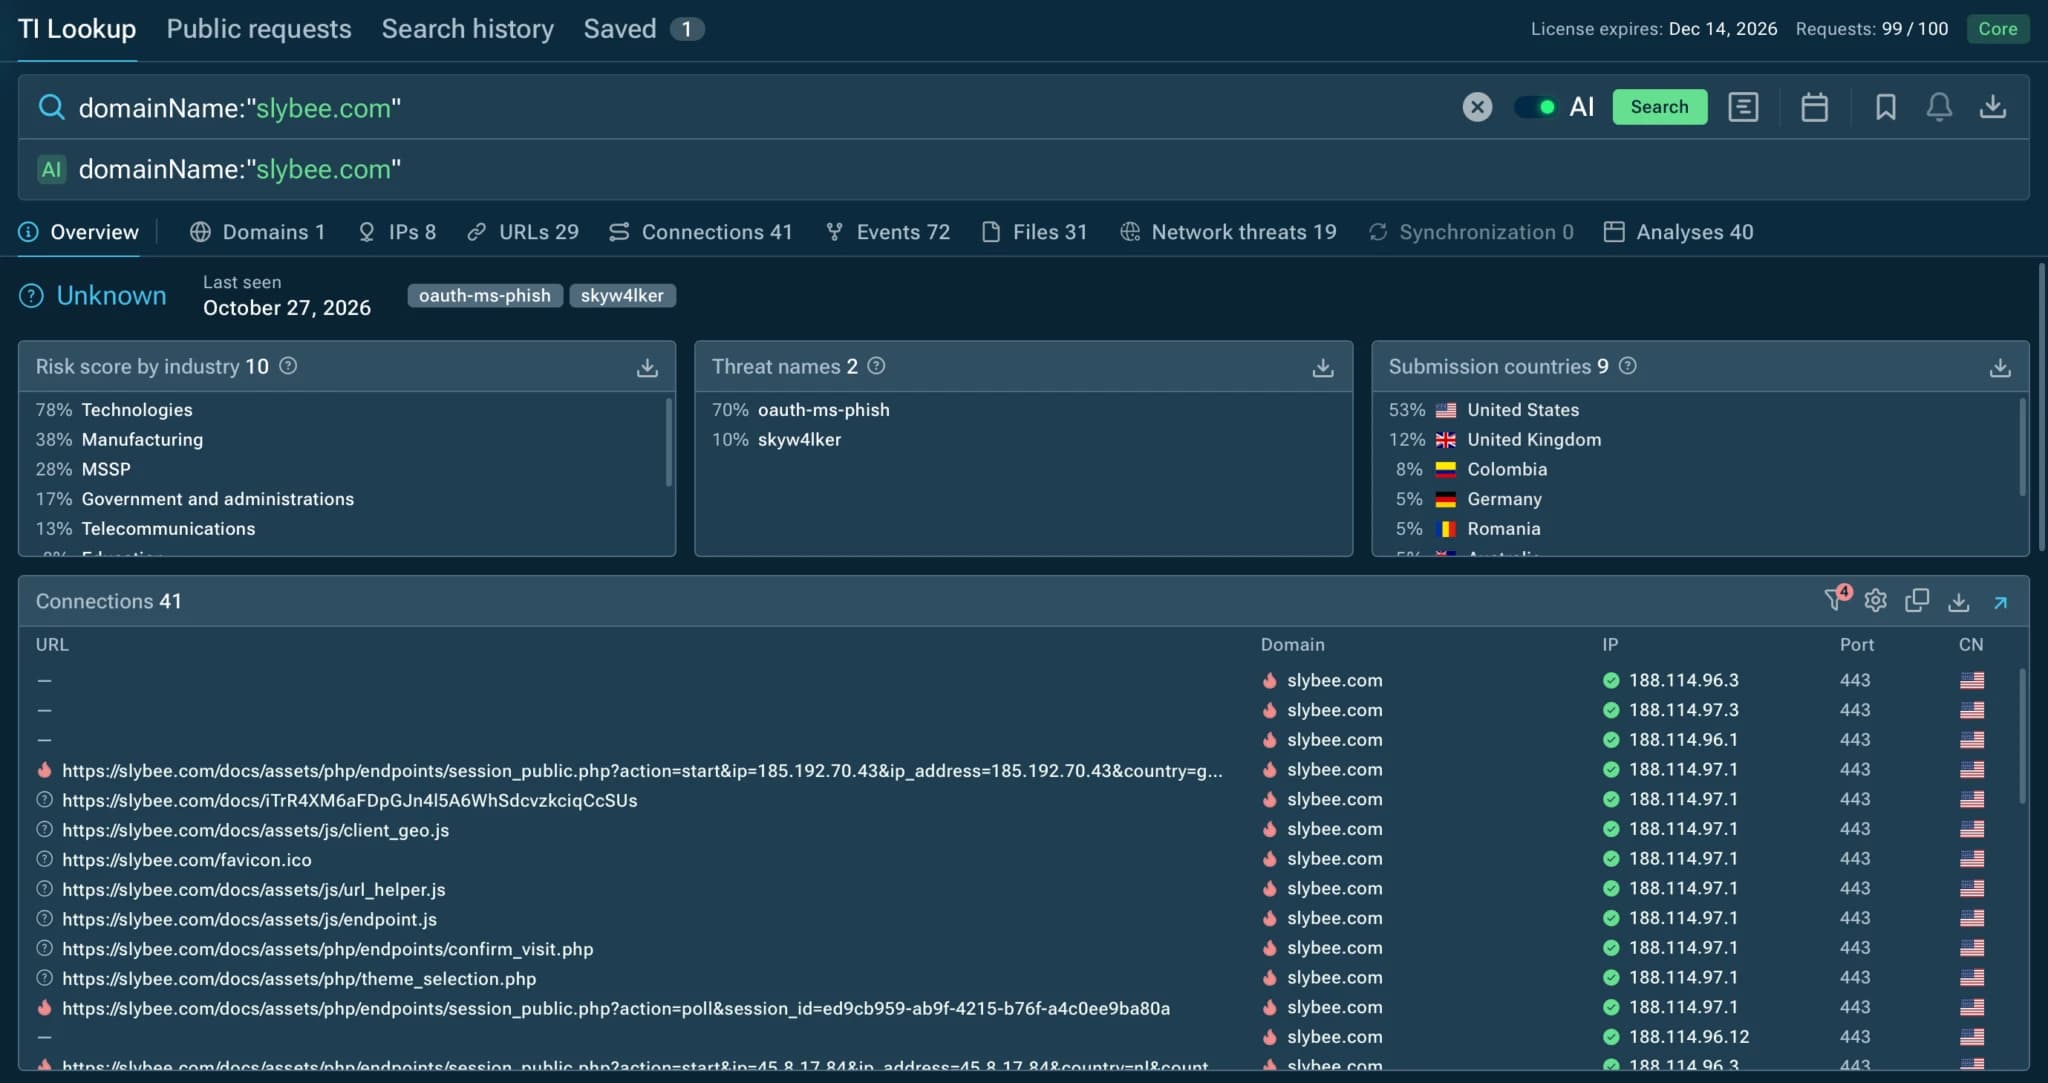
That is the place ANY.RUN’s highly effective new Associated Menace Context functionality modifications the investigation. It offers analysts a direct shortcut from a single suspicious indicator to a community of associated sandbox analyses, exposing connections throughout assaults and offering helpful intelligence with out beginning the investigation from scratch.
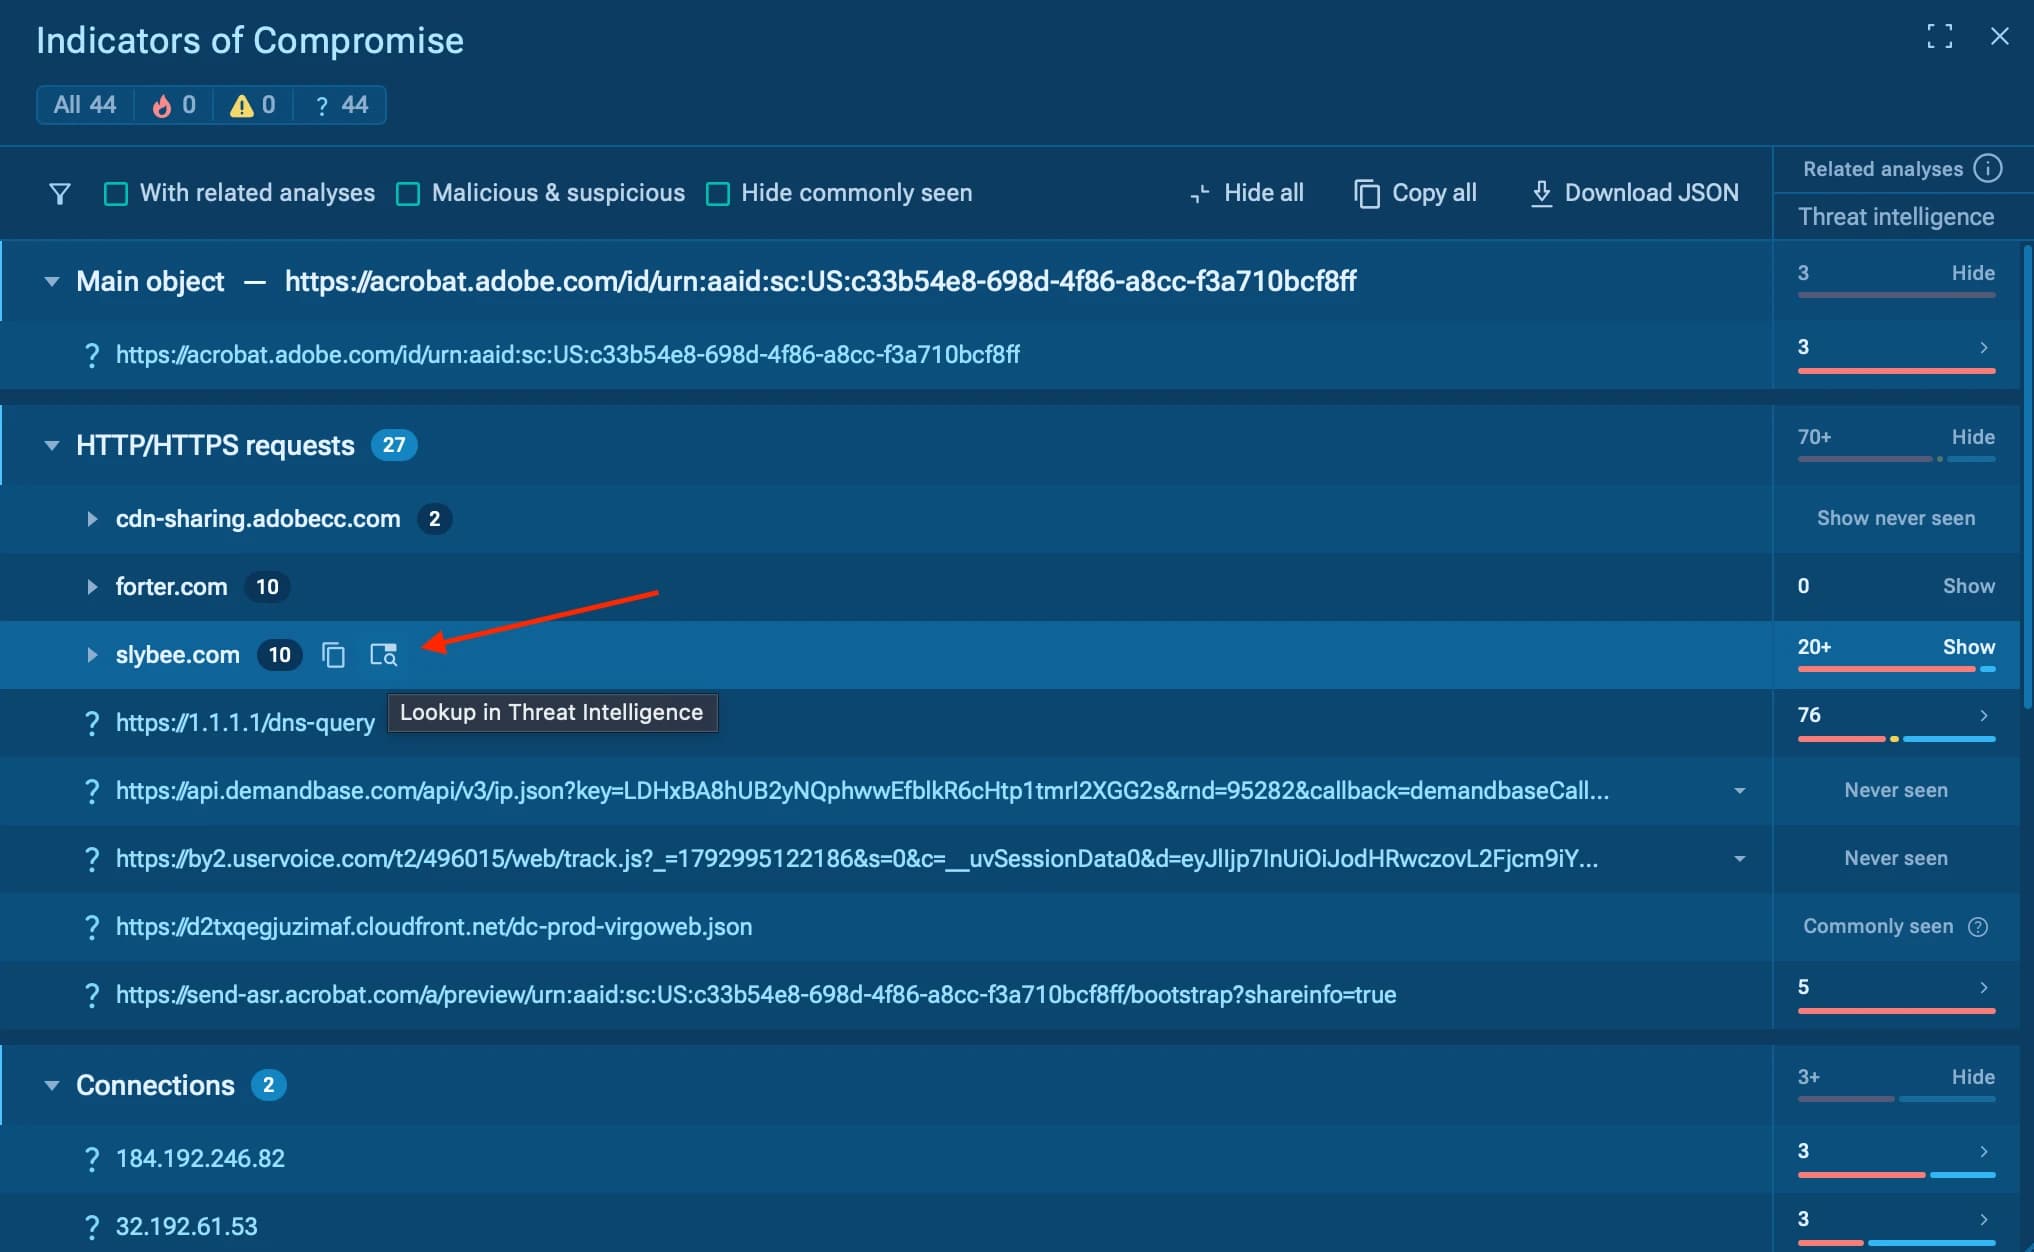
Within the Adobe PDF investigation, the potential surfaced greater than 70 associated analyses, serving to researchers hint connections to the broader SkyW4lker phishing marketing campaign. Analysts may discover associated infrastructure, earlier assault exercise, and suspicious patterns to raised perceive the size of the risk.
The SOC Benefit: Fewer Blind Spots, Sooner Response
A single investigation can now present the context wanted to make extra knowledgeable safety choices. As an alternative of losing sources on disconnected alerts, SOC groups can determine which threats are associated, prioritize high-risk exercise, and focus their response efforts the place they matter most. This implies fewer missed connections, much less repetitive work, and a decrease threat of pricey incidents.
- AI-Generated Reviews Flip Advanced Findings into Sooner SOC Choices
Uncovering a risk is just half the job. Analysts nonetheless must evaluation the proof, clarify what occurred, assess the dangers, and doc their findings for the subsequent stage of response. Making ready these reviews manually can take helpful time, particularly when a number of incidents want consideration.
AI is now serving to scale back this workload. ANY.RUN’s SOC-ready Tier 1 Report routinely brings investigation proof collectively and generates an AI Abstract explaining the noticed malicious habits, together with AI Suggestions suggesting sensible subsequent steps primarily based on the findings.
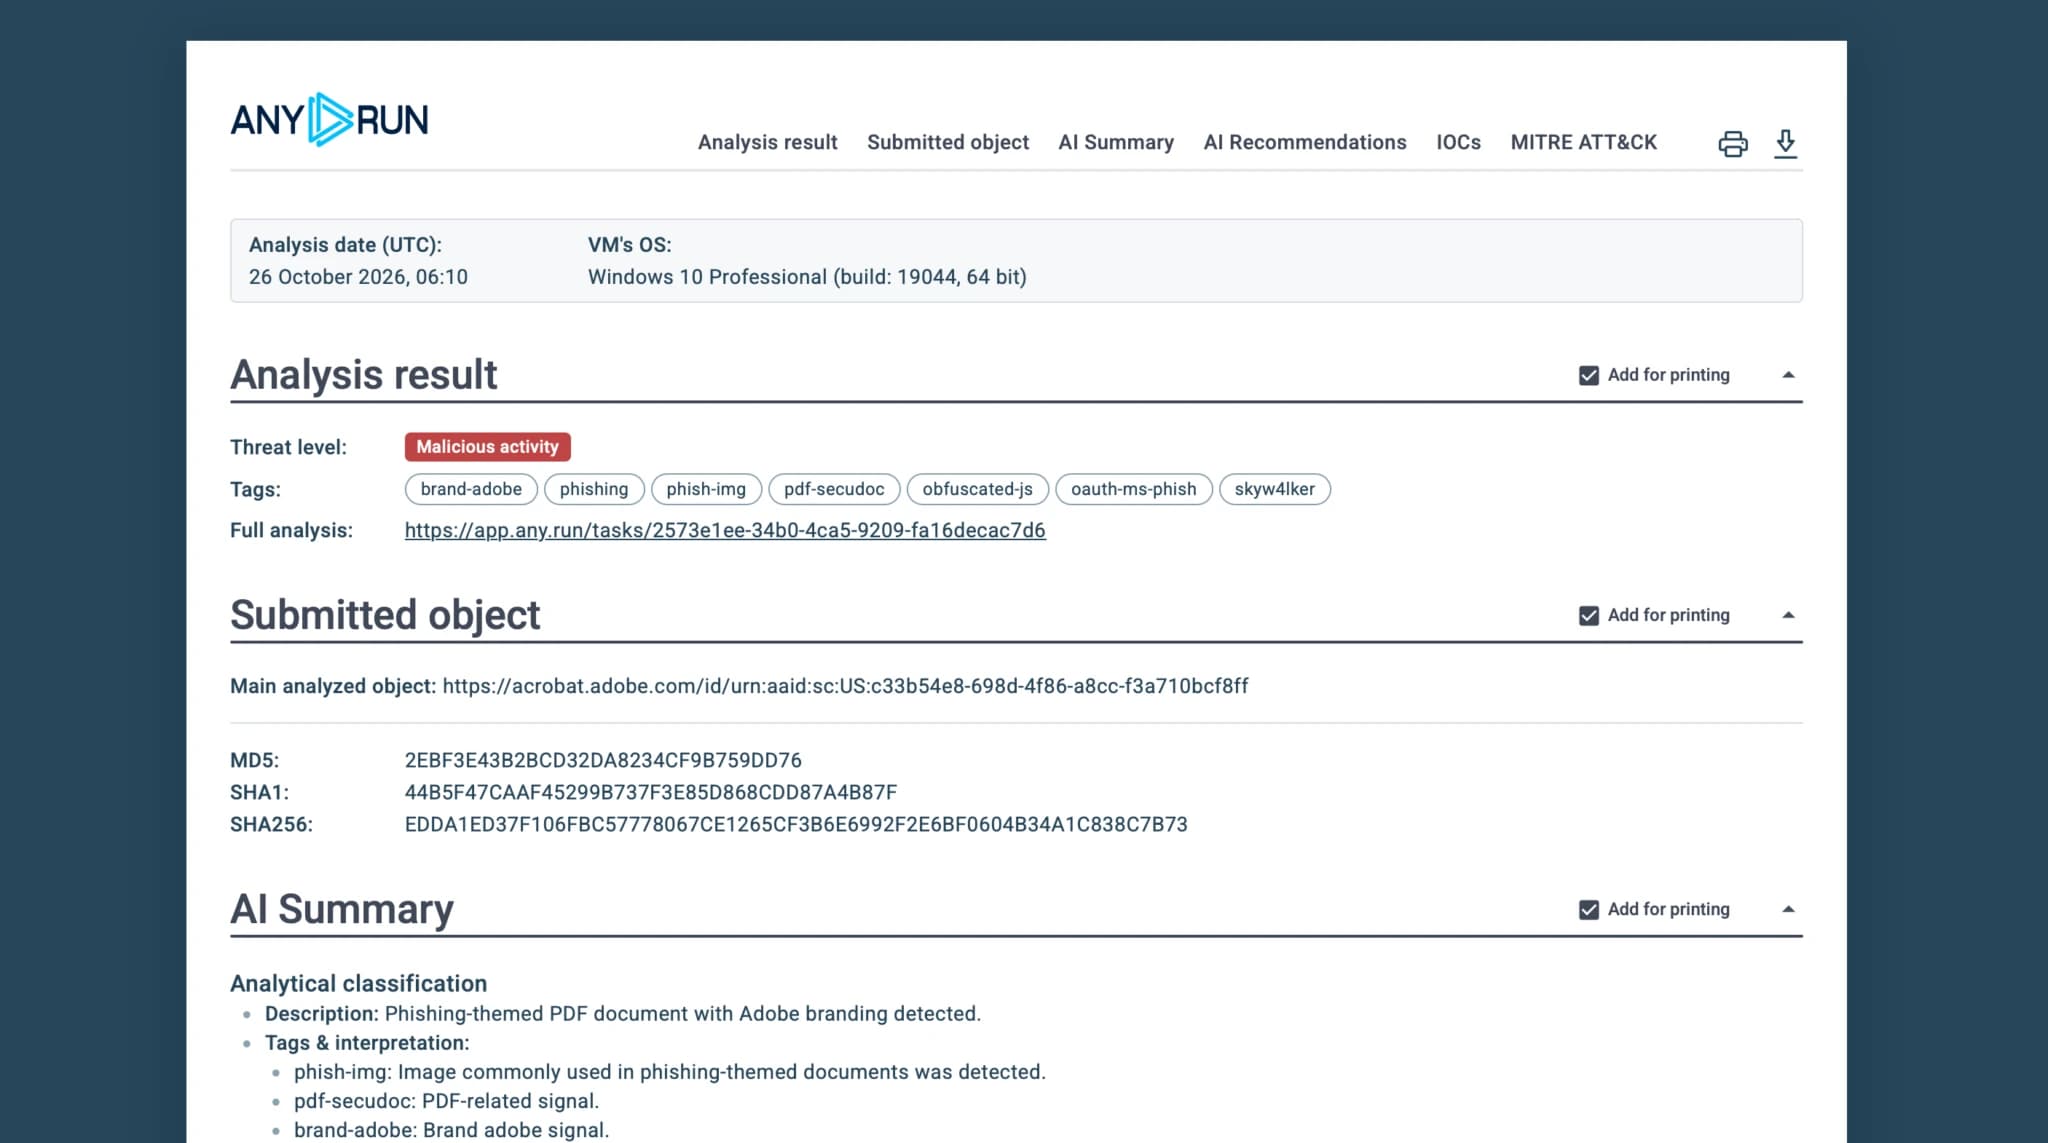
For instance, within the Adobe PDF investigation, the report helps analysts perceive the Microsoft OAuth phishing move, evaluation supporting proof, and decide what requires additional investigation or escalation.
The SOC Benefit: Sooner Choices, Fewer Escalations
With investigation findings and really helpful subsequent steps already documented, Tier 1 analysts could make quicker choices with out spending hours making ready reviews. In accordance with ANY.RUN’s reported buyer outcomes, improved investigation workflows can scale back Tier 1 workload by as much as 20% and minimize Tier 1-to-Tier 2 escalations by 30%, serving to safety groups reply quicker, keep away from duplicated work, and scale back the danger of pricey incidents.
AI-Powered SOCs: Sooner Investigations, Stronger Enterprise Safety
As cybercriminals use AI to make assaults extra refined, companies must rethink how their safety groups work. Detecting a suspicious file or hyperlink is just the start. What issues is knowing the risk, connecting the proof, and responding earlier than actual injury is finished.
AI-powered malware evaluation helps safety groups do precisely that, taking repetitive work off analysts’ shoulders whereas retaining them in command of necessary choices. This permits organizations to get extra out of their present sources, preserve prices below management, and reply to threats with higher confidence.
For safety leaders, the purpose is easy: give analysts extra time to concentrate on the threats that matter most and stop small safety incidents from turning into pricey enterprise issues.
| Scale back enterprise threat and SOC working prices with AI-powered malware evaluation that helps your safety crew deal with extra threats with out rising headcount. |