A daunting new type of Android malware was not too long ago found and unveiled by safety researchers from Zimperium. Posting on Zimperium’s weblog, the staff has shared key findings in regards to the aptly-named RatHat, an AI-powered program that disguises itself as reputable functions like Google Chrome. As soon as put in and opened, the malware will then request administrative permissions, and if given, it beneficial properties entry to ADB shell permissions via a sequence of developer instrument unlocks. From there, it installs an AI agent to run within the background and snoop in your actions and delicate info, which it sends to distant hackers, seemingly based mostly out of China, through a proxy consumer.
That is so much to digest, and there is much more complicated stuff occurring beneath the hood, however what’s significantly alarming is that the malware itself, as soon as energetic, does not do something that will give it away to most customers. It merely runs within the background stealing account names, passwords, two-factor authentication codes and different highly-sensitive info, together with messages, pictures, and way more.
There are two large defenses towards RatHat, offered your machine hasn’t already been compromised. It is largely deployed through smishing (phishing messages over textual content or different apps), and internet campaigns known as malvertising which might be designed to imitate and appear like reputable third-party obtain websites. For instance, you may see a web page making an attempt to imitate the Google Play Retailer. Avoiding installs from unknown sources, avoiding hyperlinks to app downloads in messages, and utilizing solely the official Google Play Retailer app can cut back dangers. Furthermore, companies like Google Play Shield or virus instruments like Malwarebytes Cell Safety ought to enable you to catch probably compromised sources earlier than you ever set up something.
What about telephones already contaminated with RatHat?
If a compromised app or deployment is already put in in your machine, the unhealthy information is that RatHat is tough to establish and quarantine. Worse, there’s actually just one solution to uncover if it is working in your telephone, and that is with a malware or virus instrument, once more corresponding to Malwarebytes Cell Safety. Some options embody Bitdefender Complete Safety, ESET House Safety Important, and Avira Prime, amongst others.
However there’s one thing to notice right here. Whereas respected malware and virus instruments can acknowledge RatHat, it might probably’t be simply eliminated. As a result of method the malware disguises itself and adjustments habits to stay undetected, gaining administrative entry, the one answer to oust it fully, and use your telephone safely afterwards, is to do a manufacturing unit reset. That stated, a manufacturing unit reset is nearly all the time really helpful for any machine that is been contaminated in such a method, even after they have been cleaned with malware or virus software program. Nonetheless, it isn’t a catch-all answer that cures each kind of virus or an infection. Some compromised apps and code can persist throughout resets.
If you happen to’re following all of the main CISA Android safety guidelines that everybody ought to know, you may stay comparatively secure and guarded. That is as a result of tips encourage leaving Google Play Shield energetic to vet apps, utilizing secure looking mode in Google Chrome, repeatedly reviewing and proscribing app permissions — most significantly earlier than giving them to new apps — and different sensible methods.
How one can fully keep away from RatHat
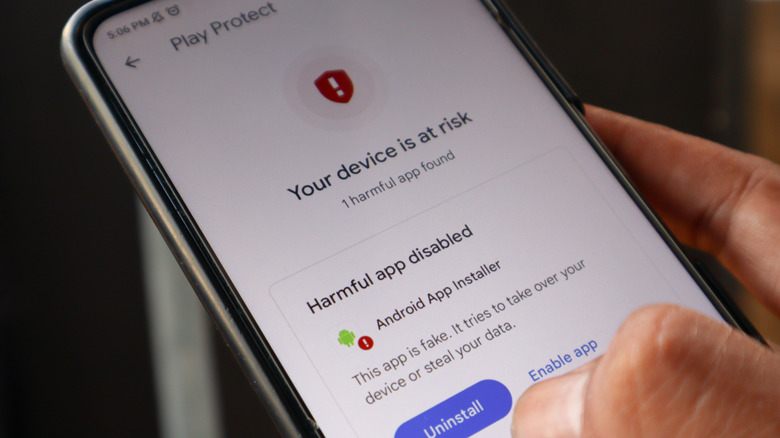
As a result of RatHat’s preliminary deployment mimics reputable set up sources, like third-party app shops, your first line of protection is keep away from putting in apps outdoors of Google Play. Do not click on on hyperlinks shared in textual content messages or in direct messages inside different apps. Furthermore, do not click on on unknown hyperlinks you see on social media or different websites, and in case you do, actually do not set up something your machine prompts you to.
To keep away from utilizing a disguised web site, take note of the URL. If it isn’t an official slug or URL, and you may’t confirm it, do not obtain something and depart instantly. To keep away from contaminated apps, set up solely from the official Google Play Retailer, preserve Google Play Shield energetic, and keep away from sideloading, through unknown sources. If you happen to see a immediate to obtain an app you have already got put in, like one other copy of Google Chrome, it is best to keep away from it. On the threat of scaring some, it is nonetheless potential to obtain compromised or malicious apps from Google Play. That is why Google Play Shield and different backups like virus instruments are important.
Lastly, even in case you unintentionally set up a compromised app, the snooping course of will not begin till after you have opened it or granted permissions. By no means blindly settle for permissions requests from new apps, and definitely keep away from giving them to apps you do not acknowledge or that seem questionable. There are app permissions that you need to simply by no means enable. Android has a built-in characteristic to assessment and alter privateness permissions you have granted up to now, as effectively. Revoking permissions will not assist if RatHat already has administrative entry, nevertheless it’s nonetheless a very good observe to remember for the long run.