Healthcare apps more and more join sufferers with a few of their most delicate data, from medical information and prescriptions to diagnostic outcomes and distant monitoring information.
This makes cell safety greater than a technical requirement. A compromised software can have an effect on affected person privateness, regulatory compliance, belief, and, in some instances, the supply of care.
For organizations investing in healthcare app improvement, safety ought to subsequently affect the product from the primary architectural choices fairly than being added shortly earlier than launch.
Perceive the Cell Risk Floor
Healthcare apps face most of the identical threats as different cell merchandise, however the penalties will be considerably greater due to the sensitivity of well being information.
As soon as an software is put in, builders not absolutely management its atmosphere. Attackers could try and intercept communications, steal credentials, manipulate the applying, exploit insecure APIs, or analyze its code by means of reverse engineering. Malware on a compromised gadget can introduce one other potential path to delicate data.
A safety technique subsequently wants to guard each affected person information and the integrity of the applying itself.
Shield Information at Each Stage
Encrypting the database is necessary, however healthcare data will be uncovered at a number of factors. It might be saved on a tool, transmitted to a backend, processed by one other service, or accessed by means of an administrative interface.
Groups ought to take into account:
- encryption for information in transit and at relaxation;
- sturdy authentication and authorization;
- safe storage of credentials and tokens;
- dependable session administration;
- API authentication and enter validation;
- role-based entry to delicate data.
Entry ought to observe the precept of least privilege. Sufferers, clinicians, directors, and assist groups ought to solely attain the knowledge essential for his or her obligations.
Make the App Tougher to Manipulate
Backend safety alone can not absolutely defend software program operating on an untrusted cell gadget.
Code hardening could make reverse engineering tougher, whereas runtime safety will help establish tampering, malicious conduct, or suspicious execution environments. Software integrity controls also can assist detect modified variations of an app.
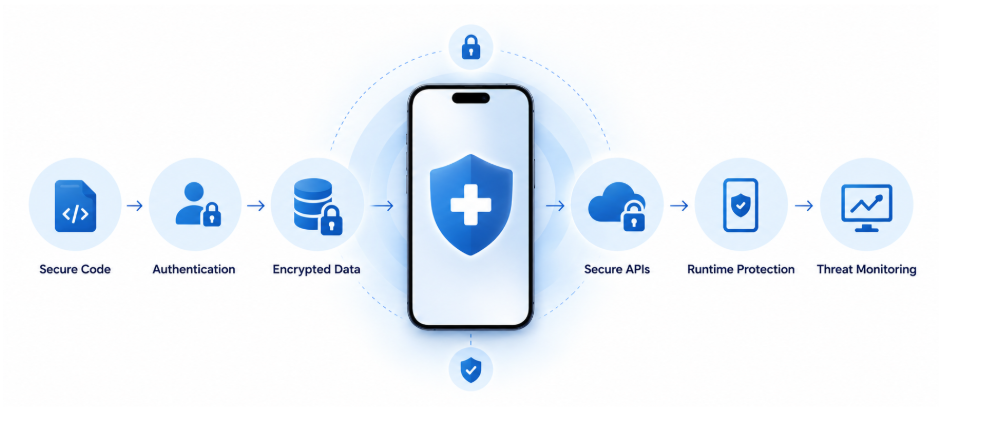
The precept is protection in depth. As an alternative of counting on one safety mechanism, a number of controls defend totally different components of the applying and information move.
Check Safety All through Improvement
Safety testing ought to occur all through improvement fairly than changing into a last pre-launch guidelines.
Automated checks can establish susceptible dependencies and customary coding points because the product evolves. Extra targeted assessments can study authentication, APIs, information storage, entry controls, and potential assault paths.
Discovering these issues earlier additionally reduces the probability of discovering architectural weaknesses instantly earlier than launch, when fixing them turns into significantly costlier.
Monitor What Occurs After Launch
Publishing the applying is just not the tip of its safety lifecycle. Dependencies develop into outdated, new vulnerabilities seem, assault strategies evolve, and product updates create new performance.
Submit-launch safety ought to embrace menace monitoring, dependency updates, vulnerability administration, entry opinions, and clear incident-response procedures. Safety controls must also be reassessed as the applying features customers, integrations, and new forms of information.
Construct Affected person Belief Into the Product
HealthTech safety finally helps one thing broader than compliance: confidence.
Sufferers have to belief that sharing medical data by means of an app won’t unnecessarily expose it. Healthcare organizations want confidence that digital merchandise won’t introduce unacceptable dangers into their programs.
The strongest strategy is subsequently to deal with cybersecurity as a part of the product lifecycle. Safe structure, protected information flows, software integrity, steady testing, and monitoring ought to evolve alongside the app.
(Photograph by Samuel Regan-Asante on Unsplash)