• About Us
  • Privacy Policy
  • Disclaimer
  • Contact Us
AimactGrow
  • Home
  • Technology
  • AI
  • SEO
  • Coding
  • Gaming
  • Cybersecurity
  • Digital marketing
No Result
View All Result
  • Home
  • Technology
  • AI
  • SEO
  • Coding
  • Gaming
  • Cybersecurity
  • Digital marketing
No Result
View All Result
AimactGrow
No Result
View All Result

Excessive-severity WinRAR 0-day exploited for weeks by 2 teams

Admin by Admin
August 12, 2025
Home Technology
Share on FacebookShare on Twitter


BI.ZONE mentioned the Paper Werewolf delivered the exploits in July and August by means of archives hooked up to emails impersonating staff of the All-Russian Analysis Institute. The last word objective was to put in malware that gave Paper Werewolf entry to contaminated techniques.

Whereas the discoveries by ESET and BI.ZONE had been unbiased of one another, it’s unknown if the teams exploiting the vulnerabilities are linked or acquired the information from the identical supply. BI.ZONE speculated that Paper Werewolf might have procured the vulnerabilities in a darkish market crime discussion board.

ESET mentioned the assaults it noticed adopted three execution chains. One chain, utilized in assaults focusing on a particular group, executed a malicious DLL file hidden in an archive utilizing a technique often called COM hijacking that precipitated it to be executed by sure apps corresponding to Microsoft Edge. It regarded like this:
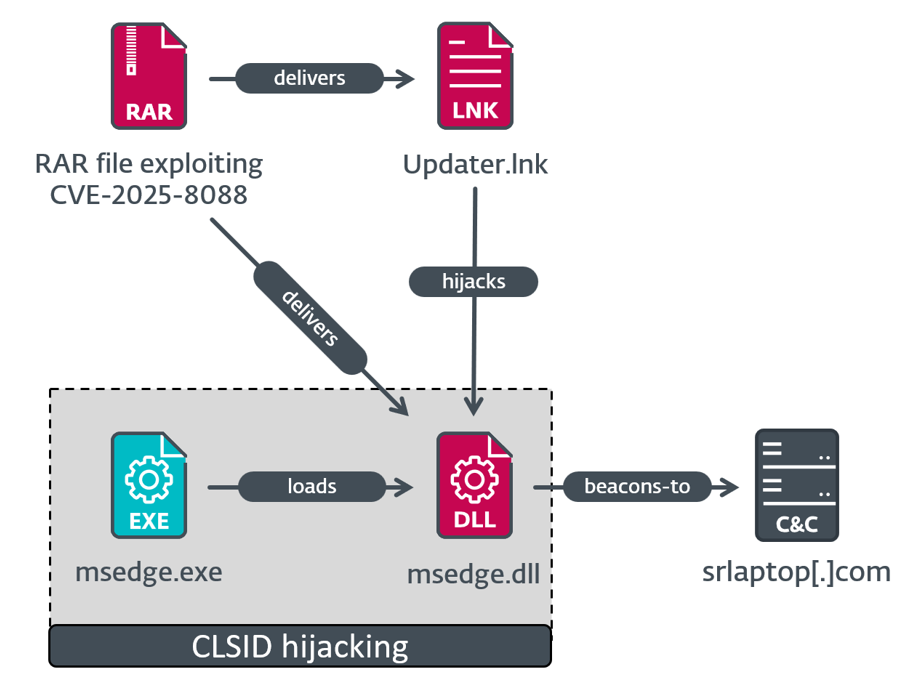


Illustration of the execution chain putting in Mythic Agent.

Credit score:
ESET

Illustration of the execution chain putting in Mythic Agent.


Credit score:

ESET

The DLL file within the archive decrypted embedded shellcode, which went on to retrieve the area identify for the present machine and examine it with a hardcoded worth. When the 2 matched, the shellcode put in a customized occasion of the Mythic Agent exploitation framework.

A second chain ran a malicious Home windows executable to ship a last payload putting in SnipBot, a identified piece of RomCom malware. It blocked some makes an attempt at being forensically analyzed by terminating when opened in an empty digital machine or sandbox, a follow widespread amongst researchers. A 3rd chain made use of two different identified items of RomCom malware, one often called RustyClaw and the opposite as Melting Claw.

WinRAR vulnerabilities have beforehand been exploited to put in malware. One code-execution vulnerability from 2019 got here beneath broad exploitation in 2019 shortly after being patched. In 2023, a WinRAR zero-day was exploited for greater than 4 months earlier than the assaults had been detected.

Moreover its huge person base, WinRAR makes an ideal car for spreading malware as a result of the utility has no automated mechanism for putting in new updates. Meaning customers should actively obtain and set up patches on their very own. What’s extra, ESET mentioned Home windows variations of the command-line utilities UnRAR.dll and the moveable UnRAR supply code are additionally weak. Individuals ought to avoid all WinRAR variations previous to 7.13, which, on the time this put up went dwell, was probably the most present. It has fixes for all identified vulnerabilities, though given the seemingly endless stream of WinRAR zero-days, it isn’t a lot of an assurance.

Tags: 0DayExploitedGroupsHighSeverityWeeksWinRAR
Admin

Admin

Next Post
I Analyzed G2 Opinions to Discover the Finest Buying Software program

I Analyzed G2 Opinions to Discover the Finest Buying Software program

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Recommended.

Meet LangGraph Multi-Agent Swarm: A Python Library for Creating Swarm-Model Multi-Agent Techniques Utilizing LangGraph

Meet LangGraph Multi-Agent Swarm: A Python Library for Creating Swarm-Model Multi-Agent Techniques Utilizing LangGraph

May 16, 2025
Our Favourite Earbuds for Samsung House owners Are On Sale

Our Favourite Earbuds for Samsung House owners Are On Sale

March 10, 2026

Trending.

AI & data-driven Starbucks – Deep Brew

AI & data-driven Starbucks – Deep Brew

May 18, 2026
High LLM Observability and Analysis Platforms in 2026: Langfuse, LangSmith, Braintrust, Arize, and Extra In contrast

High LLM Observability and Analysis Platforms in 2026: Langfuse, LangSmith, Braintrust, Arize, and Extra In contrast

August 9, 2026
The Full Information to EcoGPT

The Full Information to EcoGPT

June 6, 2026
Hasbro Information Breach Uncovered Worker Private Data

Hasbro Information Breach Uncovered Worker Private Data

August 30, 2026
7 Greatest Digital Desktop Infrastructure (VDI) Software program (2026): My Picks

7 Greatest Digital Desktop Infrastructure (VDI) Software program (2026): My Picks

September 9, 2026

AimactGrow

Welcome to AimactGrow, your ultimate source for all things technology! Our mission is to provide insightful, up-to-date content on the latest advancements in technology, coding, gaming, digital marketing, SEO, cybersecurity, and artificial intelligence (AI).

Categories

  • AI
  • Coding
  • Cybersecurity
  • Digital marketing
  • Gaming
  • SEO
  • Technology

Recent News

The Pentagon desires $30 million to construct an AI-powered lie detector

The Pentagon needs $30 million to construct an AI-powered lie detector

September 28, 2026
The promise and peril of utilizing visible AI to review cities | MIT Information

The promise and peril of utilizing visible AI to review cities | MIT Information

September 28, 2026
  • About Us
  • Privacy Policy
  • Disclaimer
  • Contact Us

© 2025 https://blog.aimactgrow.com/ - All Rights Reserved

No Result
View All Result
  • Home
  • Technology
  • AI
  • SEO
  • Coding
  • Gaming
  • Cybersecurity
  • Digital marketing

© 2025 https://blog.aimactgrow.com/ - All Rights Reserved