Cybersecurity researchers have disclosed particulars of a large-scale marketing campaign that has focused uncovered community edge gadgets resembling Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls.
“Artifacts from this investigation additionally point out that operators on this marketing campaign have obtained entry to quite a few organizations worldwide, and have tried to additional compromise some victims, leading to persistent distant entry and knowledge exfiltration,” in keeping with a joint investigation revealed by Group-IB and NyxLab.
The widespread exploitation exercise has been attributed to a menace actor referred to as k0t, who additionally goes by the aliases CryptoFeel, Member19, and QazWsxShop. The cybercriminal actor was first seen within the wild on October 22, 2025.
The menace actor is assessed to share connections with ransomware teams resembling Qilin and The Gents, doubtless working as an preliminary entry dealer or an affiliate. Evaluation of the menace actor’s darkish net exercise reveals a eager curiosity in buying vulnerability exploit code and instruments or premium accounts for metadata search engines like google and yahoo like FOFA and ZoomEye.
The marketing campaign’s victims are world and belong to a broad vary of sectors, given the indiscriminate concentrating on of uncovered community gadgets. A big chunk of compromises are stated to have taken place between February and June 2026, which additionally overlaps with one other credential harvesting marketing campaign codenamed FortiBleed.
Practically 38% of victims are concentrated within the Asia Pacific area, adopted by 31.9% in Latin America, 15.8% in Europe, and 12.7% within the Center East and North Africa.
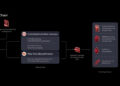
The assault chain performs out as follows –
- Conduct reconnaissance via public scanning instruments like FOFA and ZoomEye to enumerate internet-facing VPN and firewall home equipment, filter candidates by product, and put collectively goal lists of probably weak edge gadgets.
- Try to take advantage of these gadgets through recognized vulnerabilities like CVE-2025-64446 (a path traversal flaw in FortiWeb) and CVE-2026-0257 (an authentication bypass flaw in Palo Alto Networks PAN-OS and Prisma Entry) via bespoke Python scripts named “fortnew.py” and “exploit_2026_0257.py,” or carry out brute-force assaults utilizing frequent username and password mixtures, to acquire preliminary entry.
- Set up a foothold on the targets through an OpenConnect VPN connection.
- Conduct post-exploitation actions and extra credential theft like enumeration of Energetic Listing, SMB, and put in antivirus answer.
- Set up persistence on the host through reliable distant entry instruments like MeshCentral Agent, Atera, Teramind, and AnyDes, in addition to an open-source, adversary-emulation framework referred to as AdaptixC2.
- Exfiltrate harvested knowledge utilizing Rclone into Wasabi S3 buckets and MEGA cloud drives.
The assaults are additionally characterised by way of reliable administrator and pentesting utilities like NetExec, SoftPerfect, Impacket, noPac, Kerbrute, PetitPotam, and Mimikatz to burrow deeper into victims’ company environments.
“k0t seems to pick potential targets by enumerating uncovered community home equipment at scale moderately than researching particular person organizations,” Group-IB and NyxLab researchers stated. “His acknowledged geographic priorities start with the US and Canada, adopted by European international locations and chosen APAC markets.”
“The product and placement of an uncovered machine subsequently seem to matter greater than the business of the group working it, in step with the broad vary of victims noticed on this marketing campaign.”
k0t’s hyperlinks to Qilin and The Gents stem from the truth that many victims of the marketing campaign had been additionally later listed by the ransomware teams on their knowledge leak websites. Nonetheless, the precise nature of the connection between the menace and these gangs is unclear.
What’s extra, Group-IB and NyxLab stated they discovered a “negligible overlap” in compromised knowledge between this exercise and FortBleed. Greater than 70,000 uncovered credentials related to community gadgets and LDAP dumps have been recognized in reference to the marketing campaign.
“This aligns with studies that many operators are more likely to be concerned within the FortiBleed exercise cluster, suggesting that this can be a separate dataset, operator subset, or associated entry operation throughout the broader FortiBleed-related exercise,” the researchers stated. “Organisations are suggested to behave on making certain that any vulnerabilities talked about on this report are appropriately remedied.”