Bitdefender researchers uncover Midnight Mimosa malware preinstalled on low-cost MediaTek Android telephones enabling advert fraud and proxyware exercise.
Cybersecurity researchers at Bitdefender have recognized a marketing campaign dubbed Midnight Mimosa affecting a number of low-cost Android telephone manufacturers constructed on MediaTek platforms, permitting operators to put in apps, grant permissions and cargo code with out the proprietor’s consent.
The an infection occurs under the traditional app-installation layer. In its analysis shared with Hackread.com, Bitdefender notes that “each user-facing protection had already been bypassed” by the point the telephone was switched on.
Malware Hidden as a System Element
The malware hides in system packages reminiscent of com.android.system.lite and com.android.sys.prot. As a result of they run with Android system privileges, customers can not usually take away them.
A local library known as libeasy.so decrypts one other element and connects to api.weatherlive.world to obtain extra code. The malware can then set up or take away apps with out asking the consumer and provides these apps extra permissions.
Bitdefender additionally discovered Accessibility and Notification Entry being turned on and off routinely, however didn’t see the malware use both characteristic for malicious exercise.
The principle exercise noticed was not knowledge theft however monetization. The malware makes use of advert fraud and proxyware, whereas its privileged entry offers operators a solution to change or broaden the payloads later.
For context, proxyware turns a tool’s web connection right into a relay for different visitors, usually making that visitors seem to come back from the contaminated consumer’s IP deal with.
Play Defend Evasion and Hidden Advert Fraud
Earlier than putting in a payload, the malware briefly disables the Google Play Retailer package deal, com.android.merchandising, and restores it afterward. Bitdefender assessed that this may increasingly create a window for payload set up whereas avoiding regular Play Defend checks.
The malware may make a sideloaded app seem to have been put in from Google Play, though it lacks the cryptographic “frosting” marker discovered on real Play apps. Bitdefender discovered payloads reminiscent of com.cellular.applock.en, which makes use of EnLoaderLib v1.0.6 and connects to a proxy community over TCP port 6000. One other payload, com.cellular.applock.wt, accommodates an ad-fraud module.
The malware additionally installs apps for capabilities reminiscent of climate, AppLock, notes and OCR. These apps use reputable promoting SDKs, however the malware can run advertisements within the background and generate pretend impressions and clicks with out the consumer seeing them.
Hundreds of Gadgets in 150+ Nations
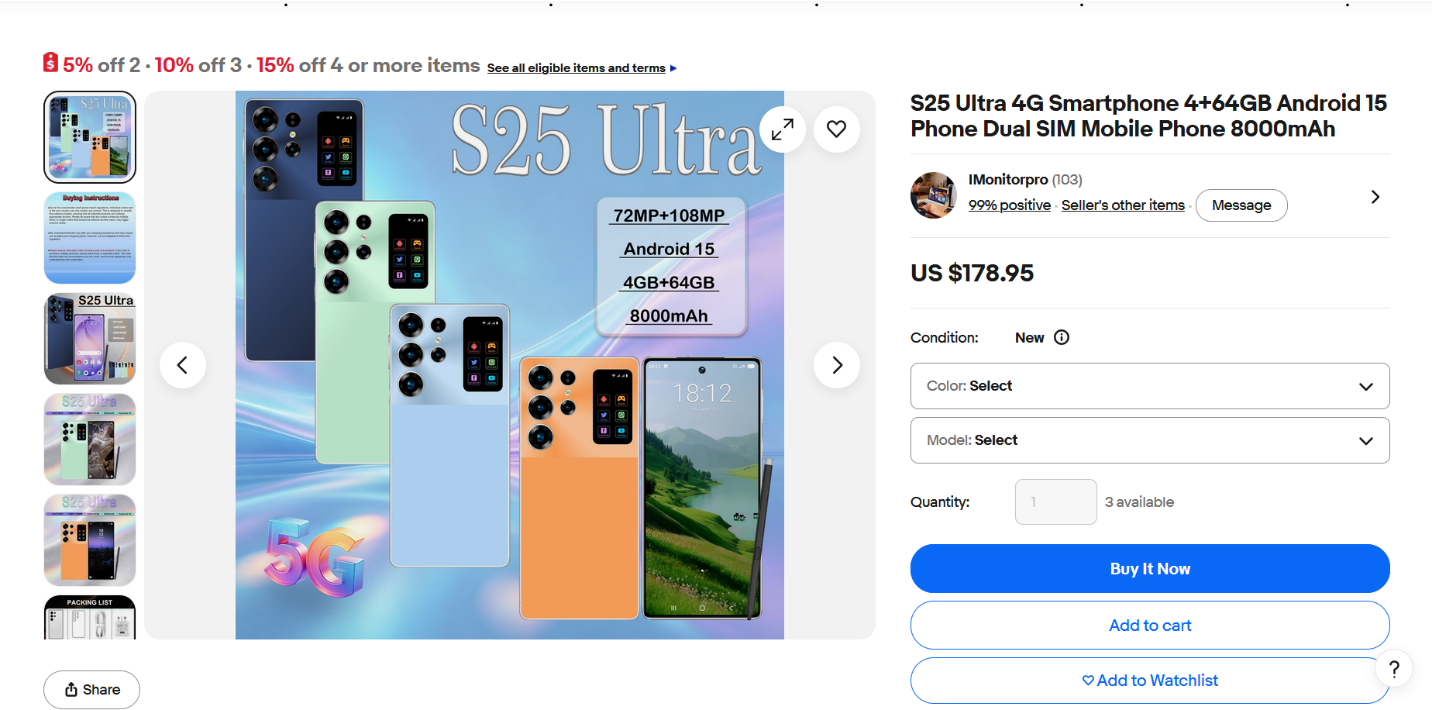
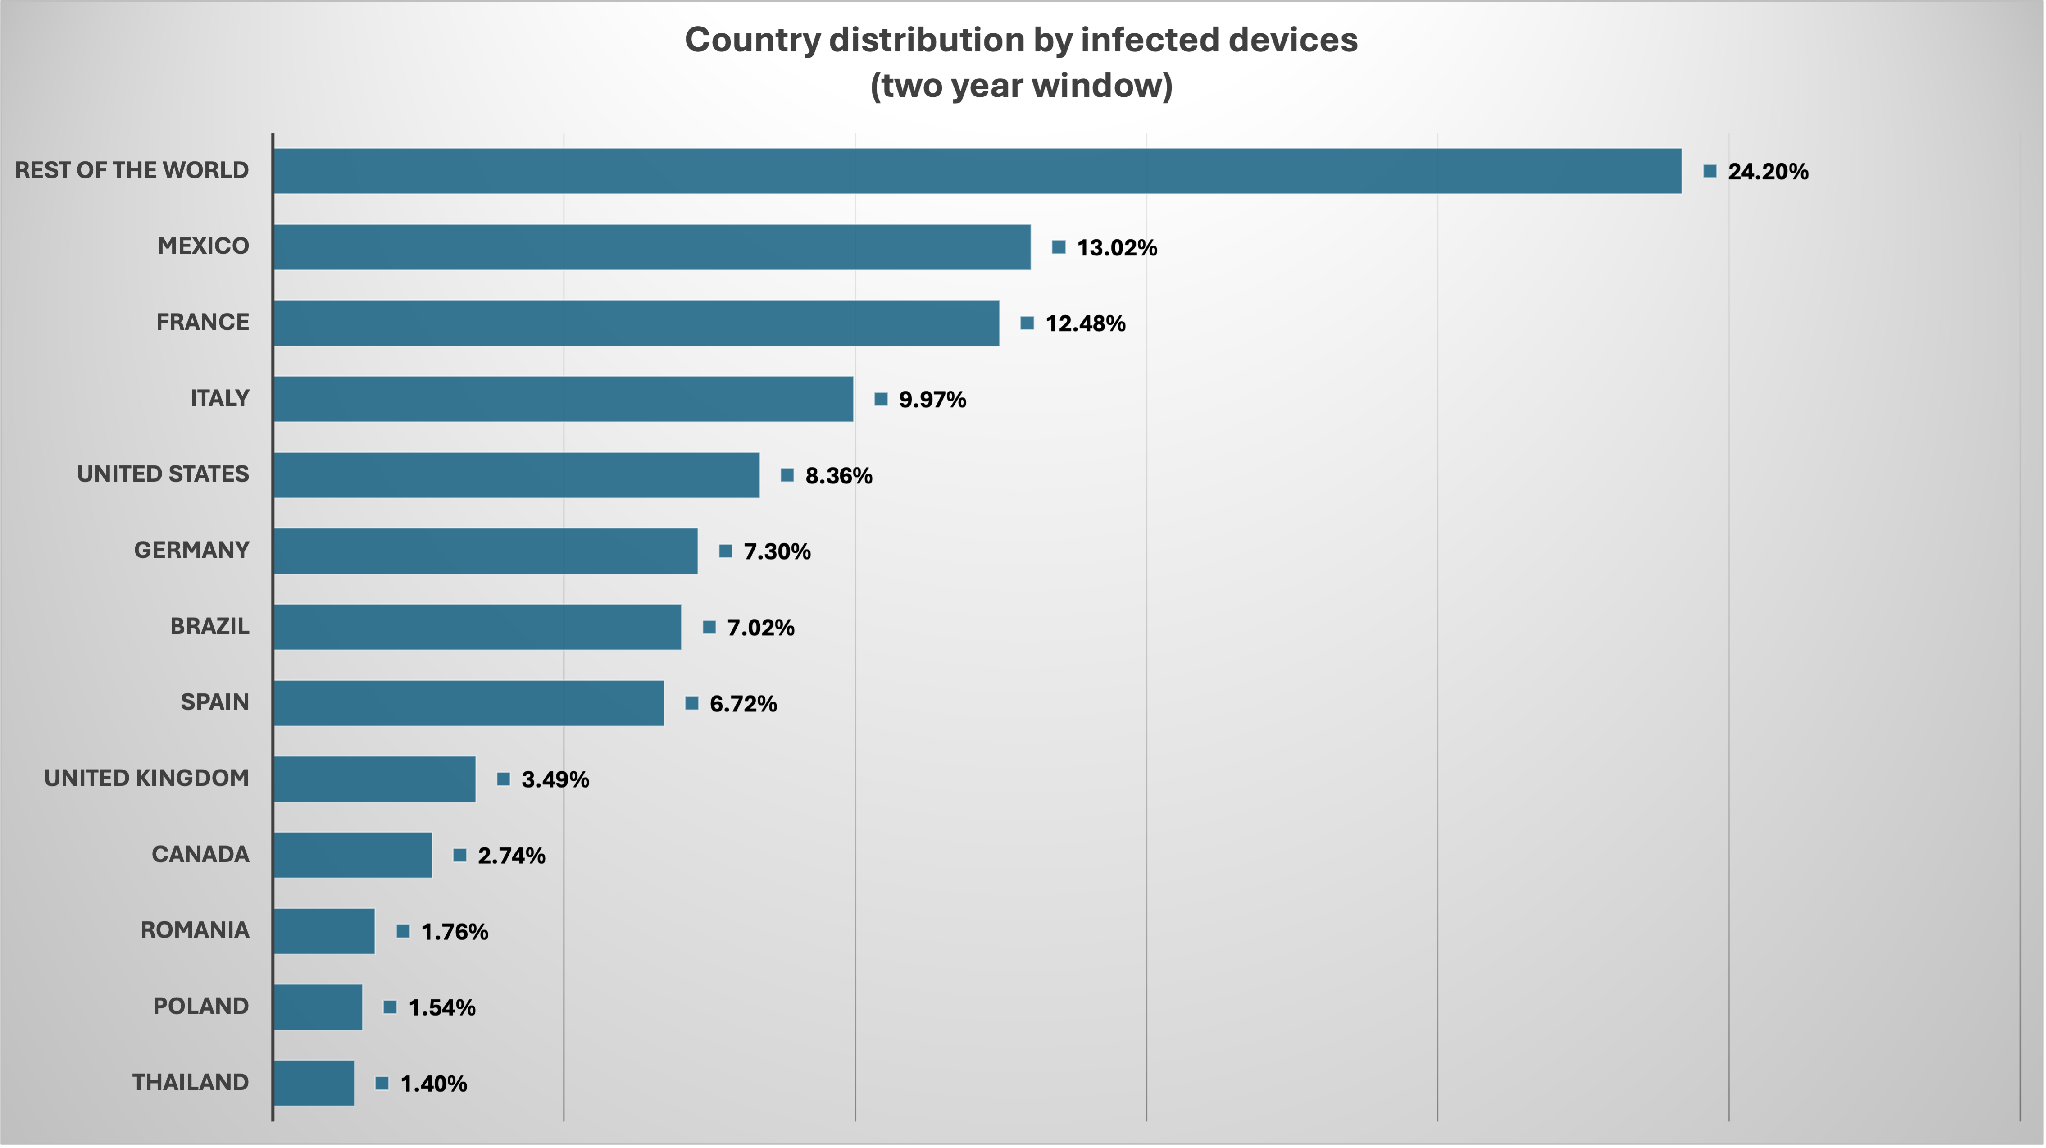
Bitdefender noticed 1000’s of contaminated units in additional than 150 international locations. Affected {hardware} included counterfeit telephones reporting names reminiscent of “S25 Extremely” and “i17 Professional Max,” together with price range fashions together with the Doogee S200 X and Cubot KINGKONG X.
The identical adfraud code was additionally present in 13 Google Play apps, exhibiting that the operation was not restricted to preinstalled firmware.
A platform certificates utilized by com.android.system.lite was related to Shenzhen Zediel Co., Ltd. Nevertheless, Bitdefender stated this doesn’t show the corporate inserted or knowingly distributed the malware. The purpose the place the malware entered the provision chain stays unknown.
For consumers, the issue is {that a} regular manufacturing facility reset or uninstall will not be sufficient. Midnight Mimosa sits in system-level firmware, so affected units might require trusted firmware substitute, vendor remediation or substitute of the telephone itself.
(Featured Picture by Andrey Matveev on Pexels)