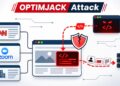
OPTIMJACK, a malicious JavaScript supply marketing campaign noticed on CNN, Zoom, and different distinguished web sites via a third-party script layer.
Detected on November 16, the exercise reportedly concerned code designed to exchange cryptocurrency pockets addresses, gather cost particulars, and selectively ship further content material to iPhone and iPad browser profiles.
Profitable monetary theft and machine exploitation stay unconfirmed.
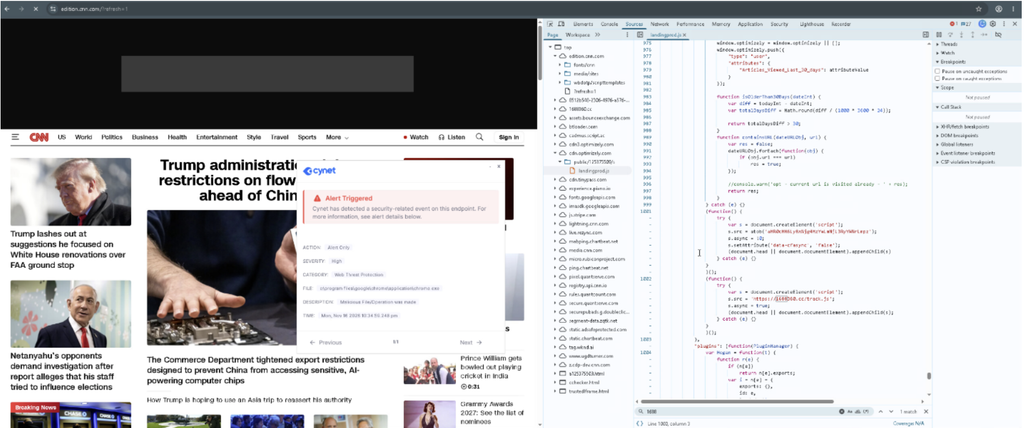
The investigation started when Cynet endpoint detection and response alerts flagged browser connections to 1688360[.]cc.
CyOps analysts correlated these alerts with searching exercise, inspected related assets and traced the loader to JavaScript served from cdn.optimizely[.]com.
Researchers assessed this third-party script layer because the seemingly injection level, with out establishing how the insertion occurred.
Browser captures confirmed a useful resource loaded on version.cnn[.]com appending 1688360[.]cc/observe.js to the web page.
On Zoom, investigators recognized the identical insertion code inside an Optimizely-hosted script loaded alongside Zoom assets. Additionally they captured the code whereas searching Optimizely’s personal web site.
The investigation moreover listed Salesforce, Fox Information and Fox Sports activities, however the report lacked request-and-response captures wanted to confirm these observations.
Their proof standing due to this fact differs from the captured CNN, Zoom and Optimizely circumstances. Supply via these pages doesn’t set up that the organizations’ inner techniques have been compromised.
Potential entry paths embody compromised account entry, tag configuration or an integration, however none has been confirmed.
Cynet explicitly cautioned towards decoding the findings as proof that Optimizely itself was breached.
Cynet Researchers documented, 1688360[.]cc/script.js and 1688360[.]cc/observe.js. Obtainable proof doesn’t set up whether or not these assets returned an identical payloads or represented completely different revisions.
Analyst evaluate described wallet-replacement performance meant to substitute cryptocurrency addresses in web page content material or clipboard interactions.
OPTIMJACK Assault
Cost-form assortment logic reportedly sought card particulars for transmission to an exterior vacation spot. Neither functionality, by itself, demonstrates a accomplished fraudulent switch or profitable assortment from a customer.
Different reported features included amassing accessible cookies and web page information, alongside utilizing html2canvas to render web page content material.
These capabilities stay constrained by browser safety boundaries: the proof doesn’t set up entry to HttpOnly cookies, unrelated origins, different tabs or unrestricted desktop screenshots.
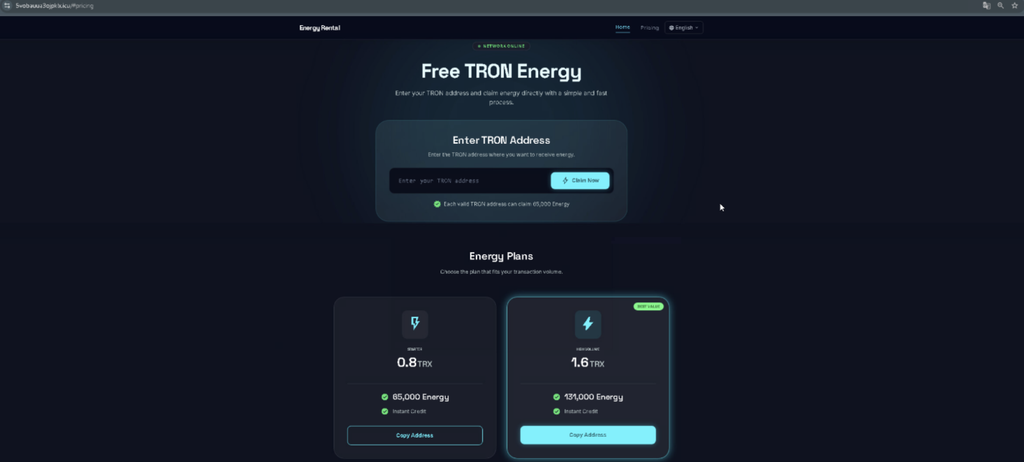
Utilizing a Safari-like iPhone profile and machine emulation, researchers retrieved boot.js from infrastructure together with 5vobauua3ojpklx[.]icu and, throughout later retrievals, eil786npto9u5bq[.]icu.
The loader reportedly checked iOS variations and chosen subsequent content material via an iframe, together with JIUJIU888/weifile.html.
This helps conditional payload supply, not profitable compromise of a bodily Apple machine.
No affected iOS model vary, exploit CVE or threat-actor attribution has been established. Root trigger and the marketing campaign’s full impression stay below investigation.
Organizations ought to evaluate third-party scripts and tag configurations, then hunt historic DNS, proxy and browser telemetry for the reported indicators.
Responders ought to distinguish blocked connections from delivered responses, executed JavaScript and confirmed outbound information transfers.
Preserving timestamps, headers, response our bodies, initiator chains and pattern hashes will assist reconstruct publicity.
Validated malicious locations needs to be blocked via accessible DNS, net gateway and endpoint controls, with enforcement examined.
Broad blocking of professional web sites, Optimizely’s CDN or shared supply addresses dangers collateral disruption.
A later 30-minute recheck didn’t reproduce the scripts on examined websites, however that commentary doesn’t set up common removing.
Assessments ought to prioritize demonstrated execution and visitor-data publicity relatively than equating each alert with an infection or confirmed compromise of the underlying web site or service supplier.
Indicators of compromise
| Indicator | Sort | Position and proof standing |
| 1688360[.]cc | Area | Main malicious vacation spot in domain-filtering detections. |
| 1688360[.]cc/script.js | URL path | Useful resource reported in preliminary analyst narrative. |
| 1688360[.]cc/observe.js | URL path | Useful resource reported in subsequent delivery-chain testing. |
Observe: IP addresses and domains are deliberately defanged (e.g., [.]) to forestall unintentional decision or hyperlinking. Re-fang solely inside managed risk intelligence platforms resembling MISP, VirusTotal, or your SIEM.
Stops Cyber threats earlier than impression with 21 min quicker MTTR. Combine ANYRUN’s Sandbox in your SOC.