An extended-running pay-per-install (PPI) operation that used YouTube gaming channels and Website positioning-poisoned software program downloads to distribute malware at scale.
The cluster, tracked as CL-CRI-1171, is linked to greater than 10,000 distinct samples of a customized loader referred to as OfferLoader, indicating a distribution pipeline far bigger than the person intrusions initially noticed.
Quite than counting on a single superior implant or an overtly focused intrusion chain, the operators used trojanized installers, disposable domains, browser-based filtering and affiliate monitoring to selectively ship payloads to victims whereas avoiding automated evaluation methods.
Unit 42 mentioned the exercise had operated for at the least two years and functioned as an infection-as-a-service platform.
In a PPI mannequin, entry to compromised methods may be bought to a number of downstream actors, permitting one benign-looking installer to deploy unrelated malware households with separate command-and-control infrastructure, goals and monetization fashions.
Researchers recognized at the least 11 YouTube channels related to the operation.
The channels collectively had tons of of 1000’s of subscribers and hundreds of thousands of views, publishing apparently respectable content material centered on gaming efficiency, frame-rate enhancements, crash fixes and game-setting optimizations.
The movies delivered real gaming recommendation, however descriptions and linked pages directed customers to malicious “optimization instruments,” cheats, utilities or software program packages.
The hyperlinks usually handed by means of middleman Blogspot pages earlier than routing customers to the identical PPI gate infrastructure utilized by the marketing campaign’s Website positioning-poisoning operation.
YouTube was notified of the channels and terminated them, in response to Unit 42.
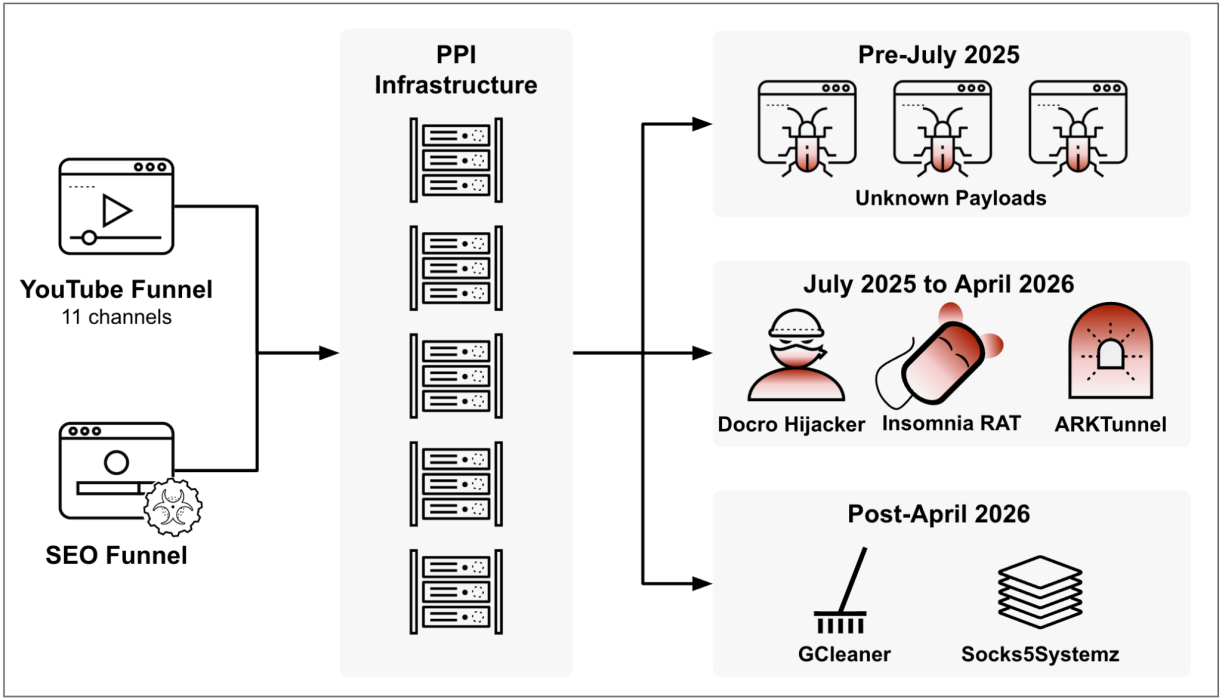
A parallel Website positioning-poisoning funnel focused customers looking for respectable instruments and software program. In investigated incidents, victims downloaded trojanized variations of a Bluetooth driver and the disk-usage utility WinDirStat.
The faux obtain pages used file-hosting lures and deceptive virus-scan animations earlier than offering ZIP archives containing malicious installers.
10,000+ Malware Loaders
Unit 42 mentioned in a report shared with GBhackers, the marketing campaign demonstrates how malware supply infrastructure can stay largely unnoticed by showing routine.
The assault chain used a gating mechanism to filter visitors. Tracker URLs included a Base64-encoded click_id parameter containing telemetry such because the customer’s working system, browser, referring area, search time period and public IP handle.
Legitimate sufferer fingerprints have been forwarded to the malware obtain, whereas crawlers, safety scanners and researchers have been reportedly served damaged hyperlinks or decoy pages impersonating respectable WinRAR downloads.
The core supply part, OfferLoader, is embedded in trojanized Inno Setup installers.
Its goal is to not retain long-term entry itself, however to behave as a disposable deployment framework that launches separate malware “affords” provided by PPI clients.
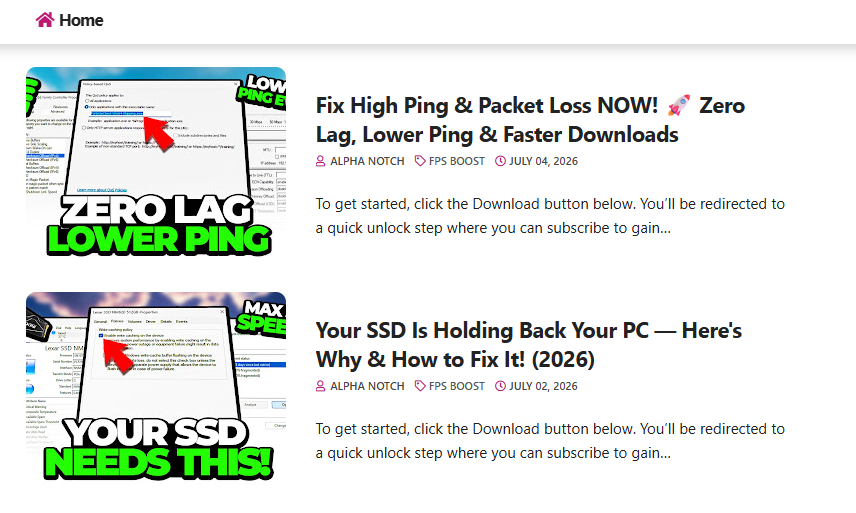
In a single noticed an infection chain, an obvious windirstat.exe installer unpacked a short lived part that contacted a monitoring server.
The server returned both “no,” which halted execution, or “okay,” which triggered the deployment of a number of baby processes.
These processes delivered separate malware payloads, enabling a number of impartial prison operations to coexist on the identical contaminated endpoint.
Unit 42 traced greater than 200 rotating infrastructure domains utilizing a particular two-word naming conference throughout .xyz, .cfd, .area and .data top-level domains.
The rotational infrastructure, shared loader and overlapping supply paths tied the YouTube and Website positioning campaigns to a single sustained cluster.
The April 2026 incidents delivered three malware households: Insomnia RAT, ARKTunnel and Docro Hijacker.
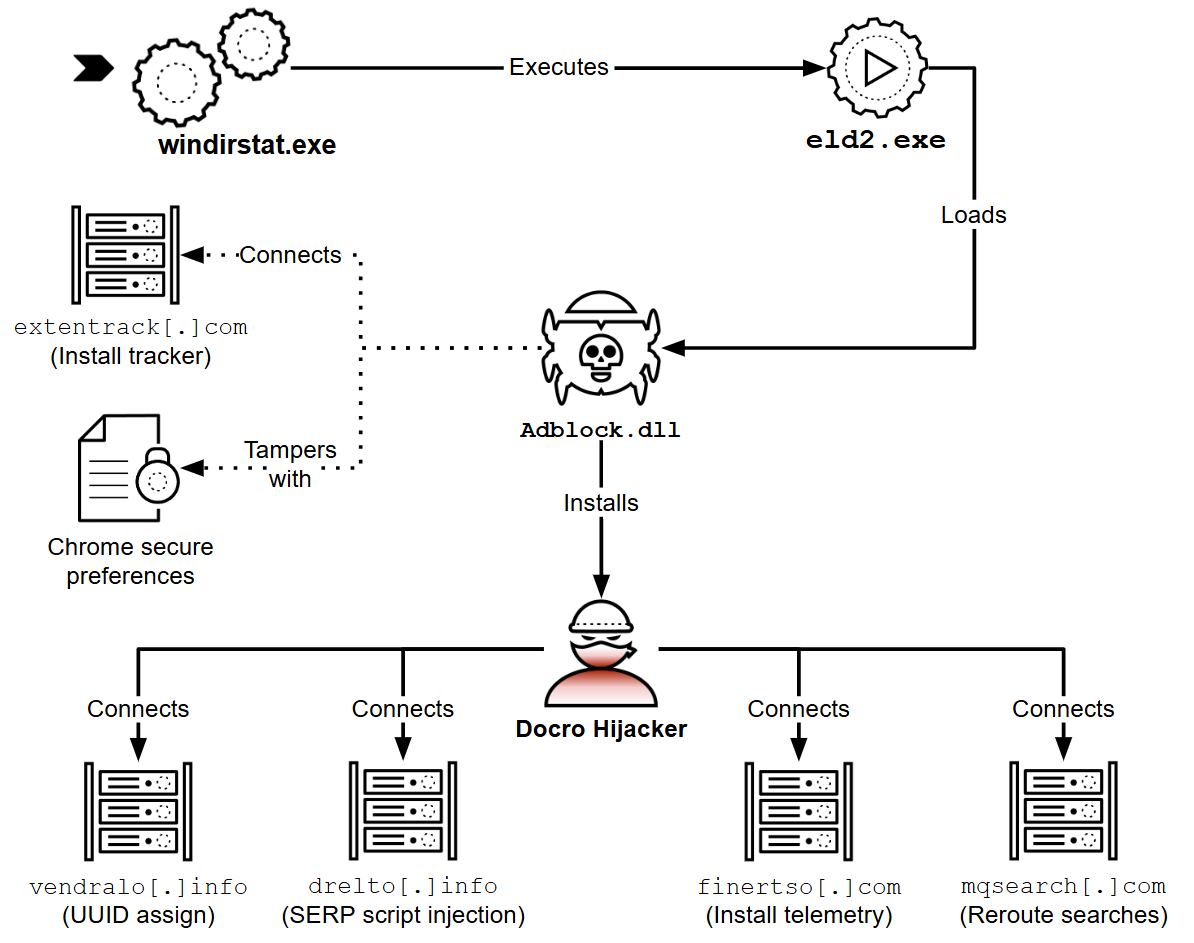
A later an infection in June reportedly delivered totally different payloads, GCleaner and Socks5Systemz, underscoring that OfferLoader’s payload set is modular and may change between associates or campaigns.
Insomnia RAT combines Node.js and Python backdoors, offering redundant entry paths.
The installer reportedly disables Microsoft Defender protections, provides C: as an exclusion and deploys runtime environments required to execute the implants.
It creates scheduled duties masquerading as Home windows parts, together with Maps Efficiency Activity and OOBETaskScheduler, then communicates with command servers utilizing the user-agent string insomnia/2023.4.0 Home windows.
ARKTunnel is a beforehand unreported WebSocket-based tunneling RAT that makes use of least-significant-bit steganography to extract its payload archive from a bitmap picture.
The implant helps TCP and UDP tunneling, file execution and service-based persistence, whereas utilizing rotating faux company identities equivalent to EarthKark and TamarkLark in its metadata.
Docro Hijacker targets Google Chrome. It modifies Chrome Safe Preferences by bypassing the browser’s HMAC-SHA256 integrity mechanism, enabling pressured search-provider modifications and set up of a Manifest V3 extension.
The extension can inject promoting, rewrite affiliate hyperlinks and redirect search visitors by means of attacker-controlled infrastructure.
The marketing campaign highlights the chance posed by “low-priority” detections involving adware-like loaders, suspicious installers and doubtlessly undesirable software program.
Safety groups ought to examine unsigned installers from search outcomes, monitor just lately registered domains, examine scheduled duties created after archive extraction, and detect browser desire modifications or surprising Chrome extensions.
Organizations must also block downloads of pirated software program, sport cheats and unofficial optimization instruments, particularly from hyperlinks promoted by means of video descriptions or search outcomes.
The marketing campaign’s power just isn’t a single exploit, however a scalable and selective distribution system constructed to make compromise look extraordinary.
IOCs
| SHA-256 | File Identify | File Kind | Description |
|---|---|---|---|
7f792c45de1e28fd42ac44c9444f157a2161742d130bac336c0e991aabbb112c |
windirstat.exe |
PE32 executable; Inno Setup 6.7.1 installer | OfferLoader-trojanized WinDirStat installer distributed by means of an Website positioning-poisoning marketing campaign. |
fc485882626512e7ff82a1d7cd8e8fb3e9751b026d97e682d6908aefff1f2d73 |
windirstat.tmp |
PE32 executable; unpacked Inno Setup stage | Unpacked WinDirStat set up stage extracted from the trojanized installer. |
Notice: IP addresses and domains are deliberately defanged (e.g., [.]) to stop unintentional decision or hyperlinking. Re-fang solely inside managed menace intelligence platforms equivalent to MISP, VirusTotal, or your SIEM.
★ Be taught 7 Metric-Gated AI SOC Deployment Phases – Obtain Free AI SOC Deployment Playbook 2026.