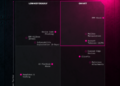
Huntress has printed the Huntress Tragic Quadrant, a rating of the cyber ways its Safety Operations Heart (SOC) is detecting and shutting down most frequently, plotted towards what the corporate calls “pucker issue”: how shut every tactic places an organisation to main harm as soon as it lands.
Constructed on telemetry from greater than 5 million endpoints and 15 million identities throughout almost 300,000 organisations, the report contains a number of beforehand unpublished findings. Chief amongst them: in Q1 2026, 45% of endpoint-related incidents Huntress investigated concerned abuse of distant monitoring and administration (RMM) instruments.
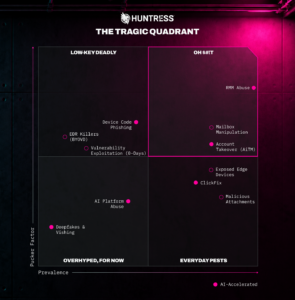
RMM abuse jumped 277% 12 months over 12 months in 2025 and is now the one commonest risk class Huntress sees on endpoints. As a result of the instruments are reputable and already trusted, attacker exercise can seem like extraordinary administration. In a single case, a faux service settlement put in Tiflux earlier than quietly stacking UltraVNC, Splashtop and ScreenConnect on the identical gadget, giving the attacker a number of methods again in from a single phishing click on.
“Why would you spend the cycles to develop or construct from scratch when you should use a reputable device that you would be able to simply pull off the shelf?” – Jamie Levy, Senior Director, Adversary Techniques, Huntress
Identification assaults sit alongside RMM within the hazard zone
RMM abuse shares the report’s top-right “Oh $#!T” nook with two identity-based ways. Mailbox manipulation, the place an adversary with inbox entry marks messages as learn, deletes inbound mail and redirects emails into obscure folders comparable to RSS Feeds or Archive, accounted for twenty-four.6% of suspicious ITDR detection indicators thus far in 2026. Adversary-in-the-middle (AiTM) account takeover, which steals session tokens in transit and sidesteps MFA, made up 18.9% of identity-based threats in 2025.
Preliminary entry stays stubbornly easy. Roughly 70% of the energetic intrusions caught by the Huntress SOC begin with adversaries authenticating by VPN entry, usually with legitimate credentials and no second issue.
“Something you expose to the web will get hammered. RDP sits on the high of that record.” – Dray Agha, Senior Supervisor, Tactical Response, Huntress
Low prevalence, excessive severity
The report additionally flags ways that seem much less usually however escalate shortly. ClickFix, the faux CAPTCHA approach that tips customers into pasting malicious instructions into the Home windows Run field, made up simply 2.2% of suspicious EDR detection indicators, but almost 99% of these indicators had been excessive severity. ClickFix was additionally behind 53.2% of all malware loader exercise in 2025.
Gadget code phishing rose 1,380% when evaluating July to December 2025 with January to April 2026. A single phishing-as-a-service package, EvilTokens, hit 344 organisations throughout 5 international locations in 16 days utilizing solely reputable infrastructure. In the meantime, bring-your-own-vulnerable-driver (BYOVD) EDR killers stay uncommon however decisive, with 23.8% of driver abuse in 2025 traced to a single device, Throttlestop/RWDriver. In a single incident, an attacker entered by stolen SonicWall VPN credentials and loaded a 15-year-old revoked EnCase driver to kill 59 safety processes from kernel mode.
Vulnerability exploitation additionally lands within the “Low-key lethal” nook, with Huntress observing attackers weaponise flaws in Wing FTP Server, WSUS and Gladinet CentreStack and Triofox inside days of disclosure.
“The remediation window that defenders depend on, the hole between ‘patch obtainable’ and ‘actively exploited at scale,’ is already measured in hours and days for essentially the most crucial vulnerabilities, and that hole will proceed to slender.” – Muhammad Yahya Patel, vCISO and cybersecurity advisor for EMEA, Huntress
Huntress recommends defenders begin within the top-right nook: set up which RMM instruments are authorized and alert on anything, baseline regular inbox guidelines, shorten session lifetimes and require re-authentication from new units or areas, and guarantee no distant entry path depends on a password alone.
On 8 October, Huntress CEO Kyle Hanslovan will run a stay hacking demonstration of methods from the Tragic Quadrant, exhibiting how shortly they transfer from preliminary entry to impression. You may register right here: https://www.huntress.com/upcoming-livestreams/live-hack-see-the-threats-that-topped-our-list
The put up RMM abuse behind 45% of endpoint incidents as Huntress publishes inaugural Tragic Quadrant appeared first on IT Safety Guru.