A big-scale SMS phishing marketing campaign is impersonating T-Cell and warning recipients that their “rewards factors” are about to run out, utilizing fabricated balances, pressing deadlines, and lookalike redemption hyperlinks to steal delicate info.
Safety researchers have tracked the operation since early Might 2026 and proceed to watch new message variants regardless of a decline from its peak exercise.
One generally noticed lure tells recipients that their T-Cell Rewards account comprises 18,400 factors that will likely be eliminated except redeemed by an imminent expiry date.
The messages instruct targets to go to URLs resembling t-mobile.[random-string].prime/pay, or to make use of an alleged Rewards & Advantages part within the T-Cell app.
The notices are fraudulent. Quite than directing subscribers to a official T-Cell property, the attackers rotate via short-lived domains constructed to visually affiliate themselves with the service.
Malwarebytes recognized at the least 81 domains used throughout 4 months, with examples together with t-mobile.biktpw[.]prime, t-mobile.cugbjl[.]prime, and t-mobile.gdikxv[.]prime.
The quickly altering infrastructure complicates easy domain-based blocking whereas preserving a recognizable naming sample for defenders.
The rip-off messages are designed to really feel personalised with out utilizing real account information.
They embody a precise-looking level stability, a date set to the day of supply or the next day, and formal language suggesting that the expiration is ruled by program coverage.
But the greetings are normally generic: “Expensive Buyer,” “Expensive T-Cell Buyer,” “Expensive Valued Buyer,” or “T-Cell Person.”
That inconsistency is a crucial detection sign. Professional account notifications usually present verifiable context via authenticated channels, whereas phishing messages incessantly use generic salutations and push the recipient away from the official software or web site.
Researchers discovered greater than 1,000 intently associated message templates with a semantic similarity rating of at the least 0.60.
Malwarebytes Researchers mentioned that, the smishing marketing campaign depends on a well-known however efficient social-engineering components: current a helpful asset, declare it’ll disappear inside hours or days, and supply a single-click path to “save” it.
T-Cell Phishing Rip-off
The 199 closest examples scored 0.95 or increased, indicating that operators are producing high-volume variations of a steady template somewhat than independently crafted campaigns.
The edits are principally beauty: salutation, topic line, claimed stability, expiry date, and wording comparable to “reminder,” “alert,” or “vital replace.”
The core name to motion stays unchanged redeem allegedly expiring factors via a hyperlink instantly.
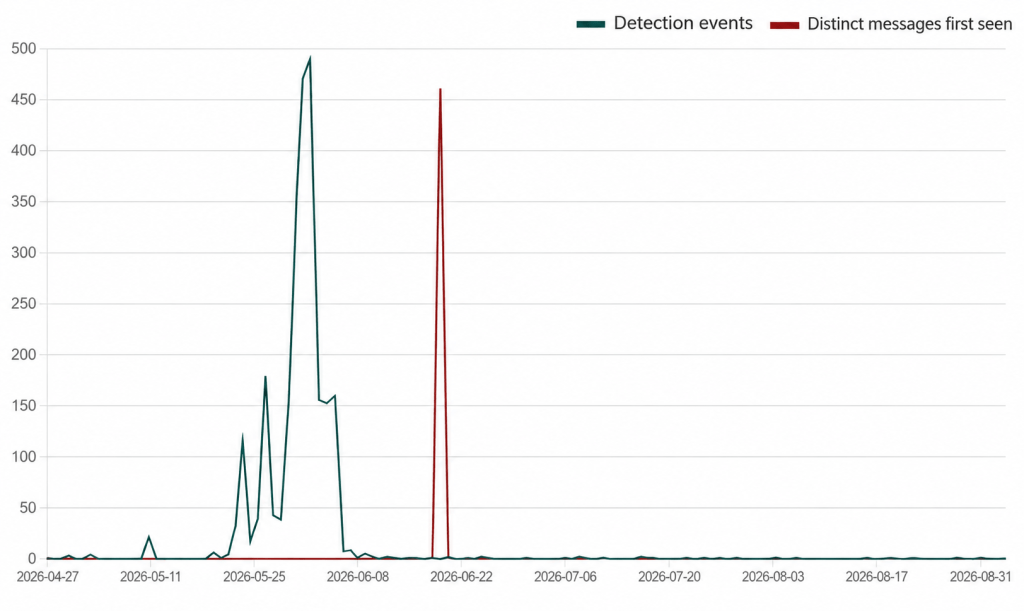
The marketing campaign started with comparatively low detection quantity earlier than producing two substantial exercise spikes.
Malwarebytes telemetry distinguishes between beforehand noticed variants and message templates seen for the primary time, exhibiting that the operators regularly refreshed lure textual content whereas sustaining the identical underlying narrative and infrastructure strategy.
This sample illustrates why static key phrase filtering alone is inadequate for SMS safety. Attackers can swap dates, reward balances, URL hostnames, and message wording at little value.
Efficient detection due to this fact requires behavioral and semantic evaluation, URL popularity checks, lookalike-domain detection, and real-time cell protections.
The marketing campaign’s use of the .prime top-level area can be a notable indicator. Whereas no TLD is inherently malicious, an unsolicited message claiming to signify T-Cell shouldn’t route customers to a website that’s unrelated to t-mobile.com.
Customers ought to deal with any reward-redemption hyperlink pointing to an unfamiliar or randomly generated area as hostile till independently verified.
The rapid danger is credential harvesting. A sufferer who follows the hyperlink could encounter a counterfeit T-Cell login web page, a kind requesting private particulars, or a cost web page claiming {that a} card is required to course of the redemption.
Attackers may additionally request one-time verification codes, which might allow account takeover even the place multifactor authentication is enabled.
Recipients shouldn’t enter account credentials, payment-card particulars, personally identifiable info, or SMS verification codes after following hyperlinks in unsolicited messages.
The most secure validation methodology is to open the official T-Cell app immediately or manually enter the service’s recognized web site in a browser, then examine account notifications from inside the authenticated session.
Subscribers who obtain a suspicious rewards-expiration discover ought to keep away from replying, clicking, or calling any quantity supplied within the message.
They need to report the textual content via their system’s spam-reporting operate and, the place supported, ahead it to 7726, the usual U.S. quick code for reporting spam texts. Experiences will also be submitted to the FTC via its fraud-reporting channel.
Customers who already submitted credentials ought to instantly reset their T-Cell password via official channels, assessment account and restoration settings, test for unauthorized adjustments, and call their monetary establishment if card particulars had been entered.
The central rule stays easy: official rewards or account alerts will be verified independently contained in the official app or on the real T-Cell web site by no means via an unsolicited text-message hyperlink.
IOCs
| # | Domains |
|---|---|
| 1 | t-mobile.biktpw[.]prime |
| 2 | t-mobile.cugbjl[.]prime |
| 3 | t-mobile.cymfjd[.]prime |
| 4 | t-mobile.gdikxv[.]prime |
| 5 | t-mobile.hdzcnb[.]prime |
| 6 | t-mobile.koxetp[.]prime |
| 7 | t-mobile.nxdcfp[.]prime |
| 8 | t-mobile.pkrbai[.]prime |
Notice: IP addresses and domains are deliberately defanged (e.g., [.]) to stop unintentional decision or hyperlinking. Re-fang solely inside managed menace intelligence platforms comparable to MISP, VirusTotal, or your SIEM.
Reduce each SOC alert investigation by 21 min. Energy your SOC with prompt IOC context for rapid response: Combine TI Lookup in your SOC