A suspected key member of ShinyHunters identified on-line as “Rey” has been detained in Jordan and is reportedly cooperating with the FBI, days after the hacking group claimed certainly one of its most delicate breaches but: the theft of personnel info belonging to FBI workers.
Jordanian authorities detained Saif al-Din Khader this week, in accordance with three individuals accustomed to the case who spoke to Reuters. Two sources mentioned authorities took him into custody Tuesday, and he’s now serving to the FBI and different legislation enforcement companies determine and find different hackers linked to the group.
The precise circumstances of Khader’s detention and his present location haven’t been disclosed. The FBI declined to substantiate a selected arrest overseas, however mentioned it’s persevering with to analyze the current incident allegedly involving ShinyHunters and has already labored with worldwide companions to arrest a number of suspects.
Who Is Rey?
Khader’s alleged id has been public for nearly a yr. In November 2025, cybersecurity journalist Brian Krebs recognized Rey as a teen from Amman, Jordan, allegedly concerned with Scattered LAPSUS$ Hunters, an alliance related to ShinyHunters, Scattered Spider and LAPSUS$. Khader reportedly spoke with Krebs over Sign and claimed on the time that he was leaving information theft and extortion behind.
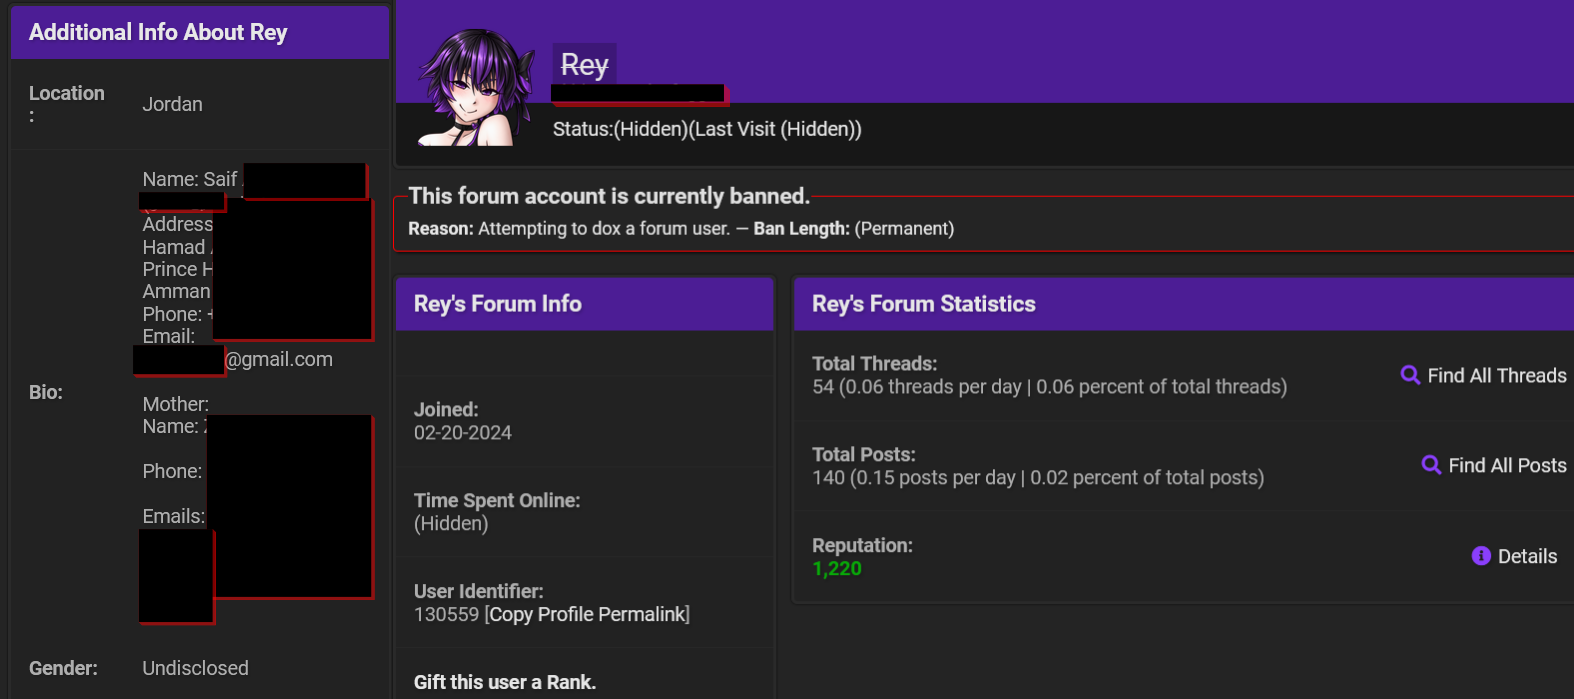
Hackread.com reported on the identification on the time, noting that Rey disputed a few of the claims linking him to the group. Newer reporting, nevertheless, positioned him a lot nearer to ShinyHunters’ operations. Sources cited by Krebs final month described Rey as having taken management of the ShinyHunters model amid an inner dispute involving Dutch hacker Pepijn van der Stap, also called Umbreon.
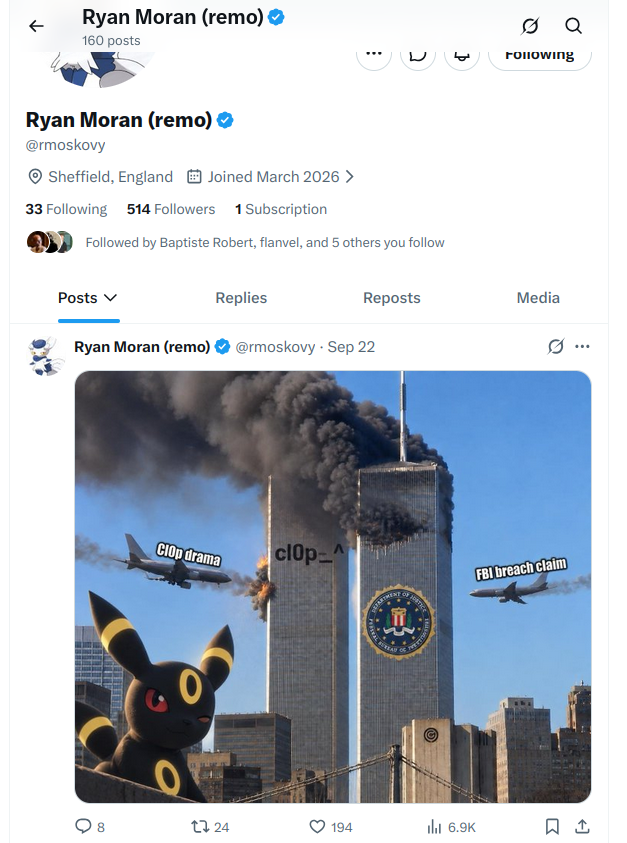
Rey had additionally been publicly taunting the FBI and rival cybercrime teams. In keeping with Krebs’ report, shortly after the FBI breach grew to become public, an account linked to him posted materials referencing the assault and the group’s battle with Clop. The account was deleted after Krebs contacted Khader’s father looking for one other interview.
FBI Breach Put ShinyHunters Below Intense Strain
The detention follows ShinyHunters’ September assault on the FBI Jobs portal. The group claimed it entered via apply.fbijobs.gov, defaced the location and obtained between 2TB and 3TB of data after accessing different programs.
The FBI confirmed it was investigating unauthorized exercise affecting the roles portal and alleged publicity of worker personally identifiable info.
The contents seem notably delicate. Reuters reviewed samples containing personally identifiable info, job roles and psychiatric and medical info belonging to FBI personnel. An inner FBI memo reportedly instructed employees to imagine each worker could have been uncovered.
ShinyHunters claimed it used an Oracle PeopleSoft vulnerability for the assault. Google Risk Intelligence Group and Mandiant individually documented ShinyHunters, tracked as UNC6240, mass-exploiting CVE-2026-35273 in opposition to PeopleSoft programs.
The flaw was first exploited as a zero-day primarily in opposition to universities earlier than the hackers modified their exploit to bypass WAF guidelines and expanded assaults into authorities, healthcare, expertise, transportation and different sectors.
Hackread.com later obtained a press release from ShinyHunters saying it had by no means meant to publish or promote the FBI information. The group described its one-week demand for the FBI to appropriate statements about its actions as a “advertising and marketing marketing campaign,” not an extortion deadline.
From Canvas and Rockstar to Giant SaaS Knowledge Theft
The FBI incident adopted an aggressive yr for ShinyHunters. In Might, the group focused Instructure’s Canvas studying platform, claiming it stole 3.65TB of data linked to just about 9,000 establishments and roughly 275 million customers.
Instructure confirmed uncovered info included names, electronic mail addresses, scholar IDs and inner Canvas messages, though the hackers’ bigger figures weren’t independently verified.
The group then defaced Canvas login portals utilized by a whole lot of faculties and universities, disrupting entry throughout exams and project durations. Instructure later introduced that it had reached an settlement with the attackers meant to forestall publication of the stolen info.
Rockstar Video games was one other goal. ShinyHunters claimed in April that it gained entry to Rockstar’s Snowflake atmosphere via credentials or tokens uncovered following a third-party incident involving Anodot.
Rockstar subsequently confirmed {that a} restricted quantity of non-material firm info had been accessed via a third-party breach, whereas saying gamers and its operations had been unaffected.
Google has additionally documented a a lot bigger ShinyHunters-branded marketing campaign involving voice phishing, pretend credential pages and theft from cloud companies together with Salesforce.
The operations focused company SSO credentials and MFA codes earlier than extracting information from SaaS platforms and utilizing it for extortion. Google tracks a number of associated clusters individually as a result of membership and partnerships inside the ShinyHunters infrastructure can change and impersonation can also be a priority.
Second Main Detention in Weeks
Khader’s detention follows the September arrest within the Netherlands of Pepijn van der Stap, a beforehand convicted hacker suspected by Dutch investigators of enjoying a task in ShinyHunters. The FBI described Van der Stap as one of many group’s alleged leaders, though ShinyHunters denied to Hackread.com that he had any affiliation with them.
The FBI says ShinyHunters and its alleged co-conspirators have breached greater than 140 organisations since final yr and picked up not less than $70 million in extortion funds. After the Dutch arrest, FBI Cyber Division Assistant Director Brett Leatherman publicly warned remaining members that arrests and seized infrastructure had been offering investigators with new info.
Occasions this week recommend investigators had been already closing in. Reuters misplaced contact with ShinyHunters via an account beforehand utilized by the group on Tuesday. Its darkish site disappeared Wednesday, shortly after the deadline in its dispute with the FBI expired. The operators later attributed the outage to sabotage by rivals and an unrelated disruption.
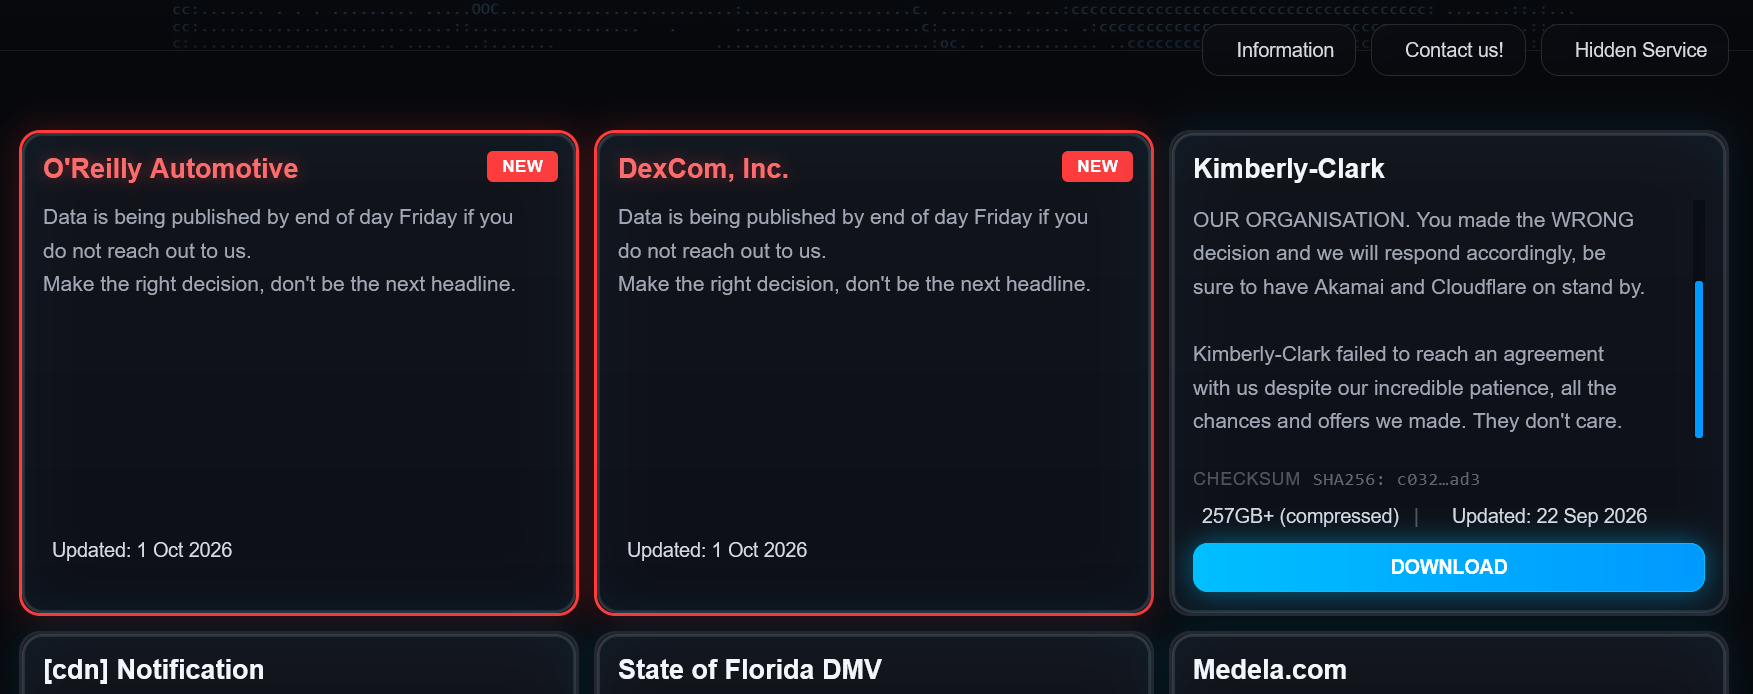
The newest reporting goes additional. Two sources informed Reuters that Khader is strolling investigators via his digital units and communications to assist determine different members. One supply described his cooperation as essential to persevering with arrest efforts.
For a bunch whose membership has usually been troublesome to outline, entry to a suspected operator’s units and communications might give investigators info that public aliases and leak websites can’t. What Khader has offered, whether or not he faces fees, and whether or not Jordan intends to extradite him haven’t been disclosed.