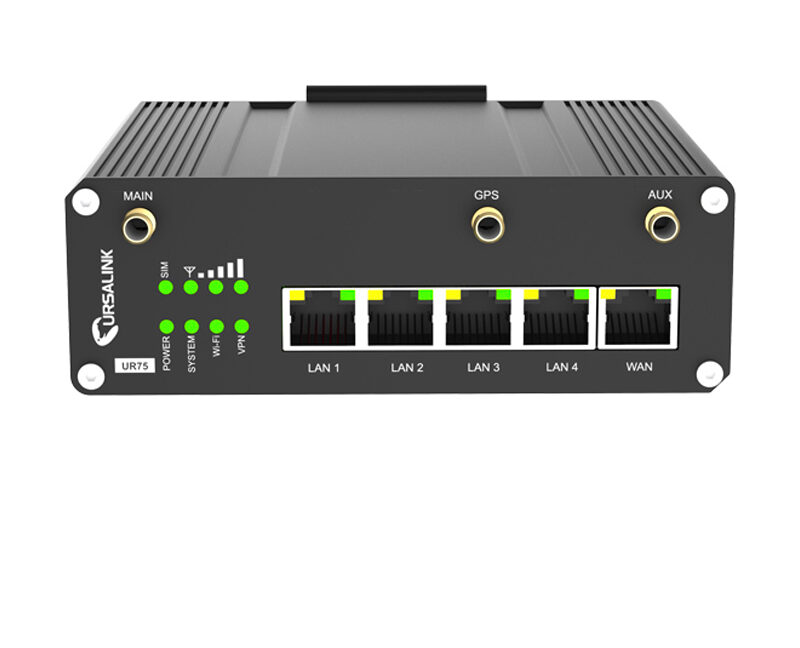
The researchers added: “This marketing campaign is notable in that it demonstrates how impactful smishing operations might be executed utilizing easy, accessible infrastructure. Given the strategic utility of such tools, it’s extremely seemingly that comparable gadgets are already being exploited in ongoing or future smishing campaigns.”
Sekoia stated it’s unclear how the gadgets are being compromised. One risk is thru CVE-2023-43261, a vulnerability within the routers that was fastened in 2023 with the discharge of model 35.3.0.7 of the system firmware. The overwhelming majority of 572 recognized as unsecured ran variations 32 or earlier.
CVE-2023-43261 stemmed from a misconfiguration that made recordsdata in a router’s storage publicly accessible by way of an internet interface, in accordance with a put up revealed by Bipin Jitiya, the researcher who found the vulnerability. Amongst different issues, a number of the recordsdata contained cryptographically protected passwords for accounts, together with the system administrator. Whereas the password was encrypted, the file additionally included the key encryption key used and an IV (initialization vector), permitting an attacker to acquire the plaintext password after which acquire full administrative entry.
The researchers stated that this principle was contradicted by a number of the info uncovered of their investigation. For one, an authentication cookie discovered on one of many hacked routers used within the marketing campaign “couldn’t be decrypted utilizing the important thing and IV described within the article,” the researchers wrote, with out elaborating additional. Additional, a number of the routers abused within the campaigns ran firmware variations that weren’t vulnerable to CVE-2023-43261.
Milesight did not reply to a message in search of remark.
The phishing web sites ran JavaScript that prevented pages from delivering malicious content material except it was accessed from a cellular system. One web site additionally ran JavaScript to disable right-click actions and browser debugging instruments. Each strikes have been seemingly made in an try to hinder evaluation and reverse engineering. Sekoia additionally discovered that a number of the websites logged customer interactions by way of a Telegram bot often known as GroozaBot. The bot is thought to be operated by an actor named “Gro_oza,” who seems to talk each Arabic and French.
Given the prevalence and big quantity of smishing messages, individuals usually marvel how scammers handle to ship billions of messages per 30 days with out getting caught or shut down. Sekoia’s investigation means that in lots of circumstances, the assets come from small, often-overlooked packing containers tucked away in janitorial closets in industrial settings.