Agentic AI
,
Identification & Entry Administration
,
Privileged Entry Administration
Royal Financial institution of Canada, Ping Identification on Privilege, Runtime Management and AI Governance
As AI brokers acquire entry to enterprise purposes, information and privileged techniques, identification groups face a brand new problem: How do you govern identities that may act autonomously and at machine velocity?
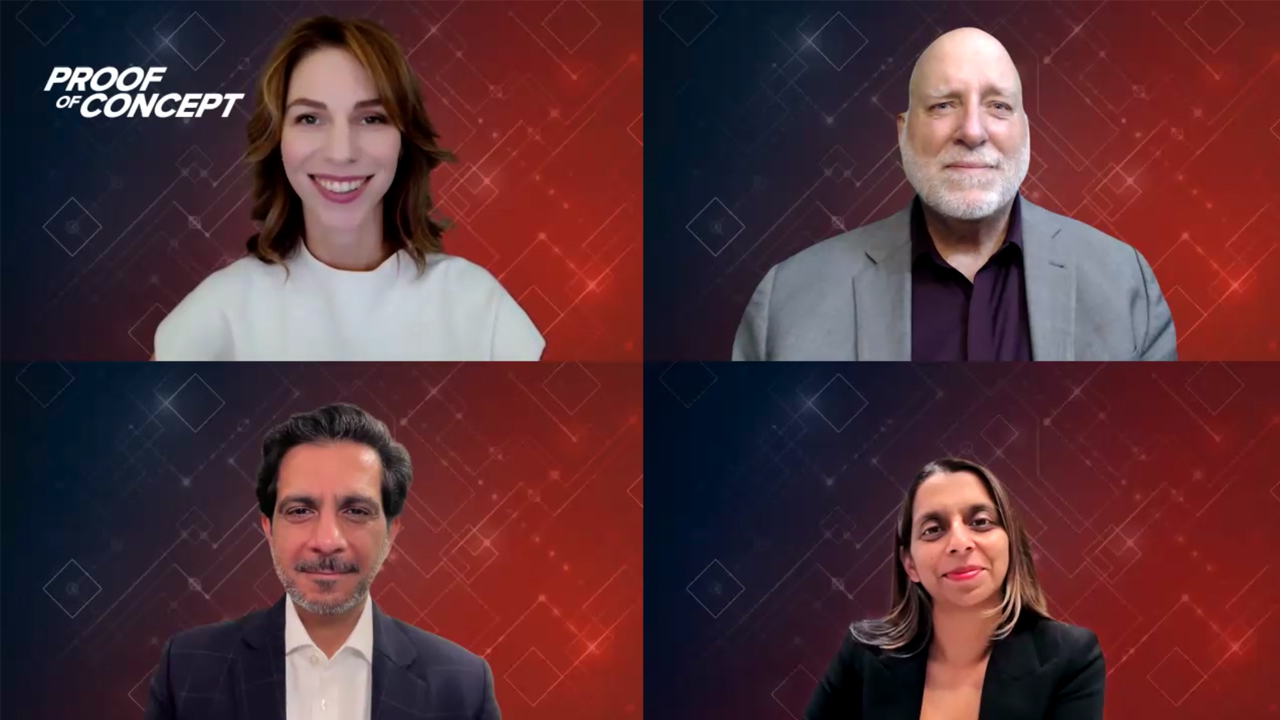
Within the newest “Proof of Idea,” Melissa Carvalho, Vice President of World Safety Identification and Entry Administration at Royal Financial institution of Canada, and Gaurav Sharma, Vice President of Workforce Product Technique at Ping Identification, talk about how AI brokers are reshaping identification governance, privileged entry and accountability.
As NIST turns its consideration to AI agent identification and authorization, organizations must know which brokers exist, who owns them, what they’ll entry and whether or not they need to be approved to take a particular motion at a particular second.
“We actually should redefine what we consider privilege and the way we handle privilege entry for these brokers, or for these accounts,” Carvalho stated.
Carvalho and Sharma joined ISMG’s Anna Delaney and Tom Discipline to debate:
- Why AI brokers require new approaches to privileged entry and least-privilege controls
- How organizations can uncover shadow brokers and prioritize controls by the potential blast radius of a compromise
- Why steady monitoring, runtime authorization and speedy containment matter as brokers acquire autonomy
Do not miss our earlier installments of “Proof of Idea,” together with the Could 6 version on disaster response and the Could 7 version on managing the aftermath of a breach.