Verizon’s 2026 Knowledge Breach Investigations Report (DBIR) places vulnerability exploitation on the prime of its preliminary entry vectors, at 31%. Remediation went the opposite approach. Solely 26% of the issues in CISA’s KEV (Identified Exploited Vulnerabilities) catalog have been totally remediated in 2025, down from 38% a yr earlier, and the median time to full decision grew from 32 days to 43.
These figures cowl organizations of each dimension. On a group the place one or two individuals personal safety alongside infrastructure or product work, choose a scanner by how a lot it leaves you to do after it finishes.
Key Takeaways
- Intruder is the strongest all-round match right here: hosted and fast to start out, with exterior, net app and cloud protection in a single account.
- Aikido Safety and Topscan.me each put code and operating techniques in the identical product. Aikido leans towards builders, Topscan towards the perimeter.
- HostedScan offers you established open-source engines with out operating them, and Pentest-Instruments.com provides hands-on exploit validation.
- Detectify suits when many of the threat sits in net apps and subdomains, and Tenable Nessus when inner networks matter and somebody can function a scanner.
How These Instruments Had been In contrast
“Lean” right here means one to a few individuals who personal safety alongside different work, usually a DevOps lead, an IT supervisor or a CTO. Every software was checked in opposition to 4 questions from that individual’s viewpoint:
- Can one individual begin alone? Join, add a goal and see outcomes with out an equipment or a gross sales name.
- Does it cowl what faces the web? Exterior infrastructure and net functions, on a plan a small group would realistically purchase.
- Does it assist resolve what to repair first? Some sign past a uncooked CVSS rating, and sufficient element to behave on a discovering with out reproducing it from scratch.
- What occurs after the repair? Rescans that affirm it, a standing historical past, and a route into Jira, Slack or related.
The details under come from distributors’ public pricing pages and documentation as of early November 2026. None of this can be a detection benchmark, so solely a trial can present accuracy by yourself stack. Costs rely on asset counts and alter usually, so they’re neglected.
The 7 Finest Vulnerability Scanning Instruments for Lean Safety Groups
The place two instruments got here out stage on these questions, the one which removes the necessity for one more buy (cloud, code or inner protection) ranks increased.
1. Intruder
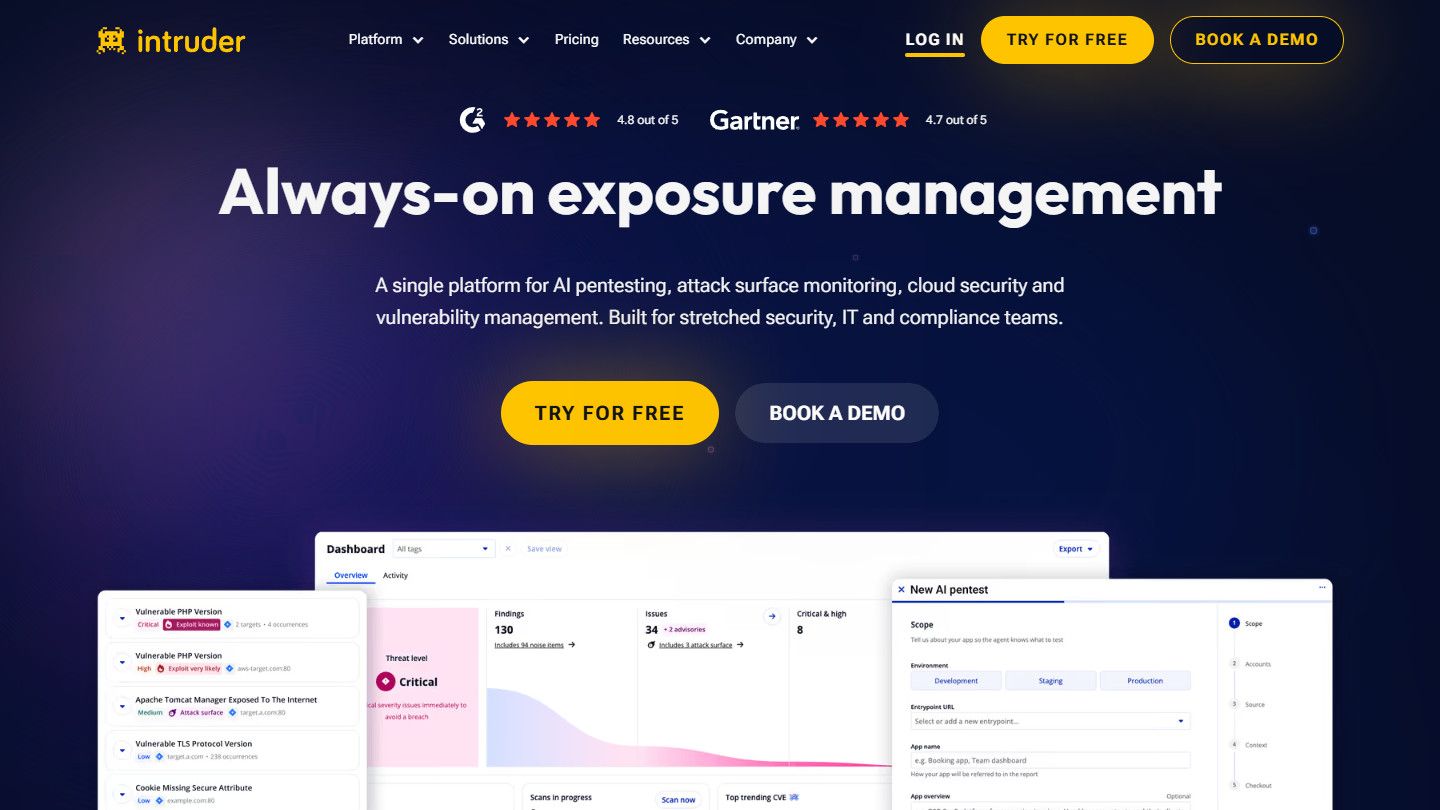
Intruder pitches its plans at “lean, time-strapped groups” and retains setup brief: you join cloud accounts, add domains and IPs, and exterior scanning begins with no brokers. The corporate says it runs greater than 170,000 checks in opposition to internet-facing belongings. Outcomes are ordered by severity, exploitability and risk intelligence, and each comes with remediation steps.
Paid plans add rising risk scans, which test your property when a brand new flaw goes public as a substitute of ready for the following scheduled run. In addition they add authenticated net app and API testing, every day cloud checks throughout AWS, Azure and Google Cloud, and integrations equivalent to Jira and Slack.
Finest for: Small groups that need exterior, net and cloud protection with little setup and a transparent repair order.
Commerce-off: The free plan leaves out net apps and screens solely ports 80 and 443. Inner and agent-based scanning begins on the Professional plan, which fits by gross sales, and automatic discovery of unknown belongings sits in Enterprise.
2. Aikido Safety
Aikido begins from the repository. Dependency scanning, static evaluation and secrets and techniques detection run alongside DAST, container scanning, infrastructure-as-code and cloud misconfiguration checks in a single account. Triage is its essential argument for a small group: reachability evaluation filters out findings that may’t be reached, the triage learns customized context out of your docs, and fixes can arrive as pull requests. The free Developer plan covers two customers, ten repositories, one area and one cloud account, with no card required.
Finest for: Software program groups the place builders repair what the scanner finds and code is the primary concern.
Commerce-off: Assault floor monitoring begins on the Professional plan, and licensing counts the builders lined, which fits product groups higher than IT teams with few coders. AutoTriage for code findings isn’t on the free plan.
3. Topscan.me
Topscan.me publishes what its engine runs at every stage and what it intentionally leaves alone, which helps when the individual shopping for the scanner additionally solutions for manufacturing. Its discovery stage works from public information (certificates transparency logs and DNS) plus a single regular HTTP request to every host, so it may possibly map a site earlier than something is accredited. Port checks and energetic templates are restricted to targets you’ve got confirmed, at a capped request charge, and nothing damaging is shipped.
A discovering exhibits its proof: the host, the standing code, the response header or certificates date behind it, and when it was checked. The following scan closes a set challenge with a date, and one which comes again is marked as reopened. Static code and dependency evaluation for GitHub and GitLab repositories sits in the identical workspace. Paid plans add net utility scanning and, for perimeter findings, SLA timers that begin at first detection. On the free plan, one host will get a weekly scan alongside one repository and one consumer, and a 14-day trial of a paid plan wants no card.
Finest for: Groups the place a DevOps lead or CTO owns safety amongst different issues and desires the perimeter and code below one subscription.
Commerce-off: There isn’t a inner community scanning, as a result of hosts want a public tackle to be scanned. Cloud integration covers AWS solely, and Slack, Microsoft Groups and Jira routing isn’t on the entry-level paid plan.
4. HostedScan
HostedScan runs established engines so that you don’t need to: OpenVAS, OWASP ZAP, Nuclei, Nmap and SSLyze on each plan, with Nessus on the highest tier. Triage rests on CVSS and EPSS scores and a report-card grade for every goal, and you’ll settle for, remediate and observe every vulnerability by its lifecycle. Assault floor mapping and limitless group members include each plan, and the 14-day trial wants no card. The corporate counts greater than 5,000 MSPs and IT groups as prospects, and its reporting options lean that approach.
Finest for: IT groups and MSPs that belief open-source engines however lack the time to run them, and want experiences for auditors or shoppers.
Commerce-off: Authenticated scans, inner community scanning, APIs and webhooks begin on the Premium plan. Supply code isn’t lined.
5. Pentest-Instruments.com
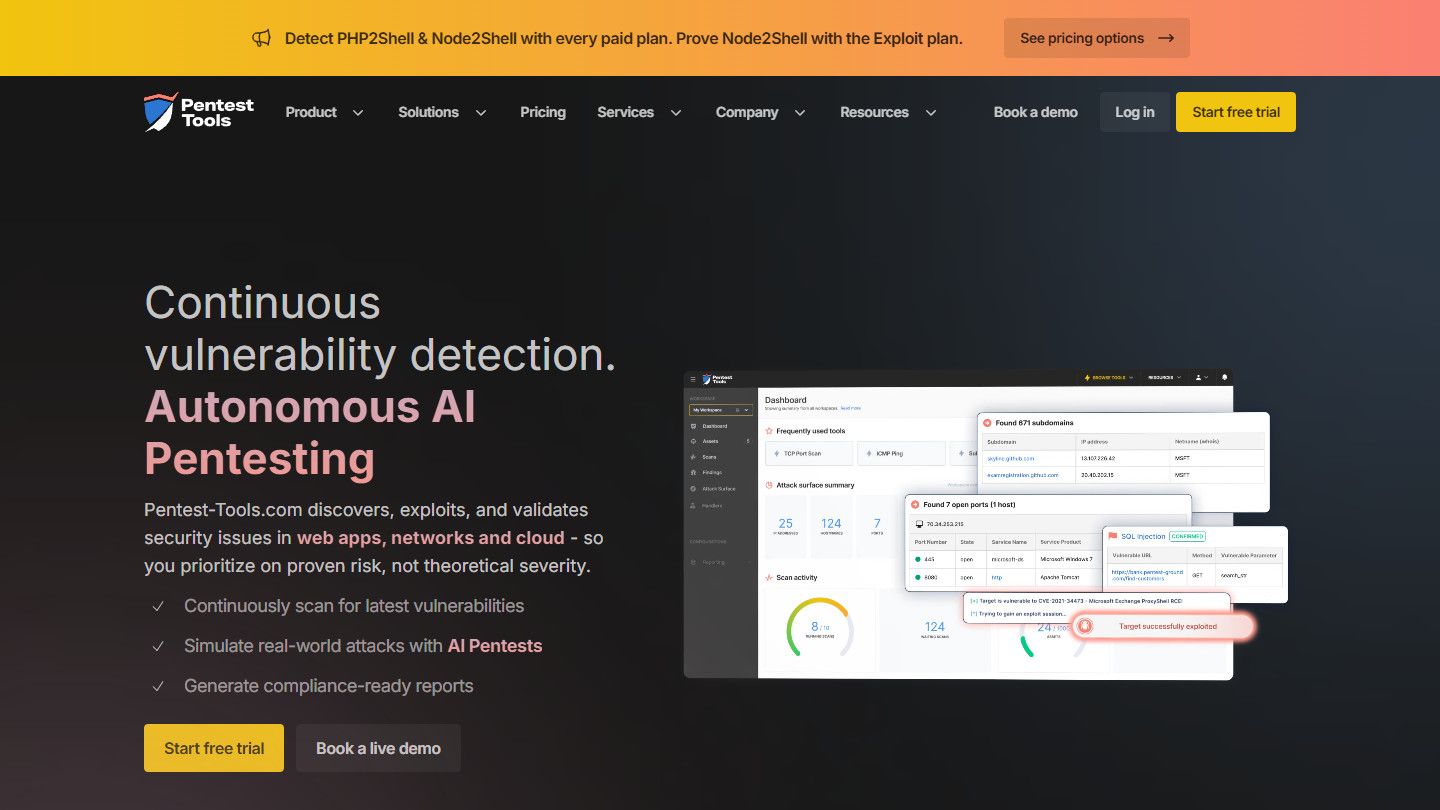
Pentest-Instruments.com comes from the pentesting facet, and its catalog of 19 instruments exhibits it: community, web site, API and cloud scanners subsequent to recon instruments and exploiters. The findings view teams related outcomes and flags duplicates, and you’ll filter by goal, severity, verification state or standing.
Each paid plan consists of limitless rescans on community and net app belongings, scan automation, limitless group members, and integrations equivalent to Jira and Microsoft Groups. The Exploit plan provides Sniper, an computerized CVE exploiter, which turns out to be useful when an engineer asks for proof {that a} discovering is actual.
Finest for: A group with some offensive safety expertise that desires to validate findings itself.
Commerce-off: The NetScan plan has solely restricted net and API scanning, so a group with its personal net app wants AppScan or above. Inner community scanning is an optionally available add-on, and the vary of instruments takes some studying for anybody new to pentesting.
6. Detectify
Detectify concentrates on what may be reached by domains and net apps. Floor Monitoring maps subdomains from certificates transparency logs, DNS enumeration and brute-forcing, finds open ports, and runs payload-based exams that the corporate says come from greater than 1,765 modules constructed by moral hackers in its Crowdsource group. Utility Scanning goes deeper, crawling single-page apps and testing behind a recorded login.
For a small group, the payload is the helpful half, as a result of the discovering exhibits what triggered it. Subdomain takeover checks run each eight hours, and people findings shut robotically as soon as the document is fastened. These alerts can go to Slack, Jira or Microsoft Groups. The Starter tier has no platform charge and permits as much as 5 customers.
Finest for: SaaS firms whose publicity is especially net apps, APIs and a sprawl of subdomains.
Commerce-off: Floor Monitoring and Utility Scanning are billed per area and per goal, along with any platform charge. Inner scanning begins on the Skilled tier, and tiers above Starter undergo a demo or gross sales.
7. Tenable Nessus
Nessus seems in nearly each roundup of vulnerability scanning instruments and is the one software right here you run your self. It deploys on a variety of platforms, together with a Raspberry Pi, so getting it inside an inner community is simple. Prioritization attracts on EPSS, CVSS and Tenable’s VPR, and greater than 450 preconfigured templates embrace configuration audits in opposition to CIS benchmarks.
Nessus Skilled doesn’t embrace net utility or exterior assault floor scanning, which include Nessus Skilled. Verify the license earlier than planning across the free version, too: Tenable now describes Nessus Necessities as a 30-day license restricted to 5 IPs and strictly for non-commercial use.
Finest for: Groups with inner networks to evaluate and somebody snug working a scanner.
Commerce-off: You host it, schedule it and preserve it up to date. Outcomes dwell within the scan and its experiences, so assigning findings and monitoring fixes normally strikes to a ticket system. Tenable itself pitches Nessus Skilled at consultants, pentesters and safety professionals.
The Seven Facet by Facet
| Instrument | Getting began | Web-facing protection | Triage sign | After the repair |
| Intruder | Free plan, 14-day trial | Exterior on each plan, net apps and APIs on paid plans | Severity, exploitability, risk intelligence | Remediation scans; Jira and Slack on paid plans |
| Aikido Safety | Free plan, no card | DAST on each plan, assault floor monitoring from Professional | Reachability, EPSS, AutoTriage | Computerized rescans; Jira sync from Fundamental |
| Topscan.me | Free plan and 14-day trial, no card | Exterior on each plan, net apps on paid plans | Severity, publicity, proof on every discovering | Closed with a date, reopened if it returns; Jira and Slack above the entry plan |
| HostedScan | 14-day trial, no card | Exterior and net apps on each plan | CVSS, EPSS, goal grades | Settle for and observe every discovering; Slack on each plan |
| Pentest-Instruments.com | Free version, free trial | Community on each paid plan, full net and API from AppScan | Grouped findings, verification state, exploit checks on the highest plan | Limitless rescans; Jira and Groups on each paid plan |
| Detectify | Starter tier, trial | Floor Monitoring and Utility Scanning, billed per area and goal | Payload-based proof | Takeover findings shut robotically; Slack, Jira, Groups |
| Tenable Nessus | Trial, self-hosted | Networks on each version, net apps and exterior assault floor on Skilled | EPSS, CVSS, Tenable VPR | Rescans you schedule; experiences and exports |
Which One to Strive First
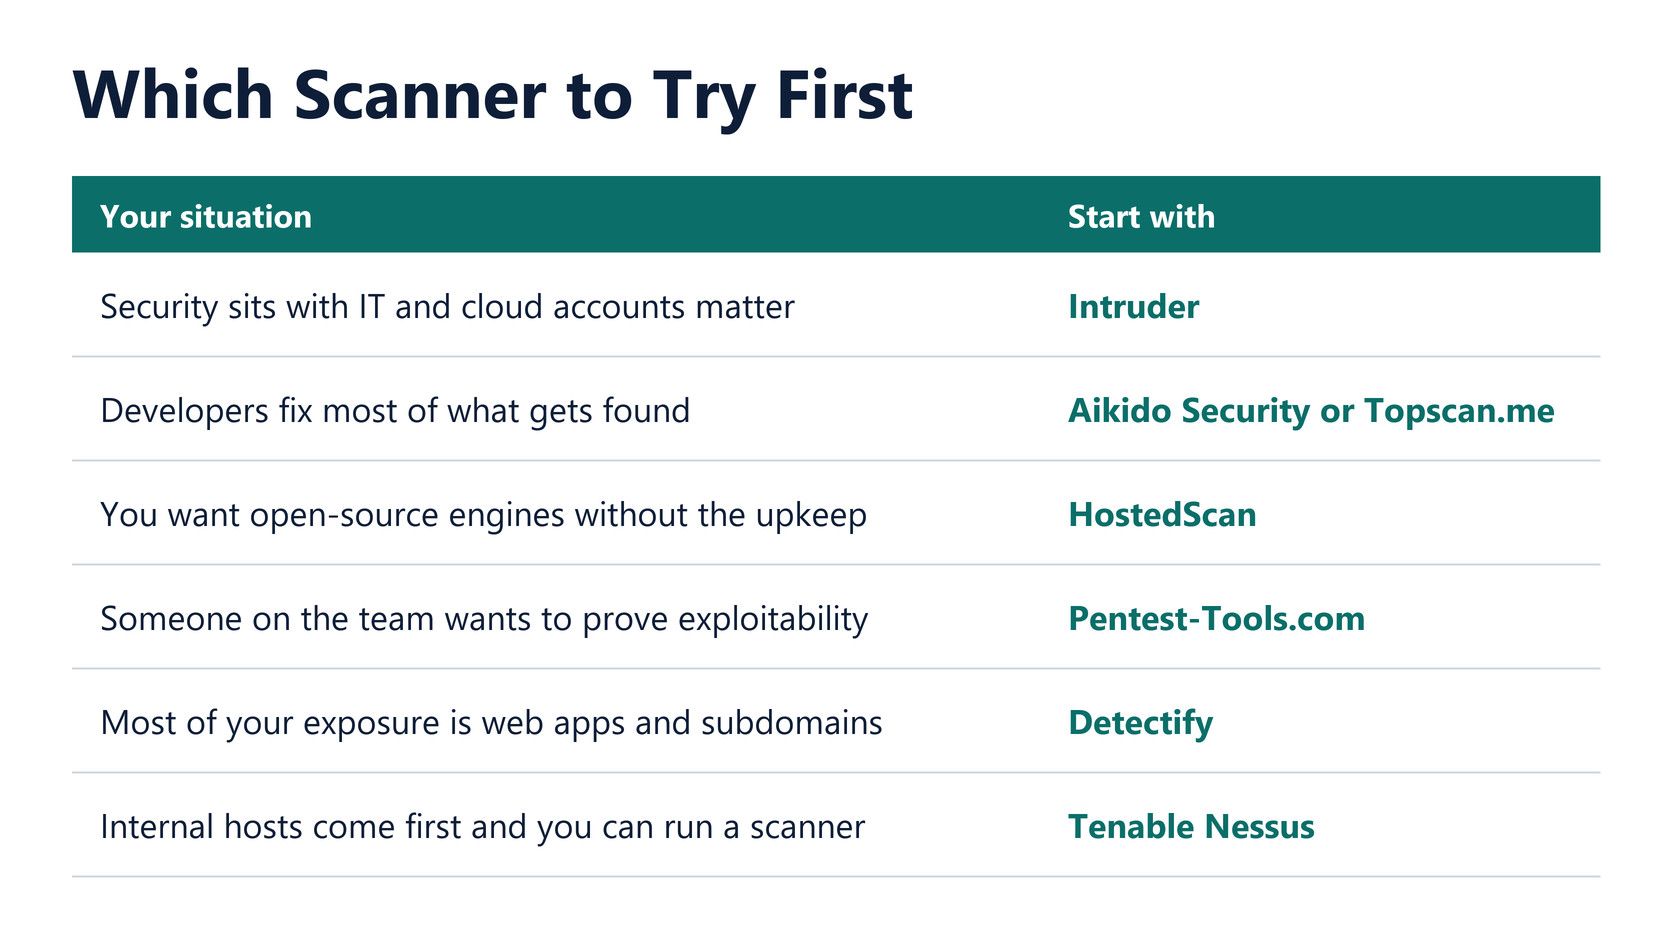
- Safety sits with IT and cloud accounts matter: Intruder.
- Builders repair most of what will get discovered: Aikido Safety or Topscan.me.
- You need open-source engines with out the maintenance: HostedScan.
- Somebody on the group needs to show exploitability: Pentest-Instruments.com.
- Most of your publicity is net apps and subdomains: Detectify.
- Inner hosts come first and you’ll run a scanner: Tenable Nessus
Who Didn’t Make the Checklist
Qualys VMDR and Rapid7 head many roundups for good purpose. Qualys spans digital scanners, cloud brokers, passive sensors and container sensors, and Rapid7 now sells InsightVM as a part of Publicity Command. Each are constructed for packages with individuals devoted to operating them, which is normally multiple or two part-time house owners want.
OpenVAS and Nuclei are free and succesful, and HostedScan and Intruder each use them. On their very own they’re engines, so scheduling, internet hosting and triage are yours to construct. They match if somebody has that point.
Internet-only and cloud-only vulnerability scanning software program misses the second query, although it may possibly sit subsequent to something on this record.
Tips on how to Check a Shortlist
Run the trial on belongings you’re approved to check, ideally a staging host with a couple of identified issues equivalent to an outdated package deal, a weak TLS setting or an admin panel left open. Then test:
- Does the software discover what you planted, and the way a lot unrelated noise arrives with it?
- Can a non-specialist perceive a discovering and confirm it from the small print within the report?
- Whenever you repair one thing after which break it once more, does the software shut it with a date and reopen the identical discovering, or does it create a brand new one?
- What does the license depend? Intruder and HostedScan depend targets, Pentest-Instruments.com counts belongings, Detectify counts domains and app targets, Aikido counts builders, and Topscan counts hosts, net apps and repositories. Rely your personal property in that unit earlier than evaluating plans.
Often Requested Questions
What’s the Distinction Between Vulnerability Scanning and Penetration Testing?
A vulnerability scan is an automatic, repeatable test for identified weaknesses and misconfigurations. A penetration check goes after what automation misses, equivalent to enterprise logic flaws and chains of smaller points. Scanning retains watch between exams.
Can a Vulnerability Scan Break Manufacturing?
It could possibly. Energetic checks ship actual site visitors, and fragile providers could react badly to it. Earlier than you scan manufacturing, take a look at what the software sends, whether or not it limits request charges, and whether or not you may level it at staging first.
Is a Free Vulnerability Scanner Sufficient for a Small Crew?
It may be a begin in case you solely have a couple of hosts. The free plans from Intruder, Aikido and Topscan.me all cap targets and maintain again options, and net app testing is the one to test first in case you run your personal utility.
Do Small Groups Want Inner Scanning as Effectively as Exterior?
Begin with what faces the web, since anybody can attain it. Inner scanning issues extra as soon as a framework requires it, and PCI DSS is one which does, so test your personal compliance scope earlier than ruling it out.