In March 2025, the Ricochet Chollima APT group, widely known as APT37 and linked to North Korean state-sponsored operations, launched a focused spear-phishing marketing campaign in opposition to activists centered on North Korean affairs.
The risk actors initiated the assault chain by way of spear-phishing emails impersonating a North Korea-focused safety professional primarily based in South Korea.
The emails referenced professional subjects, together with North Korean troops deployed to Russia and a nationwide safety convention hosted by a South Korean assume tank, to ascertain credibility.
The assault, dubbed “Operation: ToyBox Story” by Genians Safety Middle (GSC), reveals subtle strategies combining LNK file exploitation with fileless malware execution to evade conventional safety options.
The malicious emails contained Dropbox hyperlinks redirecting victims to compressed ZIP archives containing weaponized LNK shortcut recordsdata.
Multi-Stage Supply Mechanism
The assault employed a fastidiously orchestrated supply approach. The primary documented case occurred on March 8, 2025, with an e mail titled “To North Korean Troopers Deployed to the Russian Battlefield.hwp.”
The attachment mimicked a professional Hangul (HWP) doc by leveraging the HWP icon related to Naver Mail, growing the probability of sufferer interplay nevertheless, the embedded hyperlink redirected to Dropbox moderately than delivering the claimed doc.
Upon extraction, victims found a ZIP archive containing a malicious LNK file sharing the identical identify because the archive, differing solely in file extension.
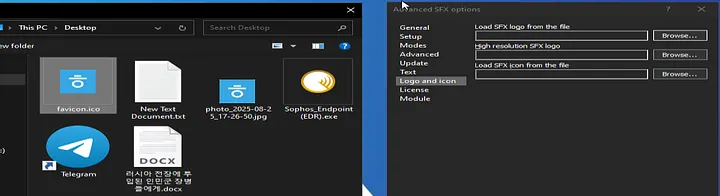
A secondary marketing campaign variant on March 11, 2025, used a “Associated Poster.zip” archive containing each a benign JPG picture and a malicious LNK shortcut file to keep up misleading appearances.
The LNK file serves because the assault’s important part, embedding hidden PowerShell instructions designed to execute robotically upon activation.
When triggered, the shortcut launches a multi-stage payload supply course of. The embedded instructions create three short-term recordsdata within the %Temp% listing and execute a BAT batch file whereas displaying a decoy HWP doc to the consumer.
The execution sequence entails loading “toy02.dat” as a loader, which then hundreds “toy01.dat” from the short-term folder. These recordsdata comprise XOR-transformed information that, when decoded, is injected into reminiscence as executable shellcode.
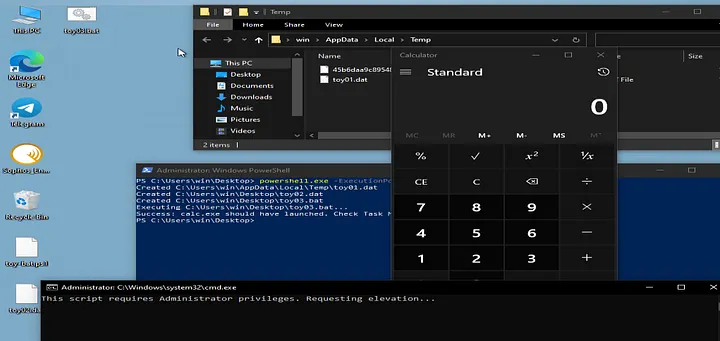
This fileless approach allows runtime malware injection and dynamic code execution with out writing malicious binaries to disk, successfully bypassing signature-based endpoint detection methods.
RoKRAT Payload and C2 Communication
The ultimate payload deploys the RoKRAT distant entry trojan, which collects intensive system info, together with Home windows OS construct model, laptop identify, consumer credentials, BIOS model, and system producer.
RoKRAT captures real-time screenshots and exfiltrates information by means of encrypted channels utilizing AES-CBC-128 encryption, with AES keys additional secured by way of RSA encryption.
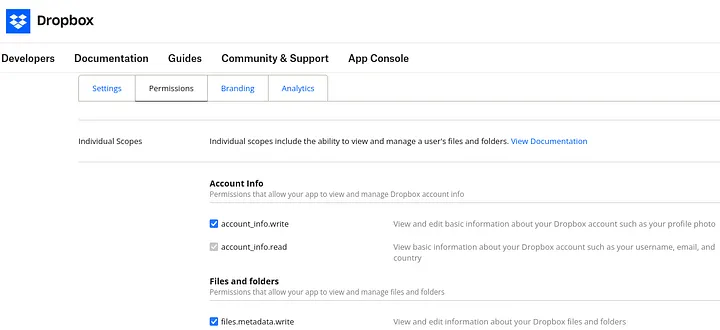
Most notably, the malware leverages Dropbox as a command-and-control server, utilizing cloud API providers to cover malicious site visitors amongst professional Dropbox communications.
This “Dwelling off Trusted Websites” (LoTS) approach complicates detection by safety groups analyzing community site visitors.
Organizations ought to prohibit LNK file execution from e mail attachments and implement endpoint detection and response (EDR) options able to monitoring fileless assaults by means of behavioral anomaly detection.
The marketing campaign demonstrates APT37’s continued sophistication in exploiting professional cloud providers to keep up persistent entry whereas evading conventional safety controls.
Observe us on Google Information, LinkedIn, and X to Get Instantaneous Updates and Set GBH as a Most popular Supply in Google.