A global police operation has disrupted the KillSec ransomware group, with three suspects arrested, 5 servers seized and a minimum of 110 terabytes of stolen information positioned below legislation enforcement management. Investigators say the suspected administrator and essential operator is barely 16 years outdated.
The operation befell on September 30 as a part of Operation KillSwitch, an investigation led by German authorities into roughly 1,000 suspected assaults worldwide. Eurojust and Europol coordinated authorities from Belgium, Finland, Germany, Greece, Romania, Spain, Switzerland, the UK and america.
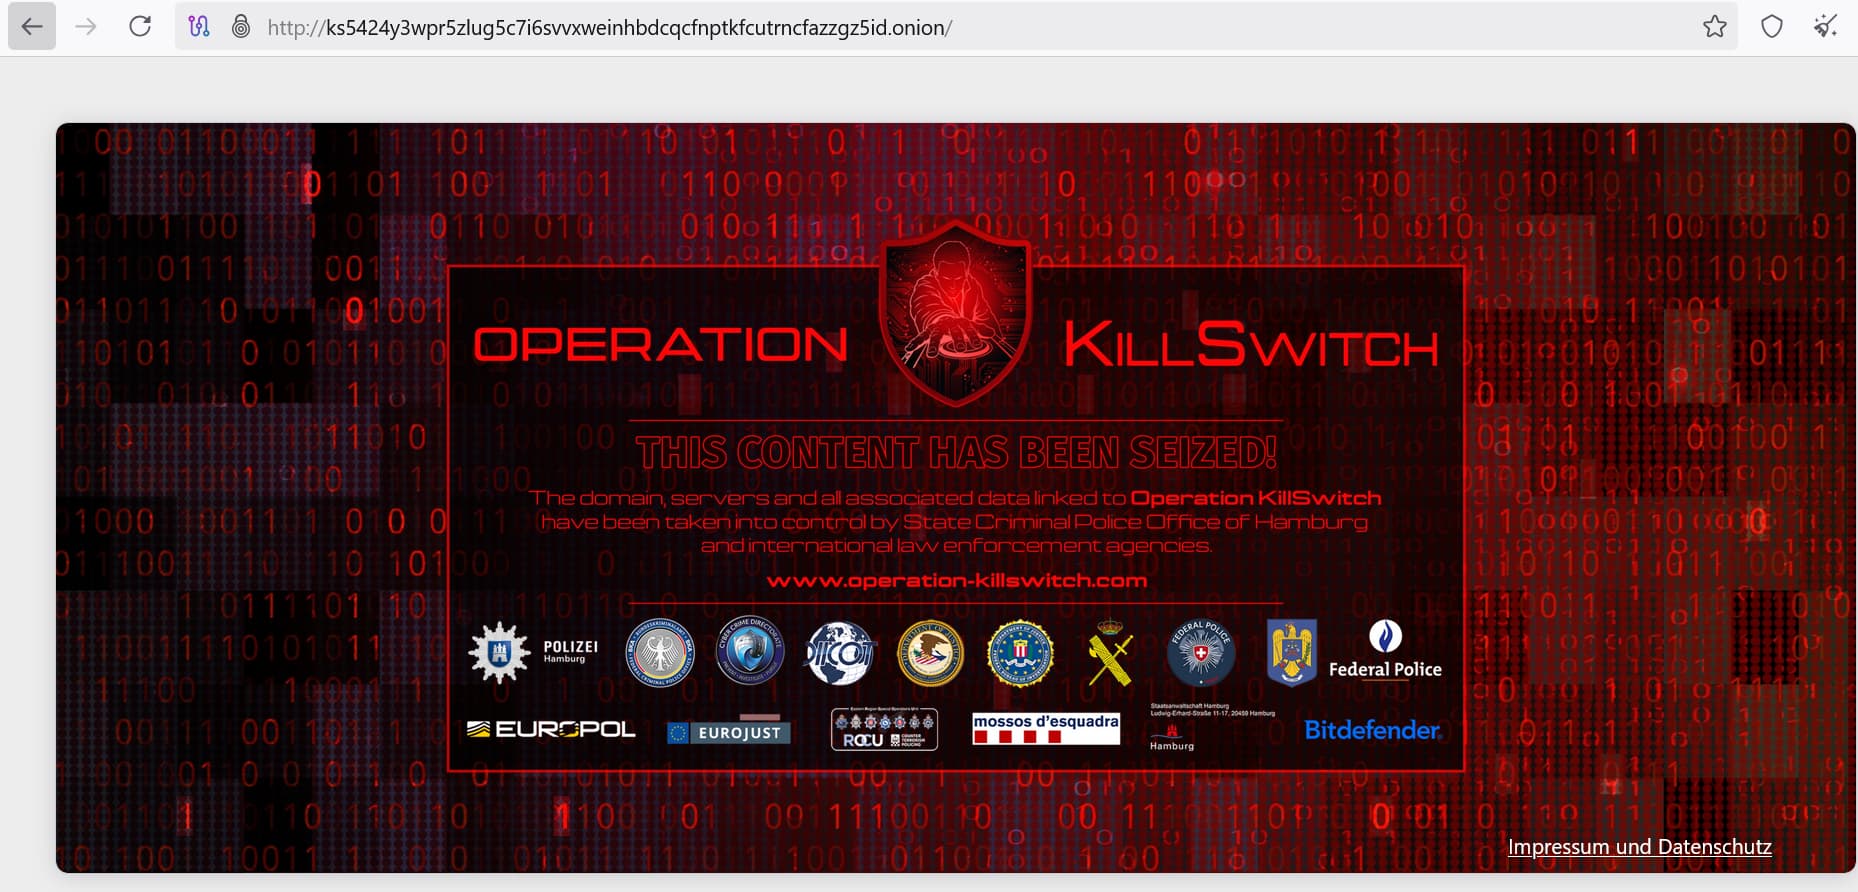
Guests to KillSec’s darkish net leak website now see a seizure discover stating that the area, servers and related information have been taken below the management of the State Felony Police Workplace of Hamburg and worldwide legislation enforcement companies. The separate Operation KillSwitch web site additionally confirms the coordinated motion in opposition to the group.
Teenager Recognized as Suspected Predominant Operator
Investigators recognized a number of individuals suspected of performing totally different jobs for KillSec, together with an administrator, developer, negotiator and affiliate. Based on Eurojust’s press launch, {the teenager} suspected of serving as administrator was additionally thought of the group’s essential operator. One other suspected developer turned 18 in August 2026 and was nonetheless a minor when a few of the alleged offences befell.
Spanish authorities arrested the 16-year-old in Alicante, in keeping with further info launched Thursday. He’s a Romanian nationwide. Two different suspects of their twenties had been arrested in Britain and Romania, whereas the suspected 18-year-old developer has been recognized however was not reported as arrested.
A kind of detained in Britain is a 25-year-old man suspected of negotiating with KillSec victims. The Jap Area Particular Operations Unit stated he was arrested in Manchester and was because of seem at Westminster Magistrates’ Courtroom on October 1 for an extradition listening to.
KillSec Linked to Round 1,000 Assaults
Energetic since round 2024, KillSec gained entry to organisations by exploiting software program vulnerabilities and poorly secured entry factors, notably programs linked to cloud storage. Stolen info was copied to infrastructure managed by the group and used to strain victims into paying ransoms.
Victims had been named on KillSec’s leak website and despatched samples of stolen info as proof that the attackers had their recordsdata. Organisations that refused to pay might have their info printed free of charge. Authorities stated the group obtained substantial ransom funds in some instances.
Investigators have up to now recognized round 500 assaults that had been profitable, though that quantity might change as seized proof is examined. Europol additionally stated investigators discovered that KillSec members used synthetic intelligence to assist construct and keep their ransomware infrastructure and determine targets.
5 Servers and 110TB of Information Seized
Police searched eight properties in Greece, Romania, Spain and the UK throughout the coordinated motion. 5 servers utilized by KillSec had been seized, together with infrastructure holding info stolen from victims, whereas authorities additionally took management of domains operated by the group.
A minimum of 110TB of stolen information was secured in opposition to additional unauthorised entry. The quantity provides investigators a considerable physique of proof to look at as they work to determine further victims and other people suspected of collaborating in KillSec.
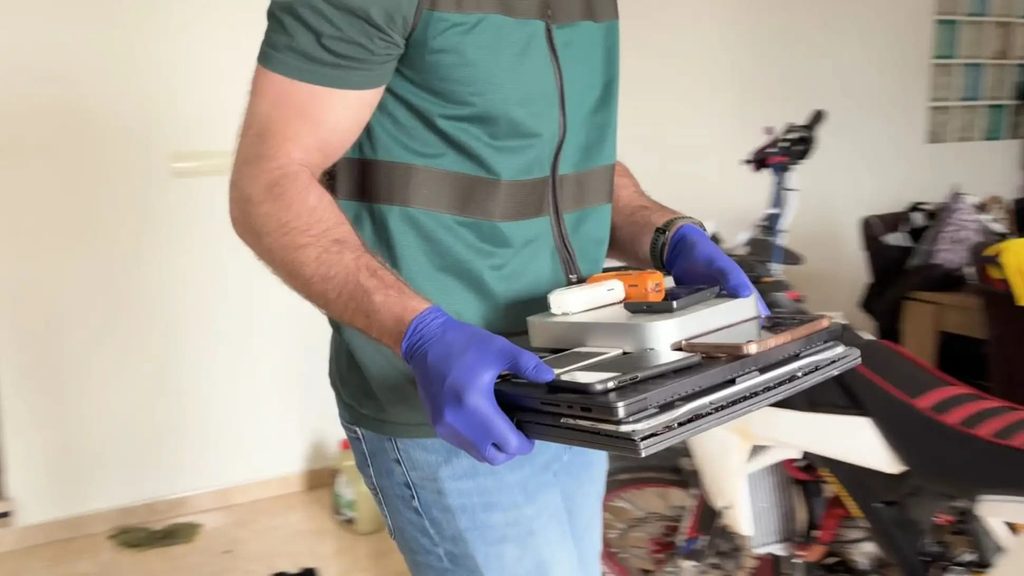
Authorities are additionally following the group’s monetary exercise. Europol offered specialist help for cryptocurrency tracing and examination of digital proof, whereas investigators are actually analysing seized units, servers and different materials for hyperlinks to additional assaults.
The operation stays energetic. Regulation enforcement has not stated that each suspected KillSec member has been arrested, and Eurojust stated the seized proof might determine further victims, assaults and other people concerned with the group.
Alicante Has Seen Different Younger Hacker Arrests
This isn’t the primary time Alicante has appeared in a case involving an alleged teenage hacker. Again in 2012, Hackread.com reported that police arrested a 16-year-old in Alicante accused of infecting computer systems with a Trojan and stealing financial institution particulars, social media passwords, emails, addresses and different private info.
{The teenager} was additionally accused of blackmailing victims and had allegedly used a neighbour’s web connection with out permission, initially main police to the fallacious individual.
One other case surfaced in February 2025, when an 18-year-old identified on-line as “Natohub” was arrested in Calpe, Alicante. Spanish authorities suspected him of greater than 40 assaults in opposition to private and non-private organisations, with targets linked to NATO, the US Military, the United Nations and Spain’s Civil Guard and authorities ministries. Police seized pc tools, an iPhone and entry to round 50 cryptocurrency accounts throughout the investigation.
Alicante was additionally the situation of a significant cybercrime arrest in December 2023, though that case didn’t contain a youngster. Spanish police arrested a Venezuelan nationwide accused of main the monetary operations of the Kelvin Safety hacker group.
Authorities linked the group to greater than 300 assaults in opposition to organisations in over 90 international locations and accused the suspect of laundering proceeds by cryptocurrency exchanges.