A newly tracked Home windows infostealer dubbed Remus is increasing its credential-theft playbook by concentrating on API tokens and native utilization information tied to AI platforms, together with OpenAI and Anthropic.
Researchers at SpyCloud Labs discovered that latest Remus builds harvest browser information, password-manager and 2FA-extension artifacts, cryptocurrency-wallet recordsdata, utility credentials, and AI assistant credential folders, doubtlessly exposing each particular person accounts and organizational AI workloads
SpyCloud researchers spent a number of weeks reverse engineering the malware, which appeared on underground marketplaces round March 2026.
The stealer is notable not only for the breadth of its assortment routines, however for combining Lumma-style browser theft with system-call evasion, COM-object abuse, staged exfiltration, and Ethereum-based command-and-control decision.
The most recent Remus configurations goal credential folders utilized by Anthropic, OpenAI, and different AI suppliers.
The theft of API tokens may enable criminals to eat paid mannequin capability, entry AI-development workflows, or pivot into methods linked to compromised developer environments.
Domestically saved LLM utilization historical past can also expose prompts, venture context, code fragments, cloud particulars, inside URLs, credentials unintentionally entered into chats, and different delicate operational information.
The danger is particularly acute the place builders use AI coding instruments alongside source-control, cloud, and ticketing platforms.
Safety reporting on the broader infostealer pattern has documented the theft of entry and refresh tokens, immediate histories, dialog databases, and MCP configuration recordsdata artifacts that may comprise API keys for linked companies.
This makes Remus greater than a standard password stealer. An uncovered AI token can grow to be a non-human id incident: an attacker might not have to crack a password or defeat MFA if a reusable API credential has already been copied from a compromised endpoint.
Remus targets information from 21 browsers and 16 cold-wallet purposes, in keeping with SpyCloud.
Its default assortment record contains Chromium-based browsers resembling Chrome, Edge, Courageous, Opera, Vivaldi, Arc, and Chrome Beta, in addition to purposes together with Claude Code, Cursor, Codex, OpenCode, Discord, Telegram, Azure, Google Cloud, Bitwarden, 1Password, KeePass, NordVPN, and OpenVPN.
The malware additionally collects a very giant set of Mozilla extension artifacts. Targets embody authenticator extensions, password managers, notes purposes, and crypto-wallet information.
The inclusion of 2FA-related extensions is critical as a result of saved authenticator secrets and techniques or session materials may allow account takeover even when victims have enabled multi-factor authentication.
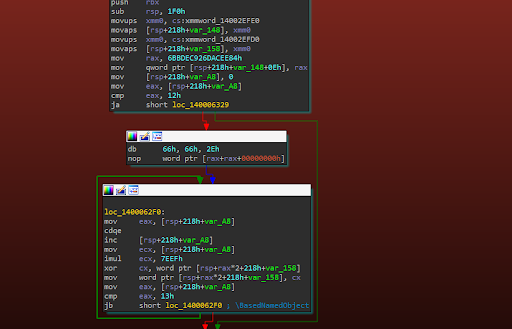
Remus, LummaC2, and several other different malware samples all make use of the identical personal OLLVM fork, which provides these string and arithmetic obfuscation routines.
Remus can even resolve Home windows shortcut recordsdata and steal the recordsdata to which they level. This provides operators one other route to gather precious paperwork from user-accessible places with out relying solely on fastened listing paths.
A standard an infection path is ClickFix social engineering. In these campaigns, victims encounter pretend CAPTCHA prompts distributed by way of phishing, malvertising, or compromised web sites, then are tricked into pasting and working malicious instructions themselves.
Remus Infostealer Marketing campaign
Public reporting has linked Remus exercise to ClickFix-to-SmokeLoader supply chains.
SpyCloud Researchers reported, recapturing 18.1 million uncovered API keys and tokens in 2025 throughout cloud, fee, developer, collaboration, and AI companies, underscoring the rising scale of this drawback.
As soon as lively, Remus makes use of a personal Obfuscator-LLVM fork for string and arithmetic obfuscation.
SpyCloud discovered overlap between its obfuscation routines and people utilized by LummaC2, whereas Gen Digital reported that Remus’s Chromium credential-theft strategy carefully resembles Lumma’s implementation.
The overlaps don’t independently show a single operator, however they level to shared code, tooling, or growth information throughout the ecosystem.
Remus additionally performs a syscall-hook sweep earlier than theft exercise, eradicating hooks that endpoint detection and response merchandise might use to look at suspicious habits.
It then makes use of syscall execution for delicate actions and generic Home windows COM objects to enumerate system info, shortcuts, and recordsdata extra quietly than overt API-heavy strategies.
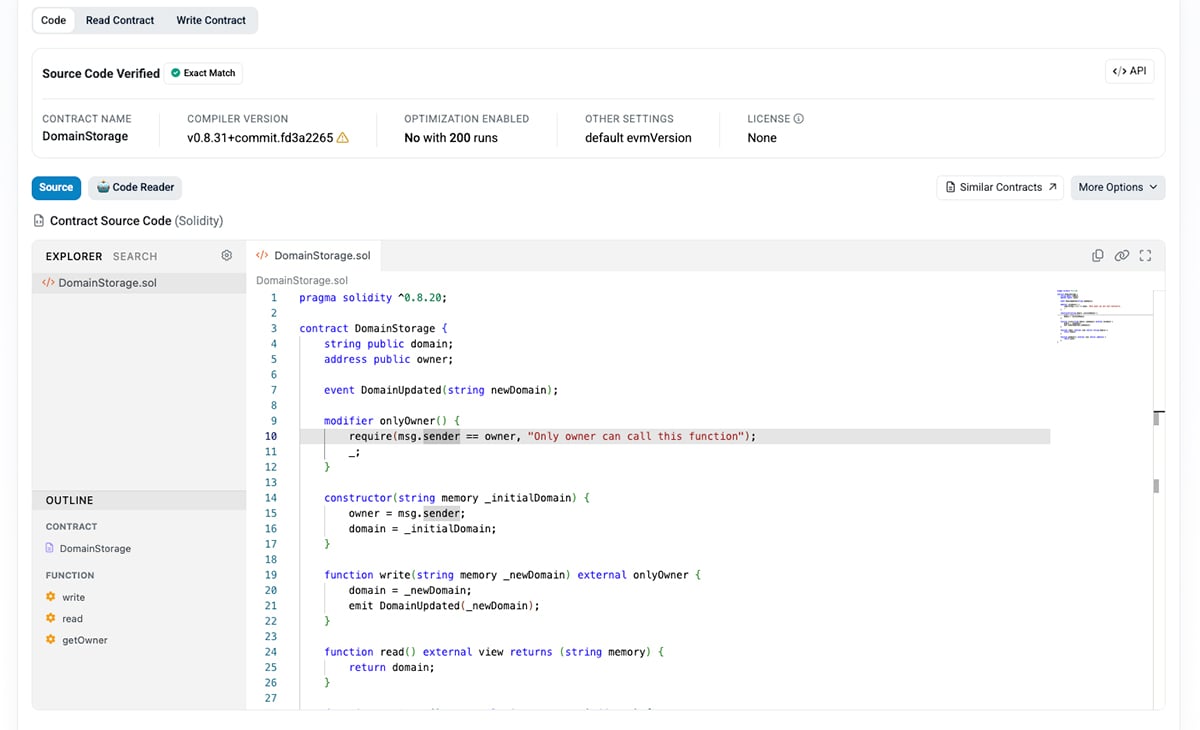
Certainly one of Remus’s most resilient options is its use of etherhiding to resolve dwell command-and-control infrastructure.
Somewhat than relying solely on a hardcoded C2 area, the malware queries an Ethereum good contract by way of a public RPC service and decodes the returned information into its present server tackle.
SpyCloud noticed Remus querying contract 0x999941b74F6bbc921D5174A5b29911562cd2D7CF by way of ethereum-rpc[.]publicnode[.]com; the contract can operate as a dead-drop resolver, enabling operators to replace C2 locations with out rebuilding and redistributing the malware.
Remus encrypts C2 configuration and stolen information utilizing ChaCha20, then exfiltrates info in levels utilizing separate requests.
This piecemeal mannequin means attackers might retain information already collected even when the endpoint detects the malware halfway by way of execution.
Organizations ought to deal with native AI credentials like high-value cloud secrets and techniques. API keys must be saved in managed secret shops relatively than browser profiles, chat-tool directories, supply repositories, or native plaintext configuration recordsdata.
Safety groups ought to rotate OpenAI, Anthropic, cloud, source-control, and pockets credentials after a suspected Remus an infection, revoke lively browser periods, and assessment AI-platform utilization logs for anomalous consumption.
Detection groups ought to monitor for suspicious eth_call JSON-RPC visitors to public Ethereum nodes, notably from workstations that should not have a enterprise have to work together with blockchain infrastructure.
They need to additionally examine pretend CAPTCHA workflows, sudden command execution spawned by browsers, anomalous COM-based file enumeration, and outbound staged HTTP POST visitors.
Blocking recognized Remus-related C2 infrastructure and monitoring Ethereum smart-contract resolver habits can additional enhance protection.
Reduce each SOC alert investigation by 21 min. Energy your SOC with immediate IOC context for quick response: Combine TI Lookup in your SOC